This one's mostly about getting our own detection logic right. Most tool updates are "we added more CVEs."…
Liam R. — Freelance Penetration Tester
This one's mostly about getting our own detection logic right.
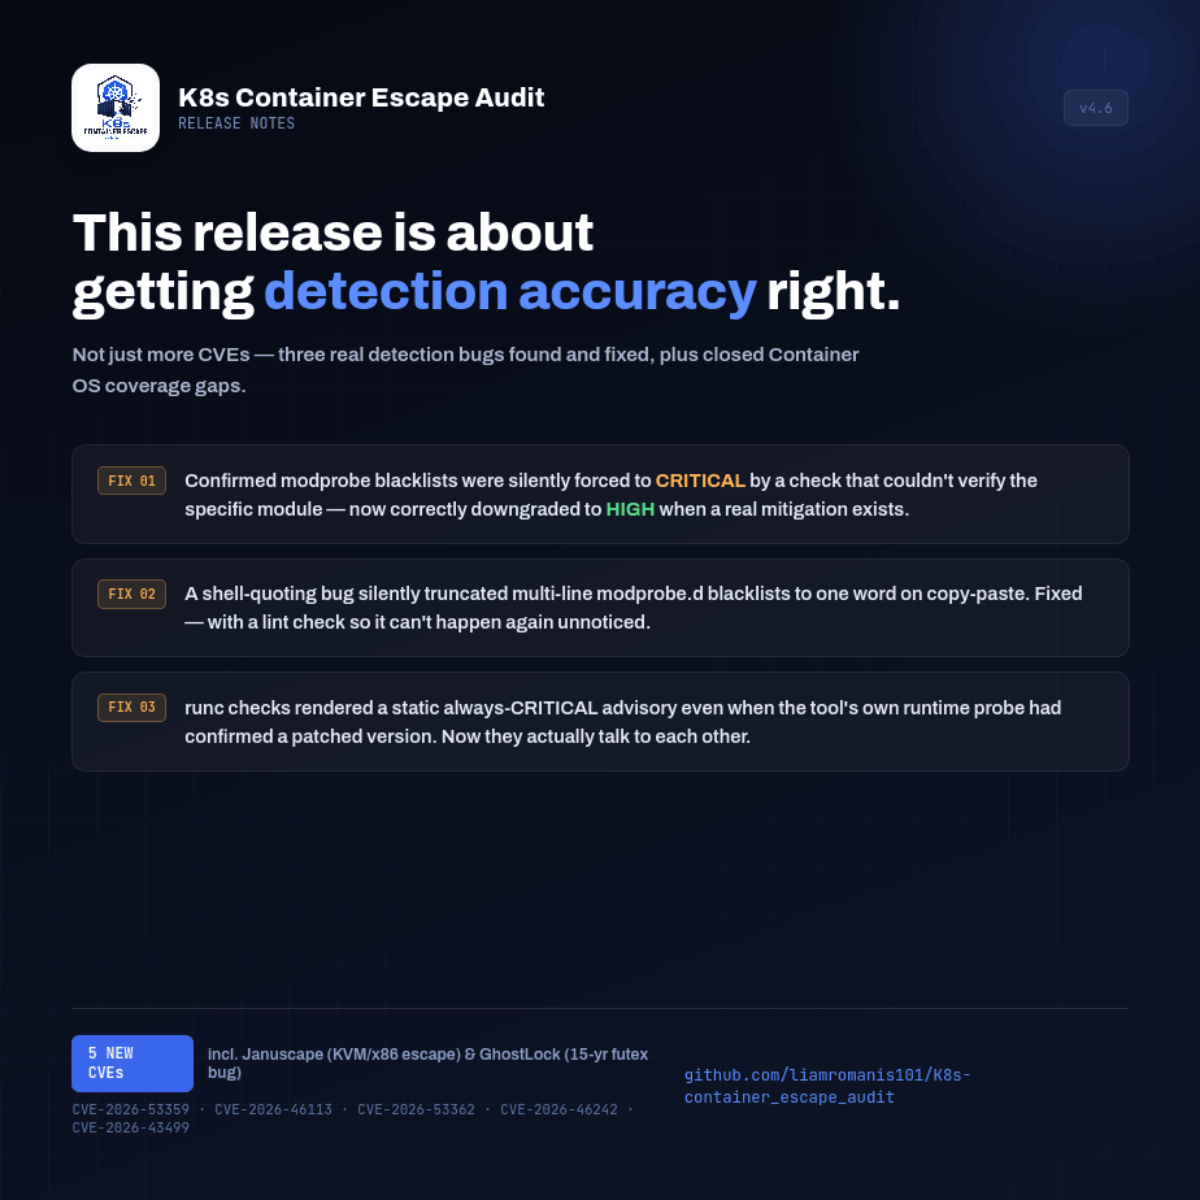
Most tool updates are "we added more CVEs." This release does that too (5 new entries, including Januscape, the first public KVM/x86 guest-to-host escape, and GhostLock, a 15-year-old futex bug), but the bigger news is three detection-accuracy bugs we found and fixed:
• A confirmed modprobe blacklist was being silently overridden to CRITICAL by a socket-reachability check that couldn't actually tell if the specific vulnerable module was blocked, now correctly downgraded to HIGH when a real mitigation is in place.
• Two mitigation commands in the CVE database had a subtle shell-quoting bug that silently truncated a multi-line modprobe.d blacklist to a single word when copy-pasted. Fixed, and added a lint check so it can't happen again unnoticed.
• The runc CVE checks were rendering a static, always-CRITICAL advisory even when the tool's own runtime probe had already confirmed a patched version elsewhere in the same scan. Now they actually talk to each other.
We also fixed real Container OS coverage gaps, Amazon Linux, SUSE, and OpenShift/RHCOS nodes were silently falling through to "unknown" due to /etc/os-release ID mismatches the engine never normalized.
If you're running this in production, it's worth pulling the update, not for the new CVEs, but because a couple of these bugs could have masked a real finding as mitigated when it wasn't.
• 5 New CVEs: CVE-2026-53359, CVE-2026-46113, CVE-2026-53362, CVE-2026-46242, CVE-2026-43499
🔗 github.com/liamromanis101/K8s-container_escape_audit
#Kubernetes #ContainerSecurity #DevSecOps #CloudSecurity #OpenSource #Januscape #Ghostlock #Bad_Epoll
3 reactions · 0 comments
Topics: #devsecops, #kubernetes, #cloudsecurity, #containersecurity, #opensource, #ghostlock, #januscape, #bad_epoll