Quick cybersecurity reality check: Buying a SIEM does not mean you are secure. Out of the box, most security…
SILVIA S. — Director, Security & Infrastructure Solutions
Reshared from a post by Ikechukwu O.
Quick cybersecurity reality check: Buying a SIEM does not mean you are secure.
Out of the box, most security monitoring tools are completely blind to unique business and application logic. If you aren't actively engineering your detections, you're blind to real threats.
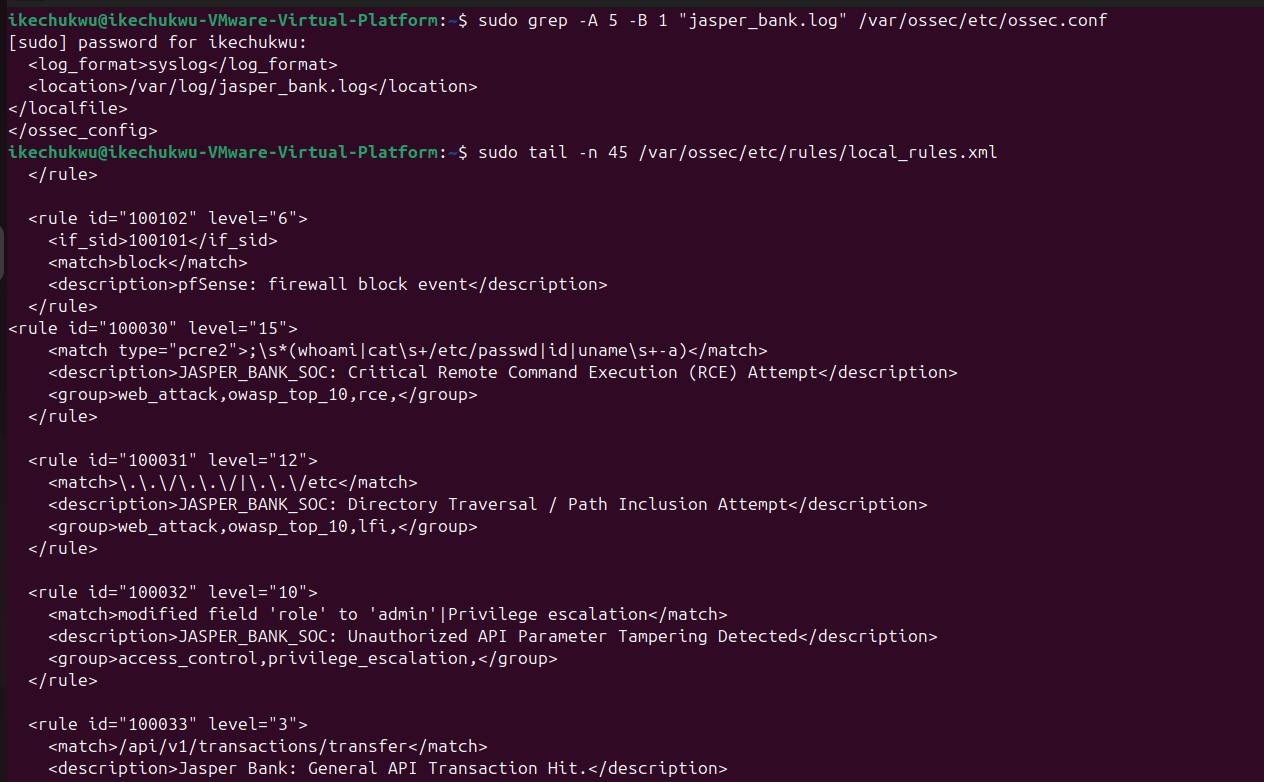
I recently ran a project simulating a fintech ecosystem to put this to the test. By building custom log ingestion pipelines and authoring targeted XML signatures, I configured the environment to catch high-severity exploits like RCE, SQLi, and API parameter tampering that standard signatures missed entirely.
The biggest takeaway? The true value of a modern SOC isn't the platform you deploy; it's the custom engineering and systematic tuning you do under the hood to eliminate false positives and catch true attacks.
the JASPER_BANK is an intentional vulnerable web application I designed with AI for simulation and never a real infrastuture. 😊
Back to building. 💻🔥
#DetectionEngineering #Cybersecurity #SIEM #Wazuh #BlueTeam #SOC #Fintech
1 reactions · 0 comments