New release: K8s-container_escape_audit v4.7.6 — two new container-escape / LPE checks. Both of these are…
Liam R. — Freelance Penetration Tester
New release: K8s-container_escape_audit v4.7.6 — two new container-escape / LPE checks.
Both of these are local-root bugs that matter inside containers, not just on desktops:
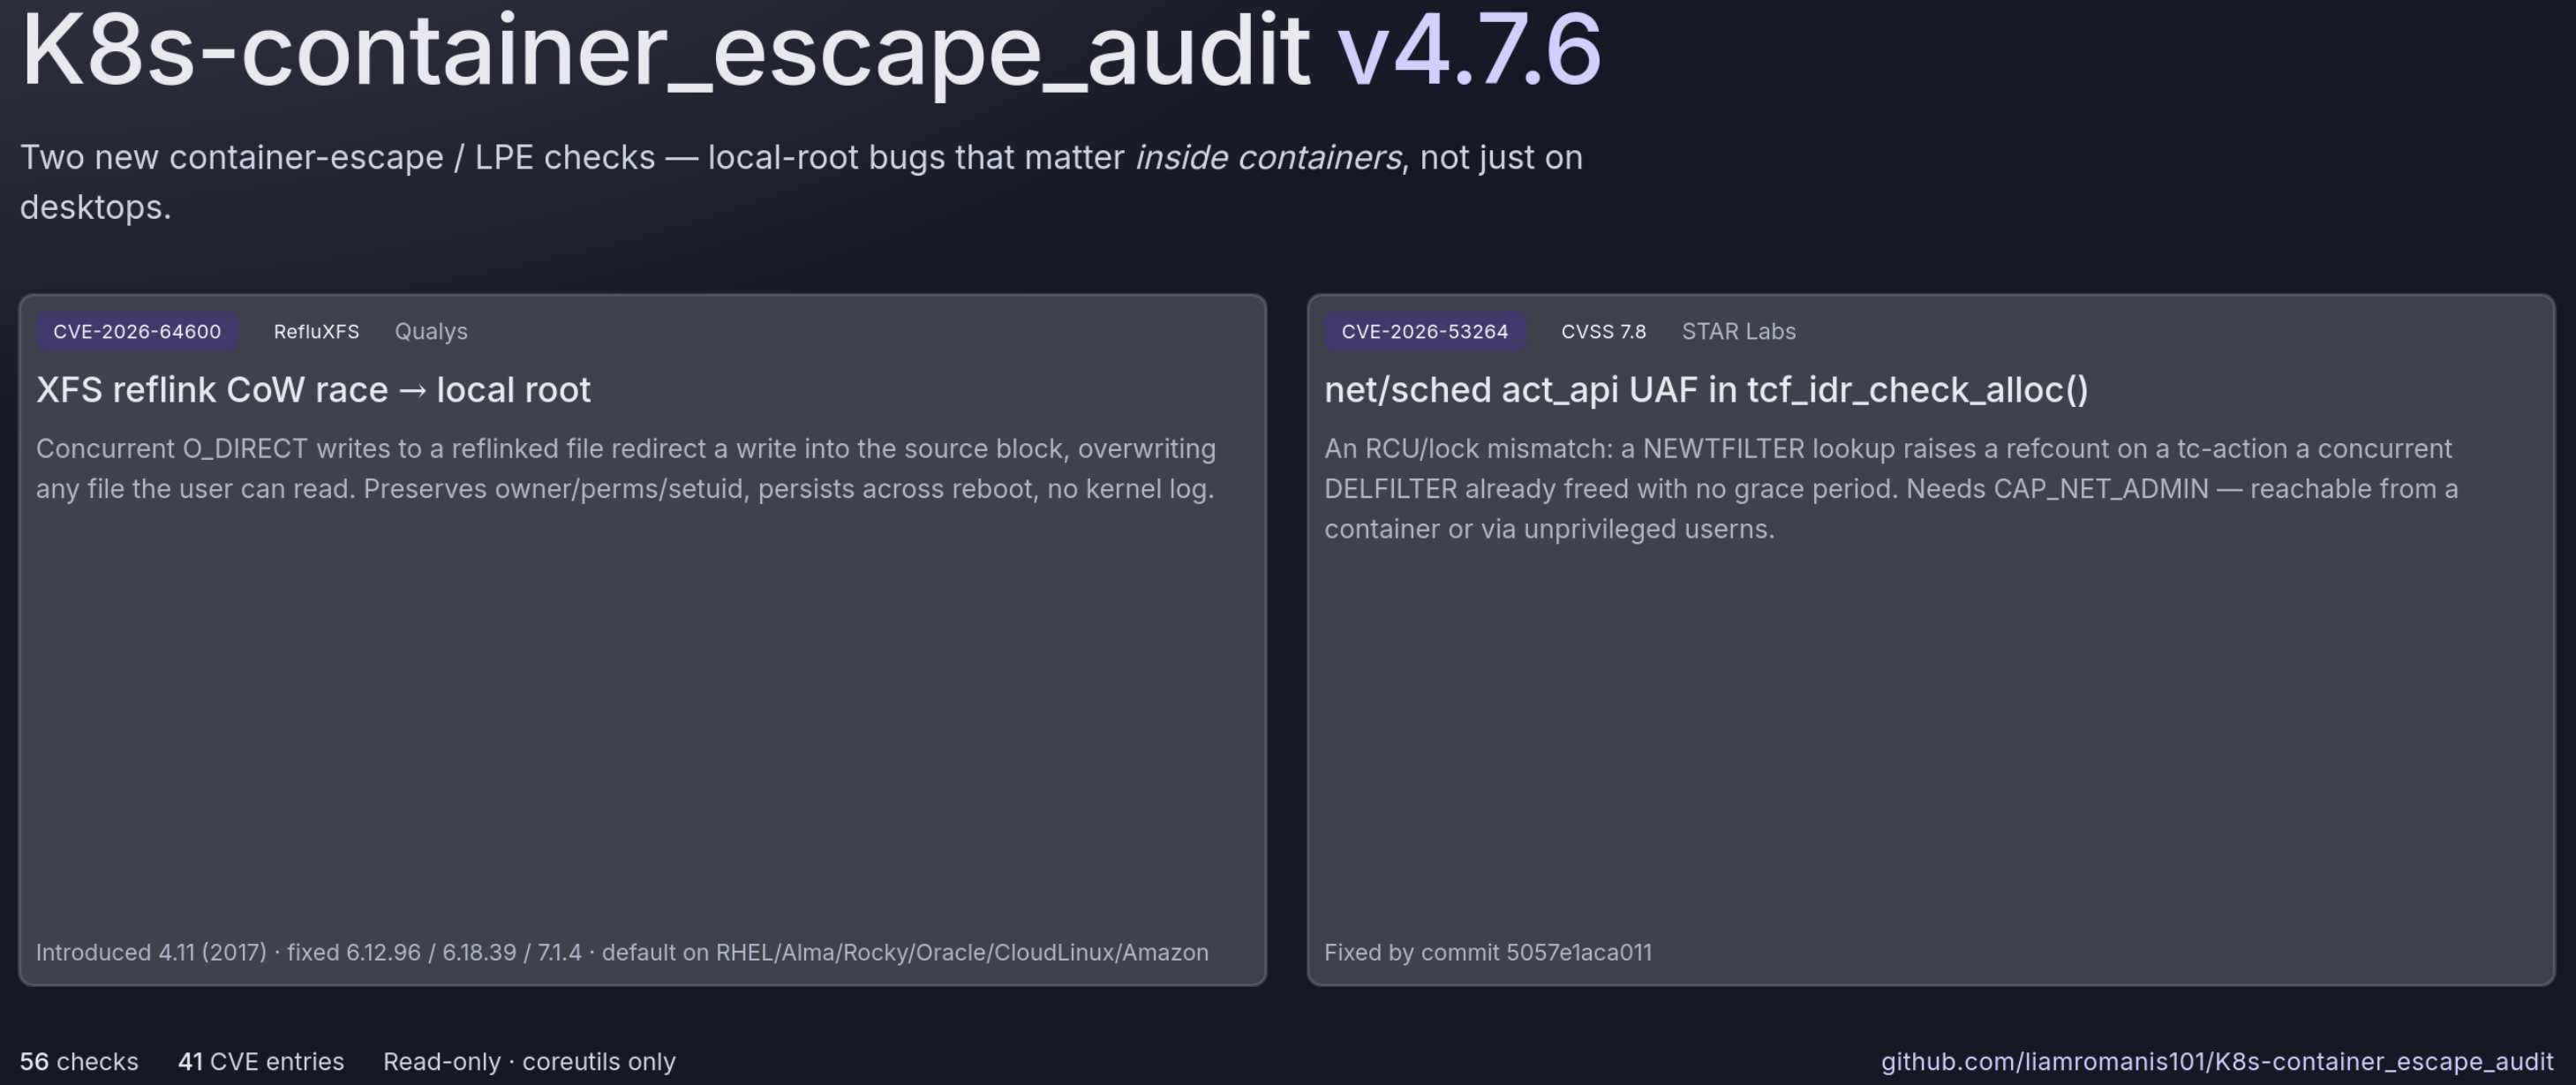
▸ CVE-2026-64600 (RefluXFS) — XFS reflink CoW race (Qualys). Concurrent O_DIRECT writes to a reflinked file let an unprivileged user redirect a write back into the source block, overwriting any file they can read → root. Preserves owner/perms/setuid, persists across reboot, no kernel log. Introduced in 4.11 (2017); fixed 6.12.96 / 6.18.39 / 7.1.4. Precondition is the filesystem: XFS with reflink=1 (mkfs.xfs default since 2019; default across RHEL/Alma/Rocky/Oracle/CloudLinux/Amazon).
▸ CVE-2026-53264 — net/sched act_api UAF in tcf_idr_check_alloc() (STAR Labs, CVSS 7.8). RCU/lock mismatch: a NEWTFILTER lookup raises a refcount on a tc-action that a concurrent DELFILTER already freed with no grace period. Needs tc-config access (CAP_NET_ADMIN) — reachable from a container directly or via unprivileged userns. Fixed by commit 5057e1aca011.
Tool changes:
Check 55 (check_xfs_reflink_exposure): parses /proc/mounts + read-only xfs_info to flag reachable reflink=1 XFS volumes
Check 56 (check_netsched_actapi_uaf): CapEff parse for CAP_NET_ADMIN + unprivileged-userns route + act_gact/cls_flower availability
CVE DB → 41 entries; 56 checks total
Version engine stays conservative on distro kernels (defer-to-vendor rather than a wrong verdict from upstream numbers)
Read-only, no dependencies beyond coreutils. Feedback / PRs welcome.
https://github.com/liamromanis101/K8s-container_escape_audit
2 reactions · 0 comments