Yesterday, I had the privilege of facilitating another amazing hands-on training session. We covered the…
Innocent A. — Cybersecurity Analyst
Yesterday, I had the privilege of facilitating another amazing hands-on training session.
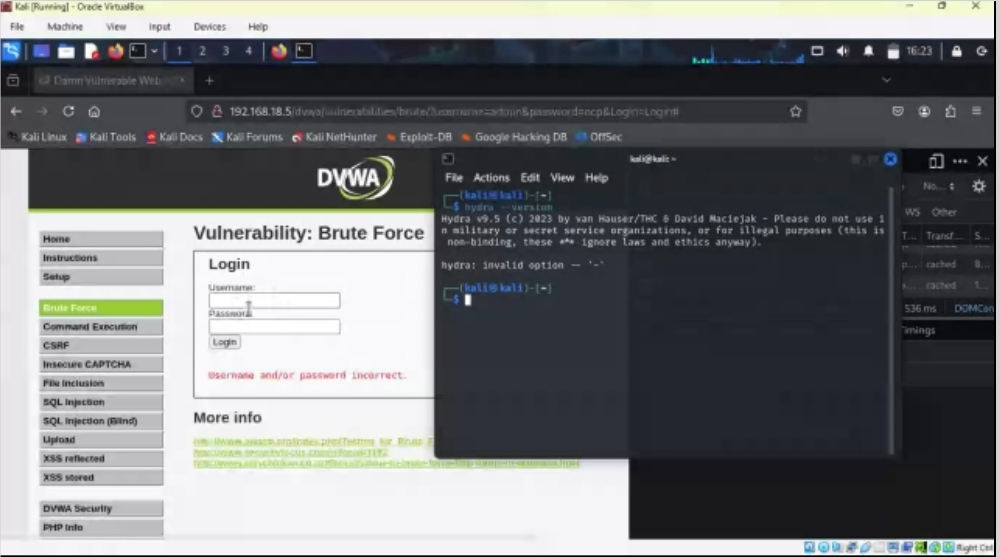
We covered the OWASP Top 10, installed OWASP Broken Web Applications on VirtualBox, and conducted a brute force attack on DVWA. We also carried out SQL injection and command execution attacks. The goal is to give our students the hands-on experience needed to protect assets from these kinds of attacks.
Our next class will complete this lesson by installing a Web Application Firewall and a simple SIEM tool for log analytics. This is what hands-on learning looks like.
This Saturday, our students will be presenting their assignments on honeypot installation and attack, as well as the network topology they built on Cisco Packet Tracer. Super excited about this.
If you want to join the CyberShift Intensive hands-on cybersecurity training, send me a DM and I'll plug you in ASAP.
2 reactions · 0 comments