Open-sourced a CORS testing toolkit that tells you whether a misconfiguration is actually exploitable — not…
Liam R. — Freelance Penetration Tester
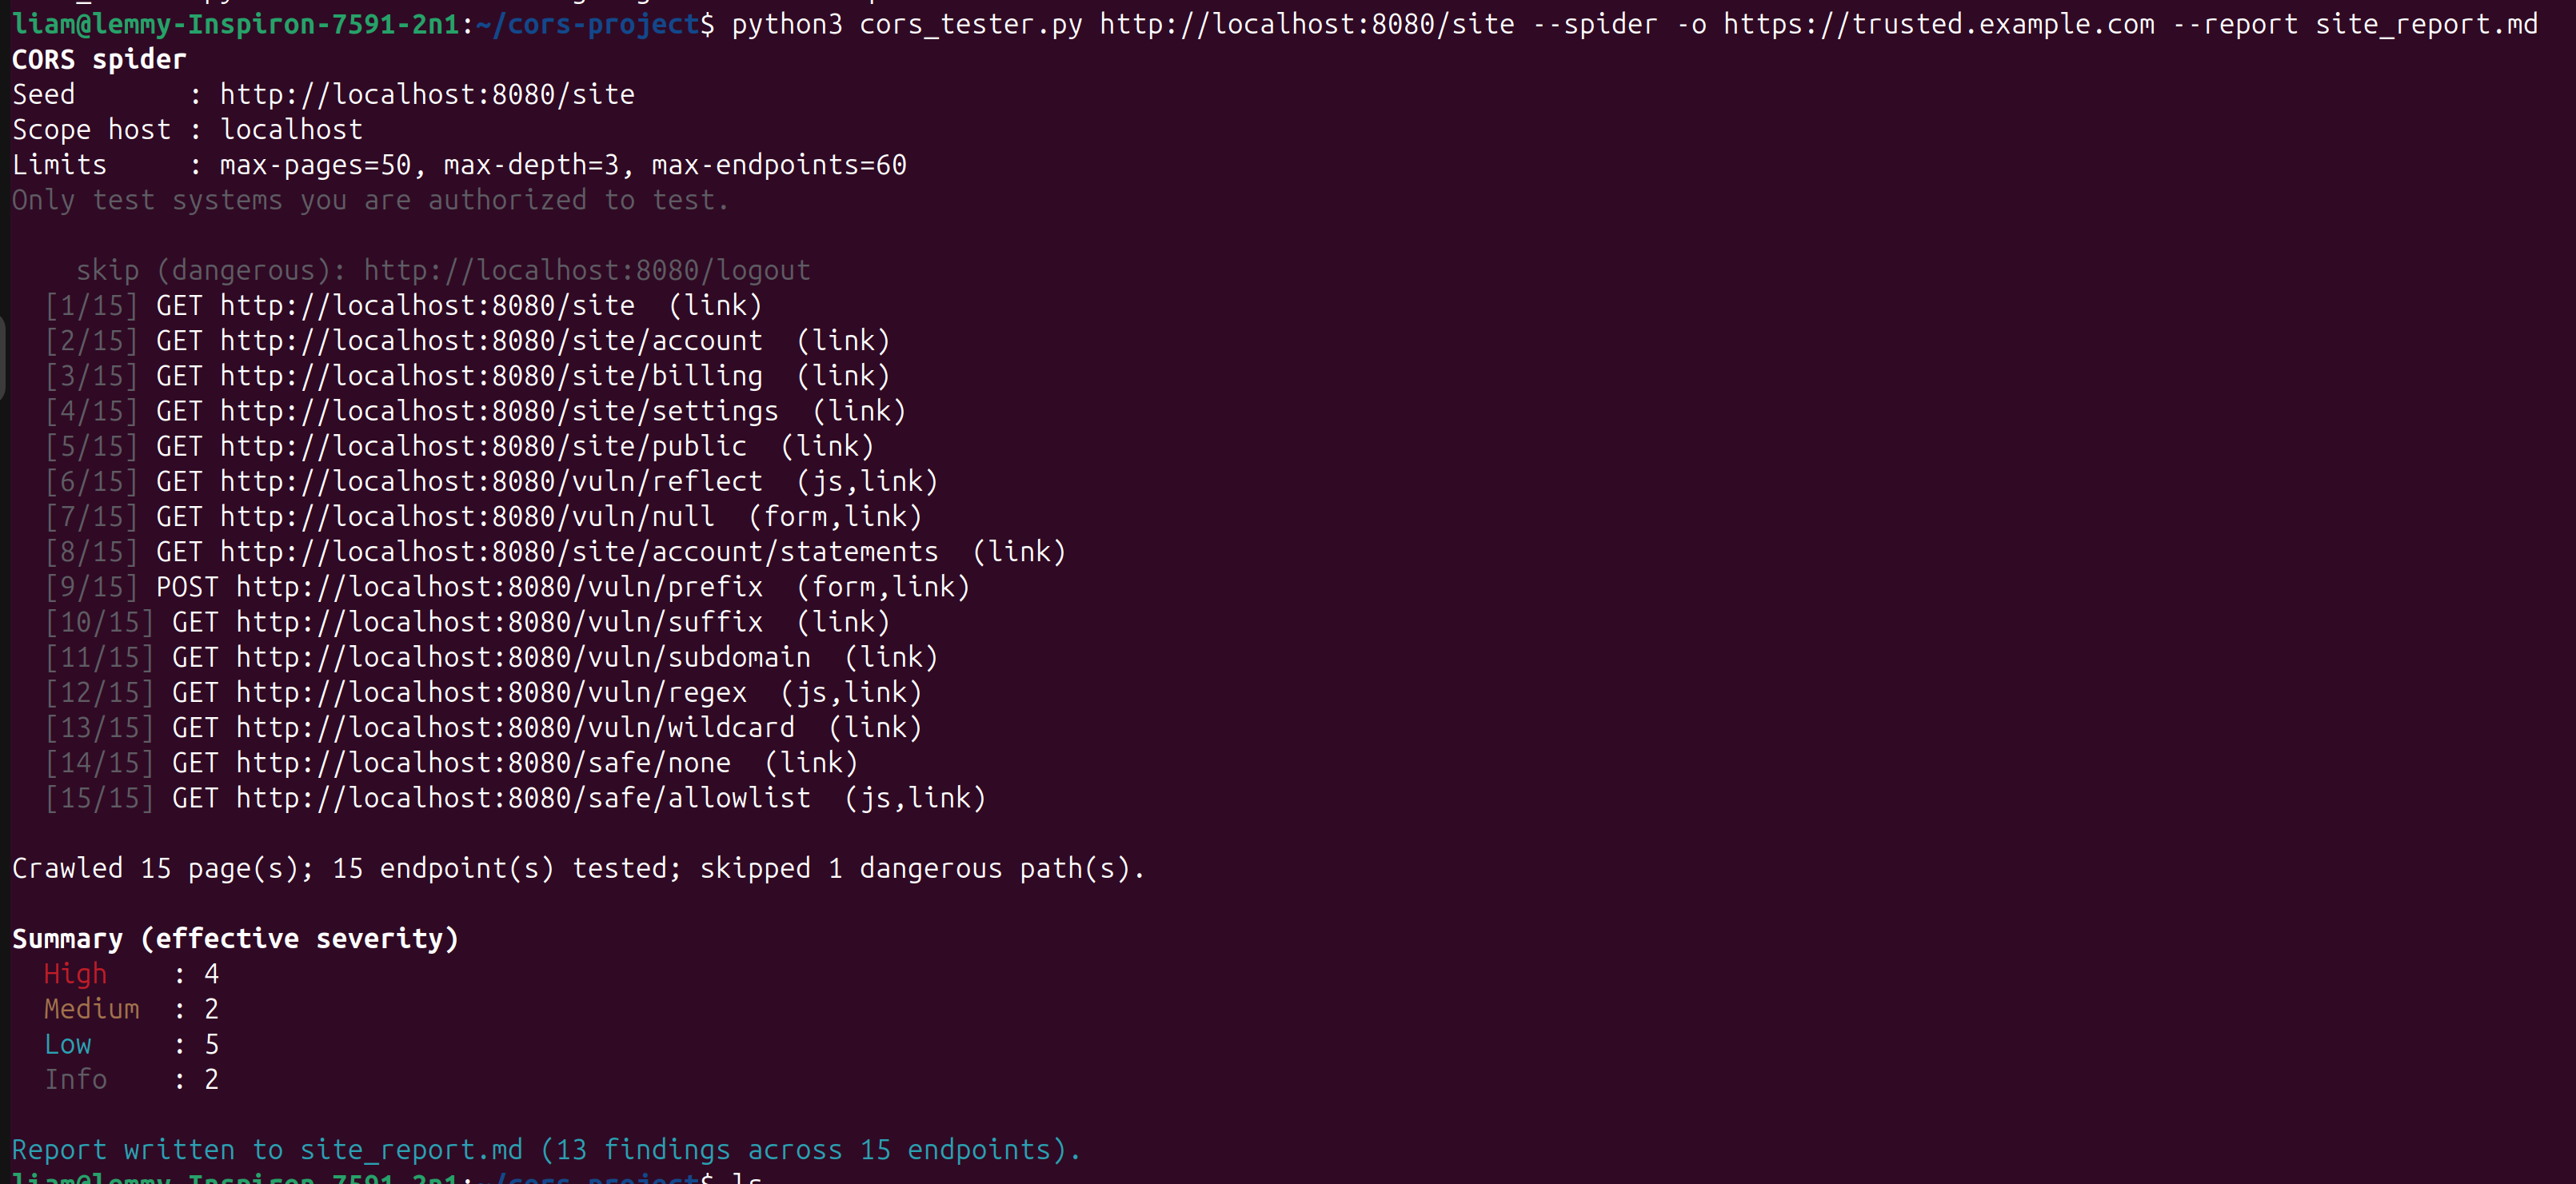
Open-sourced a CORS testing toolkit that tells you whether a misconfiguration is
actually exploitable — not just that a header is weak. It checks SameSite,
cookie-vs-bearer auth, and whether the endpoint returns anything sensitive, then
rates each finding by real impact (base vs effective severity). 17 checks incl.
parser confusion, Private Network Access, and localhost trust; detects when a
CORS flaw exposes CSRF tokens; ships with a Docker lab to try it safely.
Repo: https://github.com/liamromanis101/cors-project
· Apache-2.0 · authorized testing only.
#AppSec #CORS #WebSecurity #InfoSec #OpenSource
1 reactions · 0 comments
Topics: #websecurity, #opensource, #infosec, #appsec, #cors