Most websites are not getting hacked because of “advanced attacks”… They’re getting exposed because of the…
Innocent A. — Cybersecurity Analyst
Most websites are not getting hacked because of “advanced attacks”…
They’re getting exposed because of the basics.
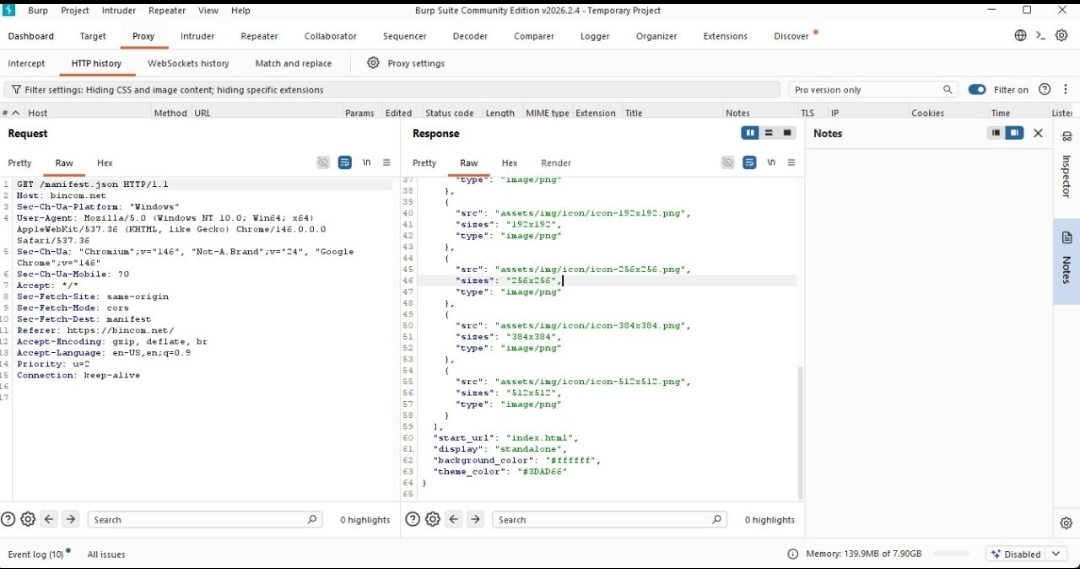
I recently analyzed a simple HTTP response from a live web application, and here’s what stood out:
- No Content Security Policy
- No HSTS
- No X-Frame-Options
- No X-Content-Type-Options
Just a clean response… but completely unprotected.
Even worse?
The server openly revealed it was running Apache.
This is how attackers think:
Not “How do I break in?”
But “What have they forgotten to protect?”
And most times, the answer is:
👉 Security headers
👉 Cookie flags
👉 Information leakage
These are not complex fixes.
Adding the right headers can:
Prevent XSS attacks
Stop clickjacking
Enforce HTTPS
Reduce attack surface significantly
Yet, they are often ignored.
If you’re a developer, security engineer, or even a founder, here’s a simple reminder:
Before chasing advanced security tools…
Fix the fundamentals.
Because in cybersecurity,
what you ignore is often what gets exploited.
#CyberSecurity #WebSecurity #AppSec #Infosec #EthicalHacking #SecurityAwareness
5 reactions · 0 comments
Topics: #websecurity, #ethicalhacking, #infosec, #appsec, #securityawareness, #cybersecurity