container_escape_audit.sh v4.7.7 — deeper AppArmor & SELinux coverage Most tooling answers one question…
Liam R. — Freelance Penetration Tester
container_escape_audit.sh v4.7.7 — deeper AppArmor & SELinux coverage
Most tooling answers one question about mandatory access control: is AppArmor/SELinux switched on? The problem is that "on" hides a lot. A profile in complain mode logs policy violations but allows them, to anything checking only whether a profile is applied, it looks protected while providing no access control at all. SELinux reporting Enforcing tells you nothing if the process is running in spc_t or unconfined_t. And a system can have all the MAC userspace and config in place while no MAC LSM is actually loaded in the kernel.
v4.7.7 adds three read-only checks that move from "is it on?" to "on in what mode, confining me to what, with which escape-relevant relaxations?":
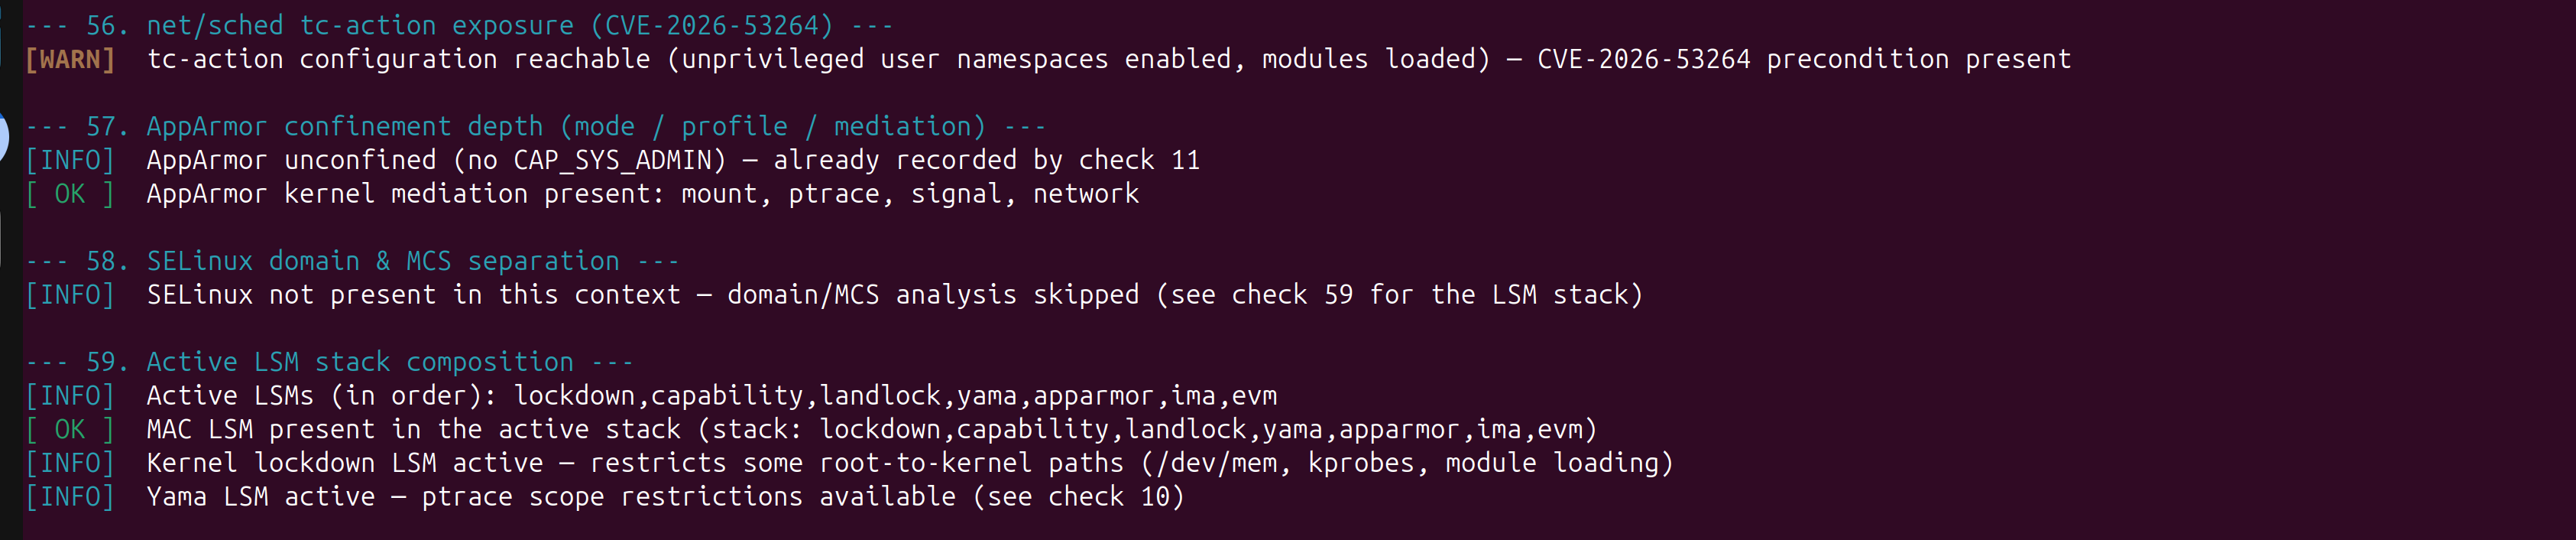
Check 57 — AppArmor confinement depth. Separates enforce / complain / unconfined; flags unconfined + CAP_SYS_ADMIN as the precondition pairing behind several escape vectors; distinguishes the runtime-default profile from a bespoke one; and checks whether the kernel actually compiled in mount/ptrace/signal mediation (a profile's mount-deny rules are inert without it).
Check 58 — SELinux domain & MCS. Reads the process domain, not just the mode: spc_t/unconfined_t are effectively unconfined despite Enforcing. Flags a container domain with no MCS category pair (host confinement intact, inter-container isolation gone) and inspects the escape-relevant booleans that can loosen container_t without changing the domain.
Check 59 — active LSM stack composition. Reads /sys/kernel/security/lsm and catches the "installed but not enforcing" gap; MAC tooling present, but no MAC LSM in the active kernel stack.
There's also a cross-reference worth calling out: when the runc check detects CVE-2025-52881, checks 57 and 58 downgrade an otherwise-enforcing profile or domain to "present but bypassable", so an enforce-mode result is never over-trusted while the runtime is unpatched.
Everything is strictly read-only — no links, mounts, or writes. Check count 56 → 59; CVE database unchanged.
Repo and full changelog: github.com/liamromanis101/K8s-container_escape_audit
1 reactions · 0 comments