📢 Shared from CyberShift Just dropped my live walkthrough of the TryHackMe Incident Response Process room…
Innocent A. — Cybersecurity Analyst
📢 Shared from CyberShift
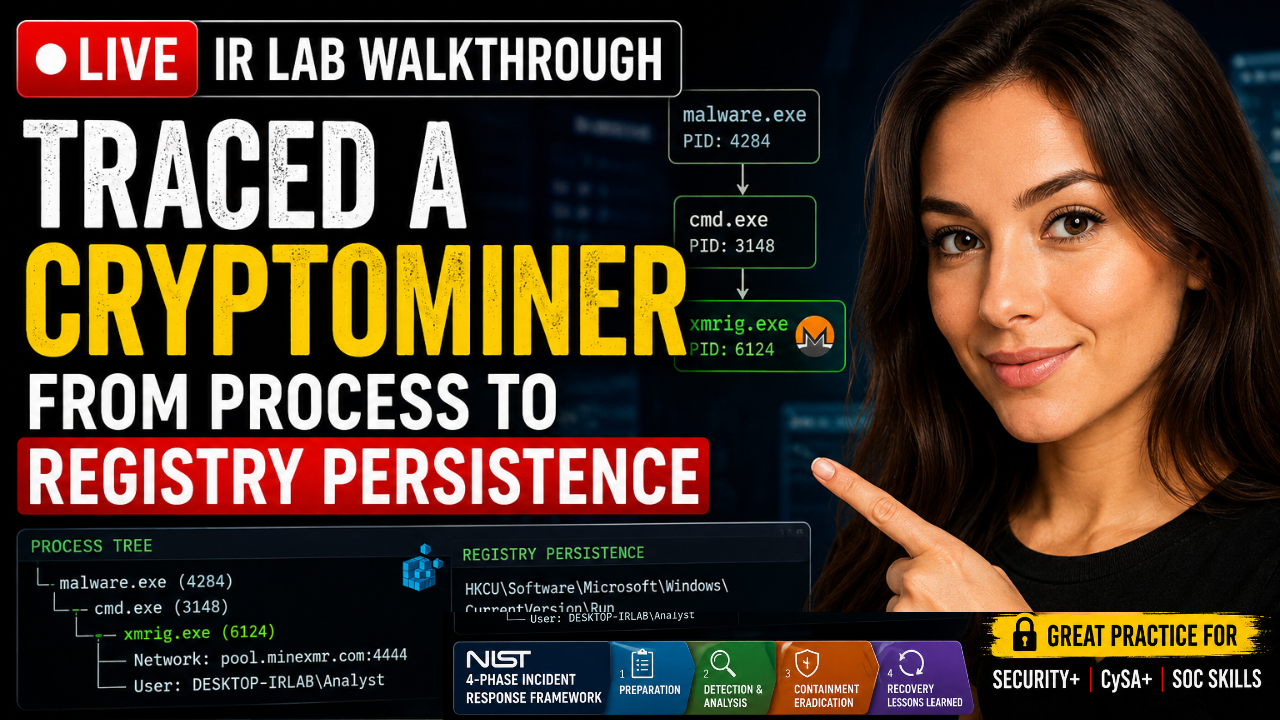
Just dropped my live walkthrough of the TryHackMe Incident Response Process room. We go through a real cryptominer infection, trace the C2 server, hunt down the registry persistence key, and eradicate it using the NIST IR Framework. Full video on my YouTube channel, link in the comments. #IncidentResponse #SOCAnalyst #TryHackMe #BlueTeam #CyberSecurity
0 reactions · 0 comments
Topics: #tryhackme, #blueteam, #incidentresponse, #socanalyst, #cybersecurity