Posted in Vulnerability Management
Fragnesia (CVE-2026-46300) is being actively exploited. Is your Linux estate exposed? CISA added Fragnesia…
Liam R. — Freelance Penetration Tester
Fragnesia (CVE-2026-46300) is being actively exploited. Is your Linux estate exposed?
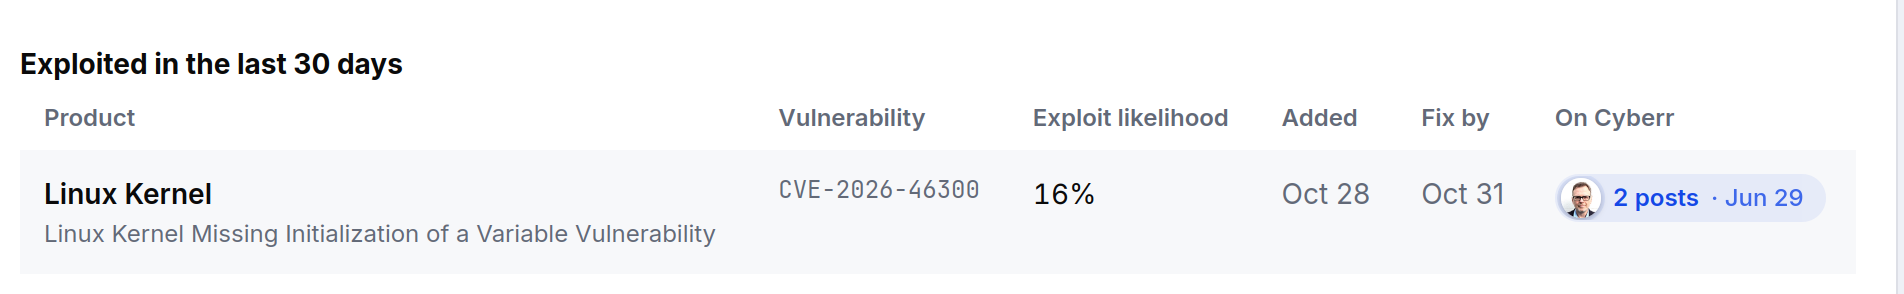
CISA added Fragnesia to its Known Exploited Vulnerabilities catalog on 28 October. This Linux kernel flaw lets a low-privileged local user write to the page cache of read-only files and gain root.
It can’t be exploited remotely on its own, but attackers are now chaining it with PHP2Shell (CVE-2026-109618 and CVE-2026-109619). Dream Security reports that this took them from unauthenticated remote code execution to root on 25 devices.
K8s-container_escape_audit has covered Fragnesia for some time. It’s built to find container escapes, but it can be used on any Linux system to check:
* Kernel version: a distro-aware CVE verdict that says when a version string can’t prove a backported fix
* Loaded modules: whether the affected ESP modules are actually loaded
* Blacklisting: whether those modules are blocked in /etc/modprobe.d
* Live patching: whether an agent could make uname -r misleading
Here’s an example from a system with the modules blocked:
*[WARN] CVE-2026-46300 (Fragnesia ESP): kernel patch status defer (not confirmed fixed) — verify
. Version verdict: ubuntu: consult ubuntu.com/security/CVE-2026-46300 — backport status not derivable from version string
+ Module loaded (/proc/modules): none of [esp4 esp6] present in /proc/modules
+ Module blacklist (/etc/modprobe.d): all of [esp4 esp6] blacklisted via 'install ... /bin/false'
[MEDIUM ] Fragnesia ESP (CVE-2026-46300) — MEDIUM [ITW] [CISA-KEV]*
The modules are blocked, but the kernel fix still isn’t confirmed, so the tool asks you to verify it rather than reporting a pass.
Run it on the host to check blacklisting, because inside a container it reads the image’s configuration, not the host’s. On a host, focus on the CVE and kernel results, as some container checks won’t apply.
Our recommendations
* Install your distro’s fixed kernel and reboot, then confirm the running kernel is the fixed version.
* Treat an inconclusive result as unpatched until your vendor’s tracker confirms the fix.
* If you can’t patch yet, block and unload esp4 and esp6. This breaks IPsec, so check VPN use first.
* Patch PHP and any appliances that embed it, as PHP2Shell is the current route in. Older branches may need a vendor fix.
* Check exposed systems for webshells. Fragnesia alters the page cache rather than the file on disk, so integrity tools may miss it.
The tool is free for personal use. Download an SLSA verified release here: https://github.com/liamromanis101/K8s-container_escape_audit and then update the cve_checks.conf database.
1 reactions · 0 comments