BSides Maine: Community, Malware, and Identity Residue Spent an awesome day volunteering and connecting at…
Haydn K. — Lead Community Operator
BSides Maine: Community, Malware, and Identity Residue
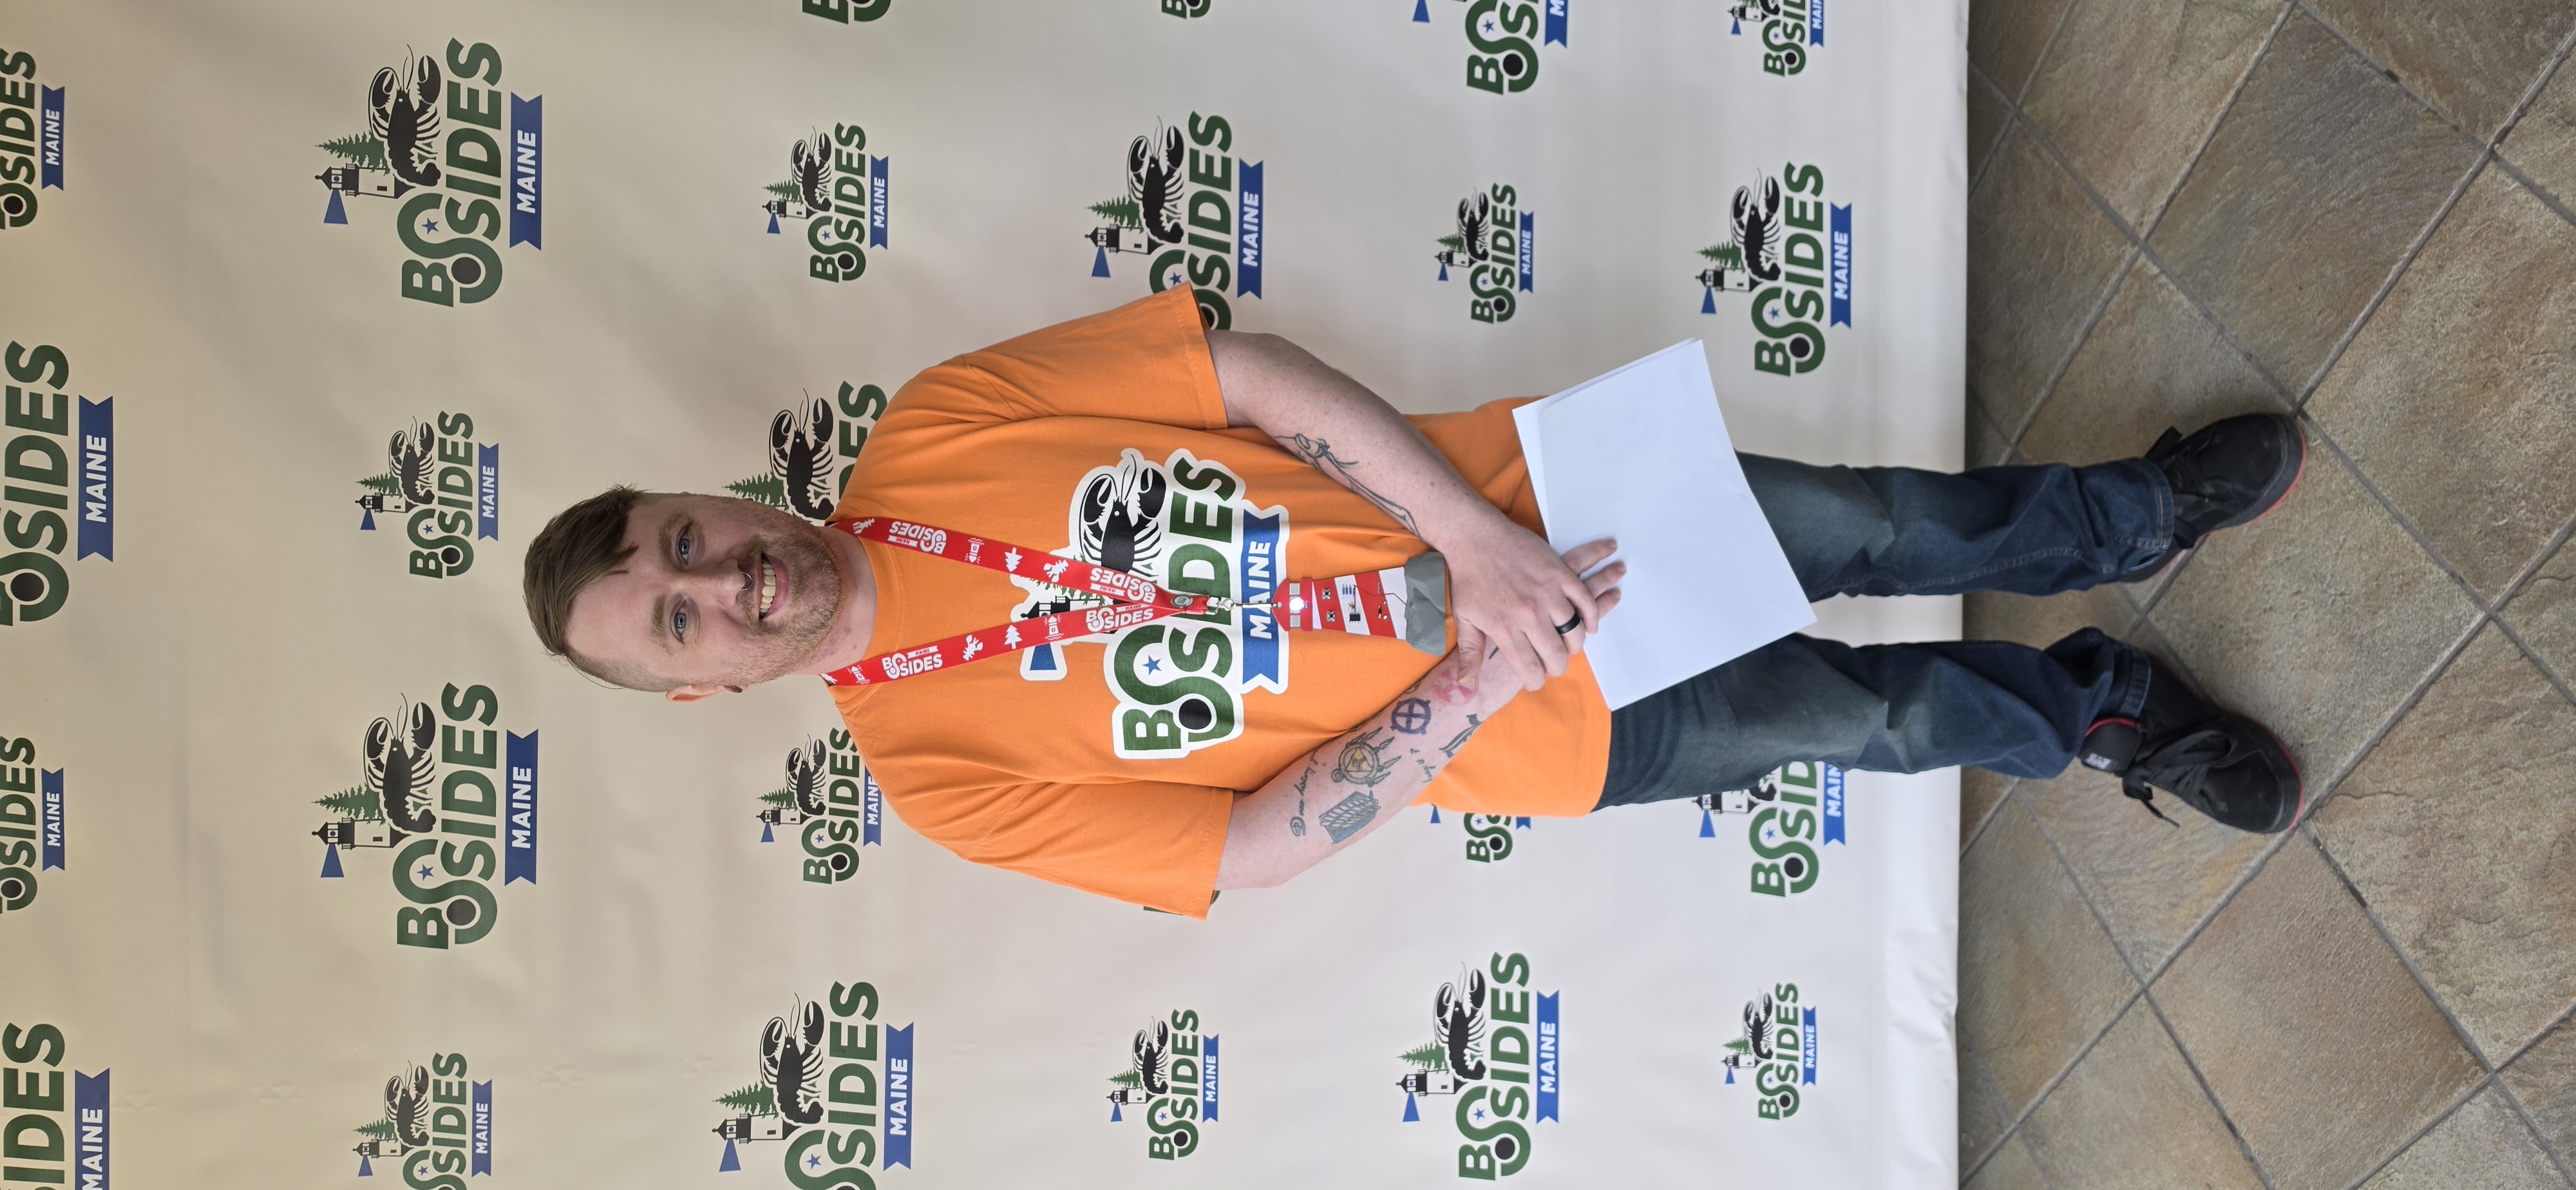
Spent an awesome day volunteering and connecting at the inaugural BSides Maine. Taking part as an auditorium logistics volunteer was a fantastic experience, and the event brought together an incredible mix of technical depth and community focus. Here are the major highlights and takeaways that stood out the most.
Exploding npm Malware Trends
Dipendu Kar and Derian Tenglein gave a great presentation on software supply chain security. The statistics are wild: in 2023, around 5,000 npm packages were removed for being malicious. By 2025, that number skyrocketed to over 500,000 malicious packages out of 4.8 million live packages.
Attackers heavily abuse the single-function dependency nature of npm to inject malicious code via typosquatting, dependency confusion, and maintainer account takeovers.
Many payloads trigger instantly via auto-running pre- or post-install scripts.
While AI tools like ChatGPT and Claude are great at decoding bundled binaries, obfuscated and minified code still present massive static analysis detection gaps.
Key blue team defenses include pinning package versions and utilizing flags like ignore-scripts to prevent auto-running code during installation.
Hunting Identity Residue with ProfileHound
Christopher Haller shared some excellent work on post-compromise escalation and identity security. He introduced ProfileHound, a tool built on the OpenGraph framework that extends classic BloodHound functionality.
Traditional BloodHound uses the HasSession edge, which only logs active, live user logons.
ProfileHound queries the C$ share on domain machines (requiring local admin) to map a new edge called HasUserProfile.
By analyzing the existence and timestamps of user profile directories, defenders and red teamers can visually pinpoint the most heavily used profiles. This allows teams to triage and find high-value identity residue like persistent browser data, long-term session cookies that bypass MFA, DPAPI blobs, and notepad backups.
Mindsets and Hardware Hacking
Jayson E Street gave a phenomenal keynote on physical social engineering. He emphasized that threat actors will exploit anyone trying to be helpful, meaning strict adherence to security rules is vital even when someone claims they urgently need help.
Caught the end of Matt Davis's embedded camera hacking session. Seeing the live terminal process the firmware dump and hit the final confirmation screen was an awesome proof of concept to watch in person.
Proactive Networking is a Game Changer
The vendor kiosks provided a great lesson in the power of building connections. I spent time talking shop with representatives from companies like Deer Brook Consulting, Defendify, Rapid7, IntegSec, TrustedSec, OWASP Maine, and the ISC2 Maine Chapter.
If you are heading to a conference soon, removing the friction from sharing your background makes a massive difference:
LinkedIn QR Wallpaper: Setting my phone background to my LinkedIn QR code made connecting instant.
Portfolio Stickers: I handed out custom stickers for my SleuthHound repository that included a QR code and a quick project description, which made a unique icebreaker.
Mobile Resume: Keeping my resume file instantly accessible on my phone meant I could fill out and submit a complete job application email right from the conference floor when an opportunity came up.
Overall, it was a stellar event that brought a ton of value for both technical insights and community building. I am looking forward to applying these defensive concepts to my upcoming lab projects.
2 reactions · 4 comments
Comments
Samantha S.: Love this! Volunteering is the best - thank you for sharing and for helping the community! 💖
Samantha S.: Also you inspired a post on this too - our platform has the connection QR code with your referral code baked in automatically :)
Haydn K.: Samantha Swift thank you! It really was a great way to give back, learn lots, and meet a lot of people in the local market!
Haydn K.: Samantha Swift oh wow, that's awesome! Thank you so much, I really appreciate the shoutout and I'm glad the post inspired you:) That's a really cool feature to have baked in, I didn't know about that!