Updated the CVE database in K8s-container_escape_audit with three new Linux kernel issues worth checking…
Liam R. — Freelance Penetration Tester
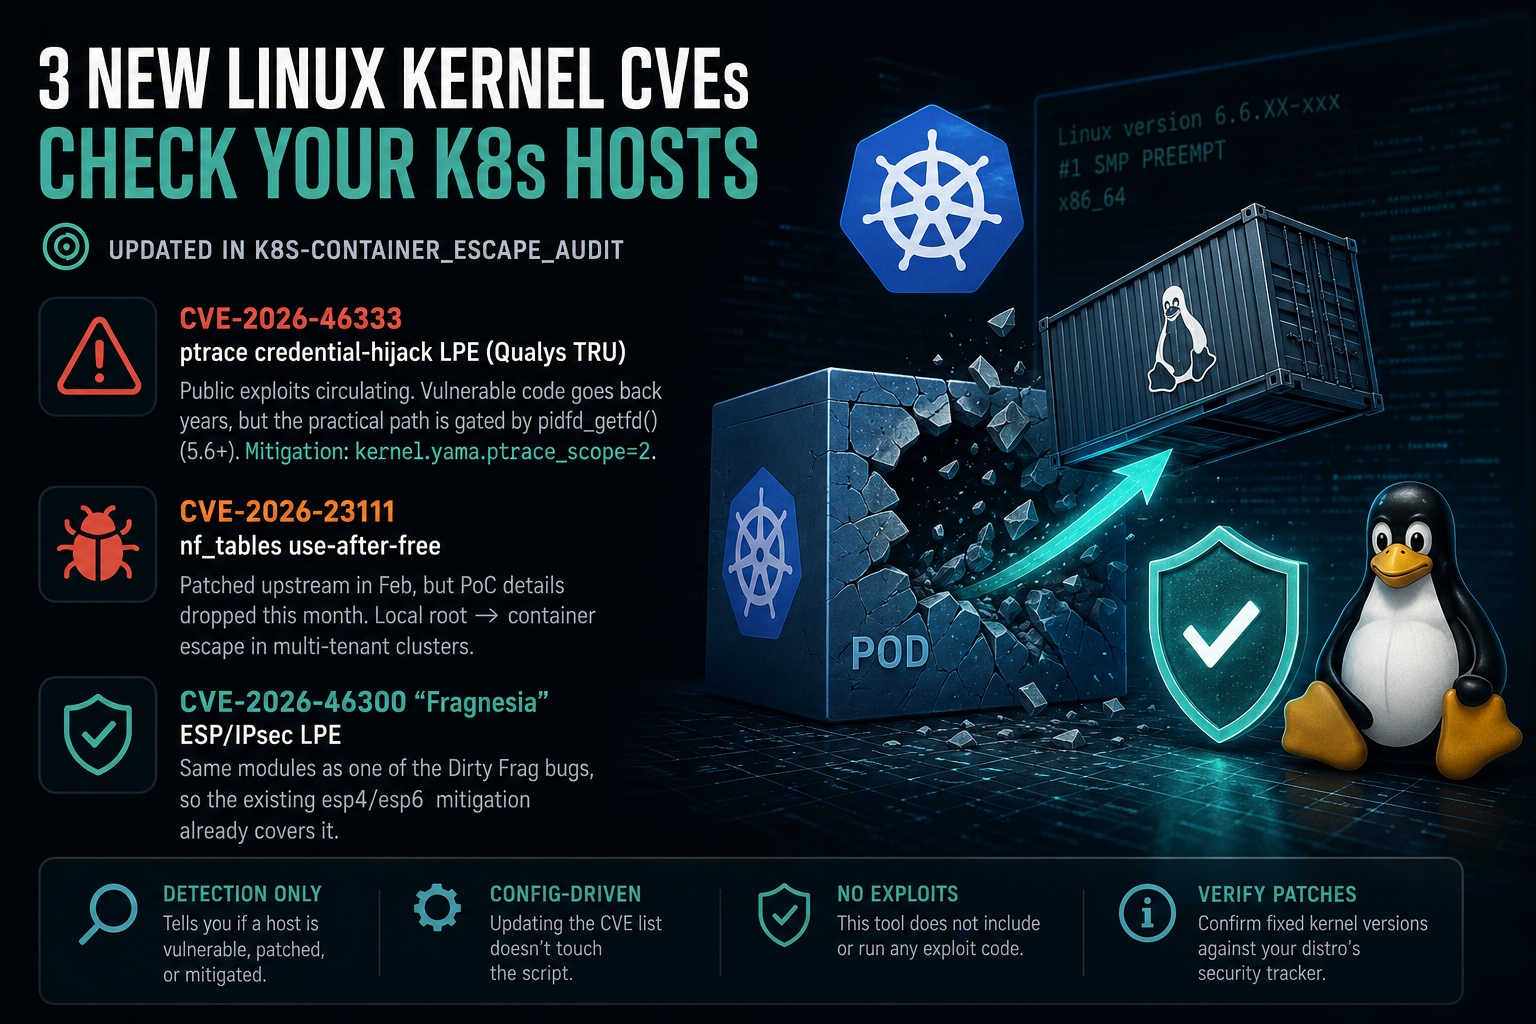
Updated the CVE database in K8s-container_escape_audit with three new Linux kernel issues worth checking your hosts against:
🔹 CVE-2026-46333 — ptrace credential-hijack LPE (Qualys TRU). Public exploits circulating. Vulnerable code goes back years, but the practical path is gated by pidfd_getfd() (5.6+). Mitigation: kernel.yama.ptrace_scope=2.
🔹 CVE-2026-23111 — nf_tables use-after-free. Patched upstream in Feb, but PoC details dropped this month. Local root → container escape in multi-tenant clusters.
🔹 CVE-2026-46300 "Fragnesia" — ESP/IPsec LPE. Same modules as one of the Dirty Frag bugs, so the existing esp4/esp6 mitigation already covers it.
As always, the tool is detection-only — it tells you whether a host is vulnerable, patched, or mitigated. No exploit code. One note: confirm the fixed kernel versions against your distro's security tracker before trusting any "patched" verdict — backports vary by vendor.
Checks are config-driven, so updating the CVE list doesn't touch the script.
https://github.com/liamromanis101/K8s-container_escape_audit
#linux #kubernetes #containers #security #devsecops
3 reactions · 0 comments
Topics: #devsecops, #kubernetes, #security, #containers, #linux