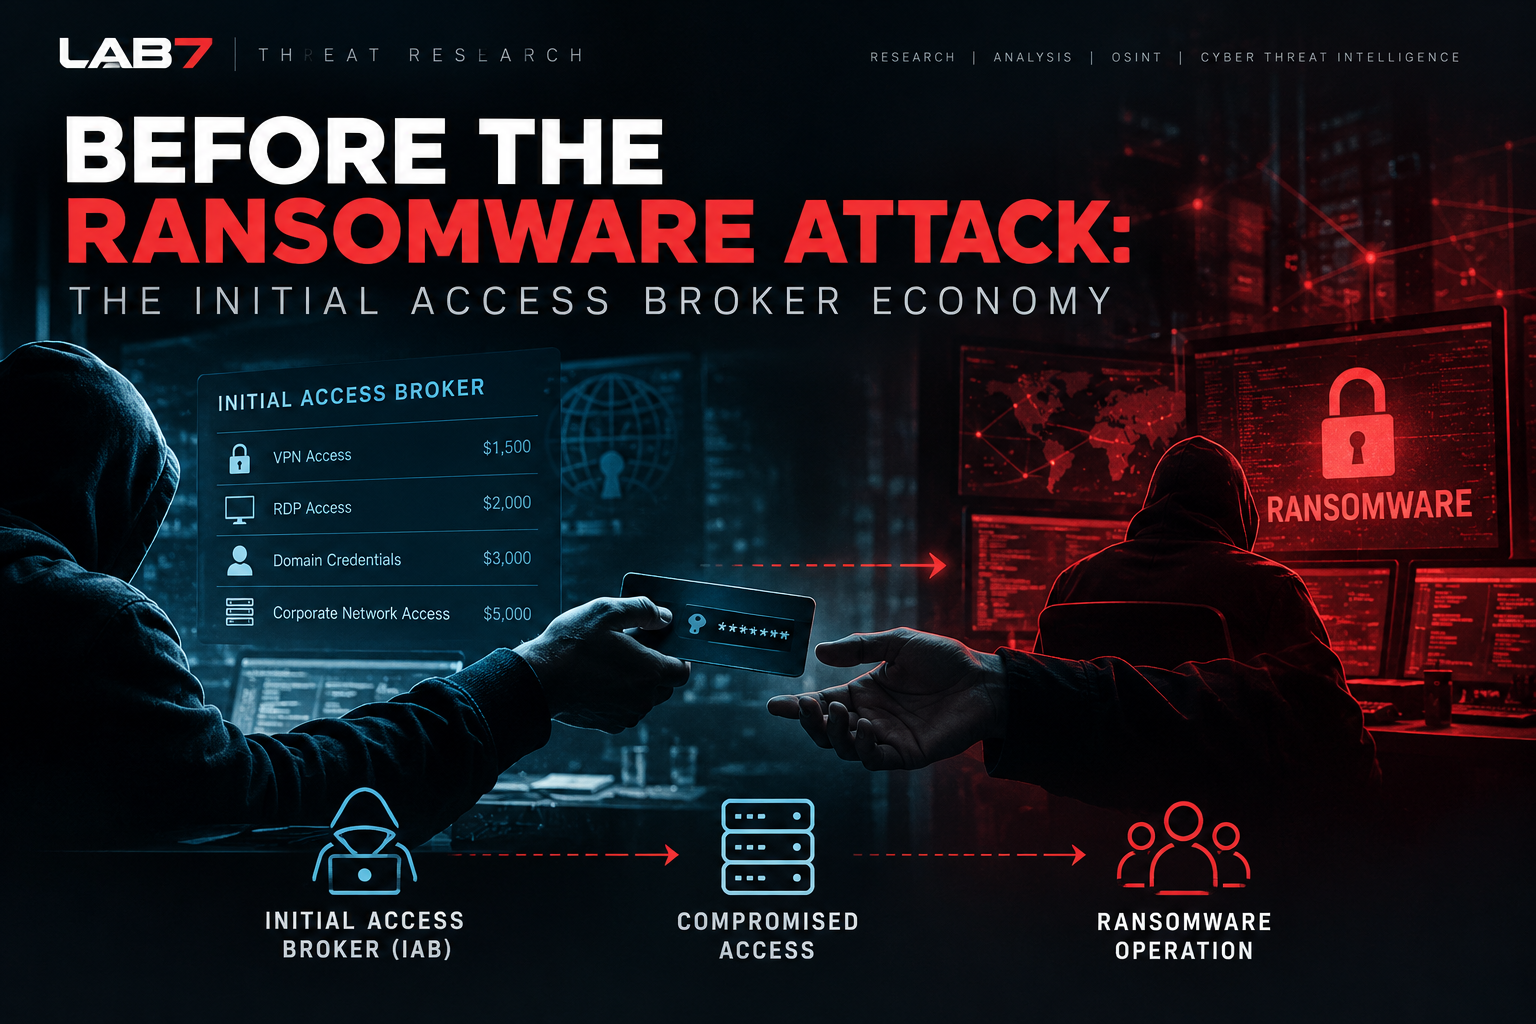
Before the Ransomware Attack: The Initial Access Broker Economy Not every ransomware operation begins with…
usama R. — Cybersecurity | Web Application Penetration Tester | Vulnerability Assessment | OWASP Top 10 | Burp Suite Professional
Reshared from a post by Mario M.
Before the Ransomware Attack: The Initial Access Broker Economy
Not every ransomware operation begins with the ransomware group gaining initial access.
In some cases, that access may already be available through an Initial Access Broker (IAB).
Compromised VPN credentials, exposed remote access services, and access to corporate environments can become commodities in underground markets.
For threat researchers, the important question isn't simply who deployed the ransomware.
It's also:
- Who may have obtained the initial access?
- Was that access advertised or transferred before the attack?
- Are there credible links between the access broker and the ransomware operation?
- What evidence supports those connections?
At LAB7 Threat Research, we're exploring these questions through passive OSINT monitoring and analysis of publicly available intelligence.
An advertised access listing is not proof of compromise, and a claimed connection is not confirmed attribution.
Understanding the access economy may help explain what happens before ransomware deployment.
#ThreatIntelligence #InitialAccessBroker #Ransomware #ThreatResearch #OSINT
0 reactions · 0 comments