Just released an open-source bash checker for CIFSwitch (CVE-2026-46243) — the 19-year-old Linux kernel LPE…
Liam R. — Freelance Penetration Tester
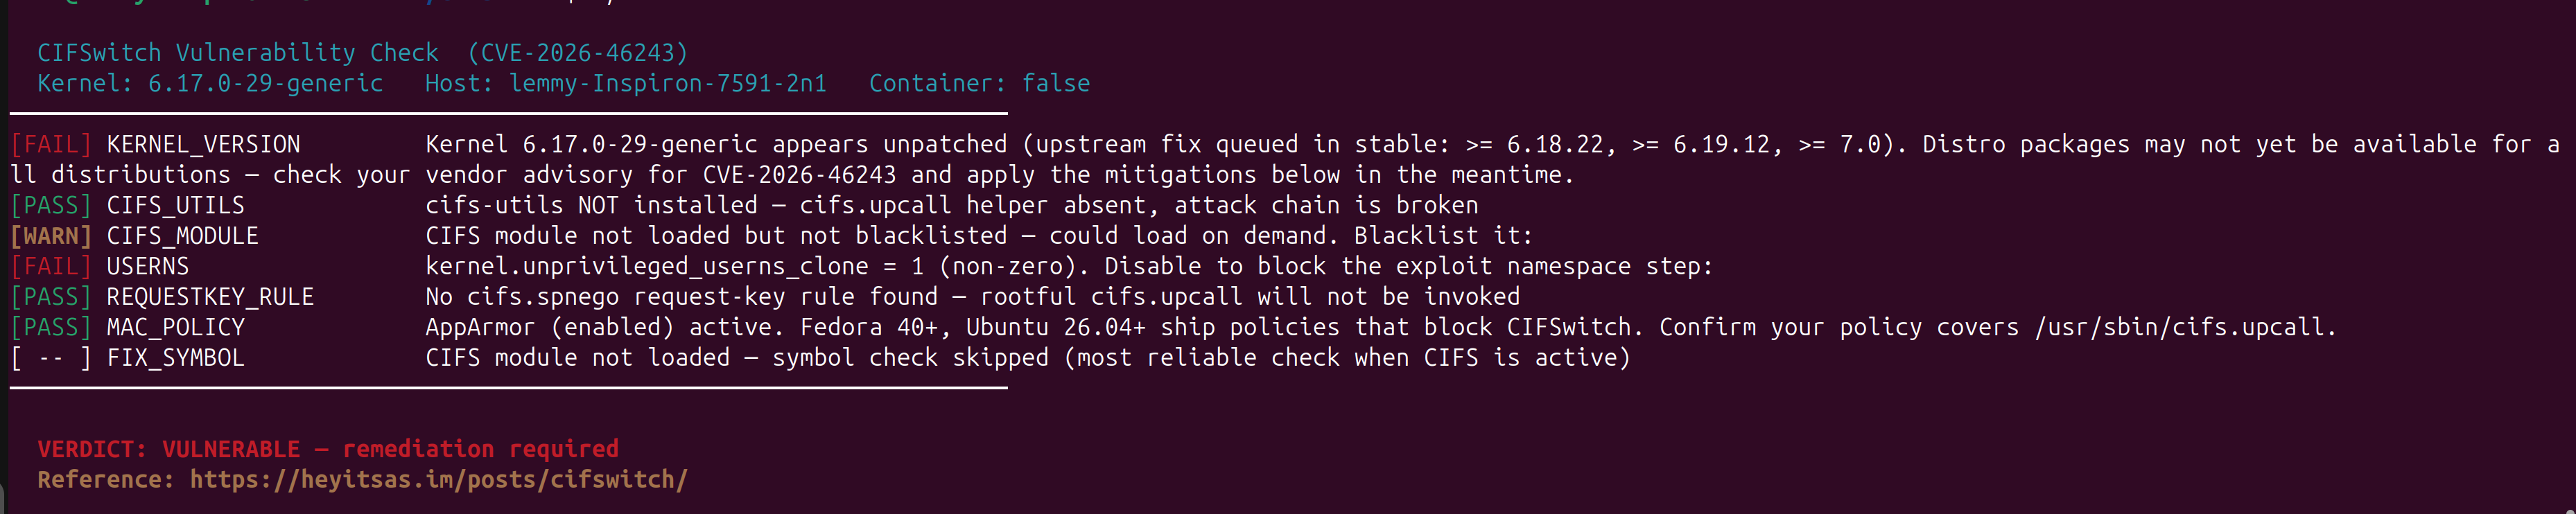
Just released an open-source bash checker for CIFSwitch (CVE-2026-46243) — the 19-year-old Linux kernel LPE disclosed last week that lets any unprivileged local user get root by abusing the CIFS/SPNEGO upcall path.
The script runs on bare-metal, VMs, and inside containers, and is CI/CD-friendly with JSON output and clean exit codes.
It checks:
✅ Kernel version against patched thresholds (6.18.22 / 6.19.12 / 7.0+)
✅ cifs-utils presence and exploitable version
✅ CIFS kernel module load state and blacklist status
✅ Unprivileged user namespace sysctl (the pivot point for the exploit)
✅ Active request-key cifs.spnego rules
✅ SELinux / AppArmor enforcement
✅ Container capabilities (CAP_SYS_ADMIN)
✅ Kernel symbol verification for the fix commit
Outputs human-readable or JSON for SIEM ingestion. Exit 0 = safe, exit 1 = action needed — drop it straight into a pipeline.
CIFSwitch is the fourth Linux LPE in under six weeks (after Copy Fail, Dirty Frag, and Fragnesia). If you're running multi-tenant Linux, CI runners, or container build farms, now is a good time to audit.
It is available here:
https://github.com/liamromanis101/cifswitch-check
I have also updated my container escape audit tool accordingly with checks for this issue:
https://github.com/liamromanis101/K8s-container_escape_audit
2 reactions · 0 comments