Posted in GRC
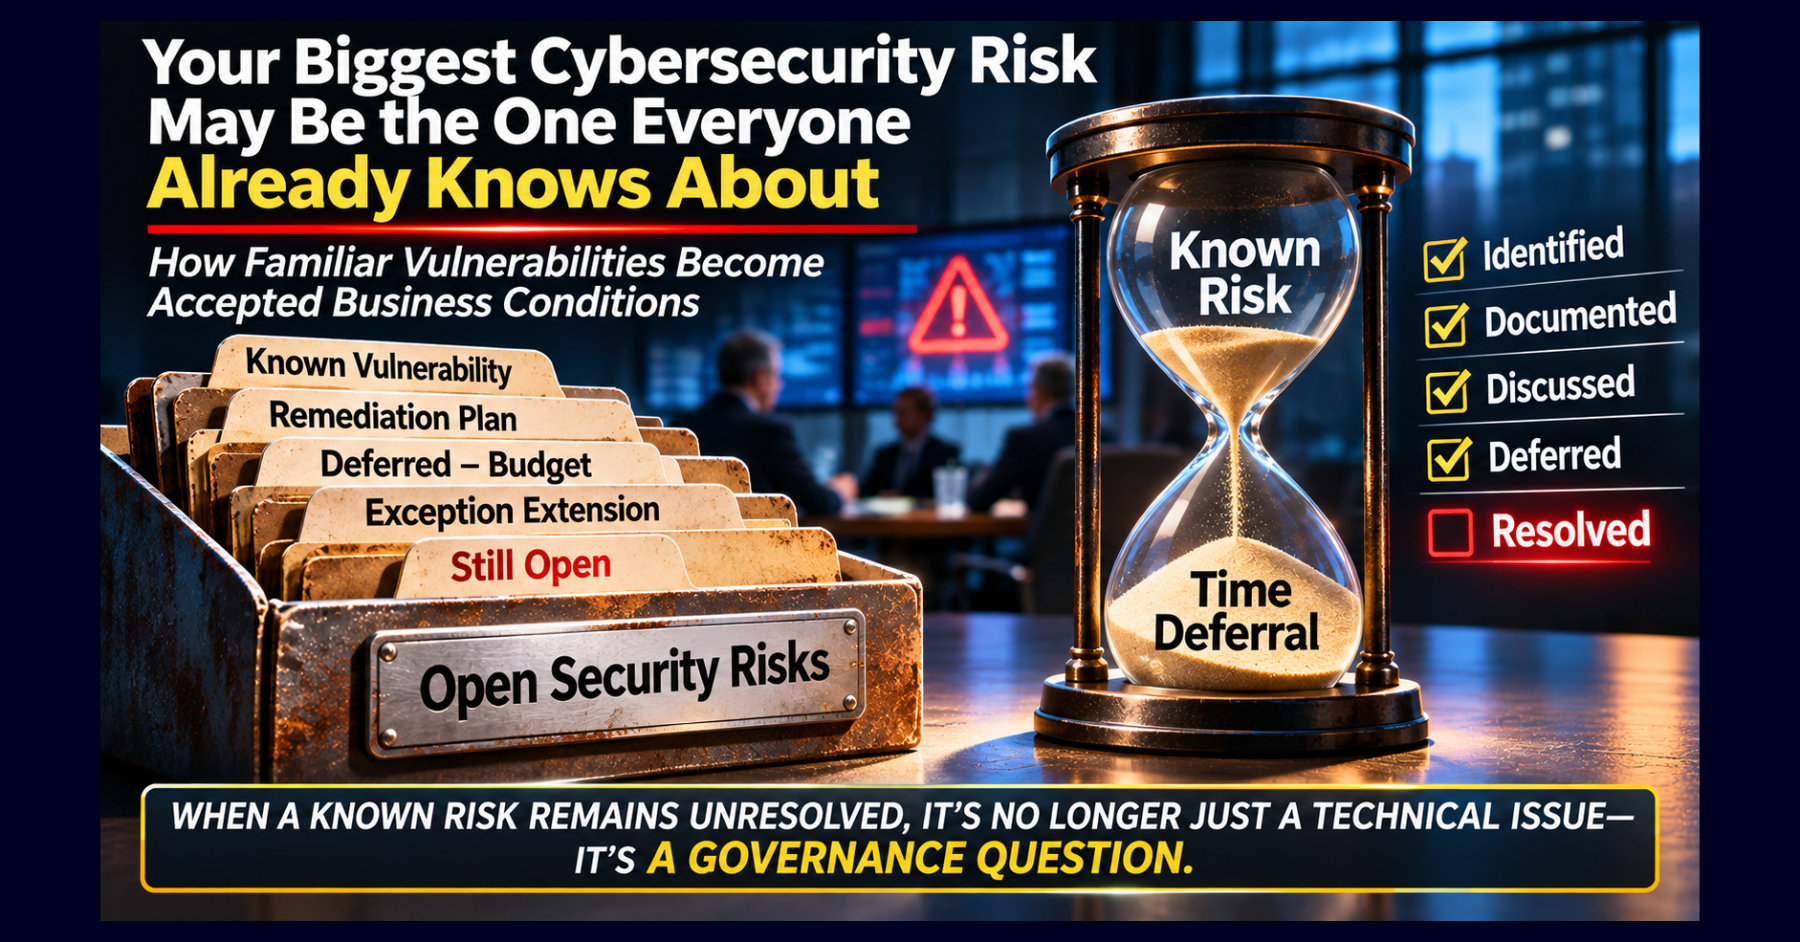
Your Biggest Cybersecurity Risk May Be the One Everyone Already Knows About
Victor Font — Keynote Speaker | Strategic Technology Leader | Fractional CIO | IT & Cyber Governance Expert | Published Author | FedRAMP Readiness | Board-Level Advisor | Digital Transformation | Enterprise WordPress/Formidable Forms
How Familiar Vulnerabilities Become Accepted Business Conditions
Somewhere in your organization, there is probably a cybersecurity risk that everyone knows about.
The security team has documented it.
IT has evaluated it.
The business owner understands it.
Management has discussed it.
It appears in a vulnerability report, risk register, audit finding, or remediation backlog.
There is a plan to address it.
There has been a plan for months.
Perhaps years.
Yet the risk remains.
Not because nobody noticed it.
Not because the organization lacks cybersecurity expertise.
Not even because the technology required to address it is unavailable.
The risk persists because other priorities repeatedly take precedence.
The organization has not failed to identify the problem. It has learned to live with it.
And that may be one of the most dangerous conditions in enterprise cybersecurity governance.
The Risk That Became Normal
Consider a business-critical application running on an aging technology platform.
The application supports essential operations.
Replacing it would require significant investment, operational disruption, and coordination across multiple departments.
Security has identified serious vulnerabilities.
IT has proposed modernization.
The business unit acknowledges the exposure.
But the replacement project keeps getting postponed.
This year, the organization has other capital priorities.
Next year, a major transformation initiative consumes the available resources.
The following year, leadership changes.
The project returns to the planning backlog.
Meanwhile, the vulnerable system continues operating.
Every quarterly risk review acknowledges the problem.
Every management presentation describes the planned remediation.
Every year, the organization becomes more accustomed to the exposure.
Eventually, something subtle happens.
The risk stops feeling exceptional.
It becomes part of the operating environment.
A vulnerability that remains unresolved long enough can begin to look like an accepted business condition—even when nobody has made a defensible decision to accept it.
That is where familiarity becomes dangerous.
Known Does Not Mean Governed
Cybersecurity programs are generally effective at creating visibility into identified risks.
Vulnerability scanners discover technical weaknesses.
Audits identify control deficiencies.
Penetration tests expose exploitable conditions.
Risk assessments evaluate potential consequences.
Governance platforms consolidate findings into registers and dashboards.
These capabilities are important.
But visibility does not establish accountability.
A known risk is not necessarily a governed risk.
The distinction depends on what happens after identification.
Who has authority over the decision?
What treatment options were considered?
Why was remediation postponed?
What compensating controls were established?
What conditions would require reconsideration?
Who is accountable for monitoring the exposure?
And how does the organization determine whether the original decision remains reasonable?
If those questions cannot be answered, the risk may be documented without being meaningfully governed.
A risk register can tell leadership what the organization knows. It cannot, by itself, demonstrate what leadership has responsibly decided.
The Normalization of Cybersecurity Deviance
There is a concept in organizational safety known as the normalization of deviance .
It describes how departures from expected standards can gradually become accepted when they do not immediately produce visible harm.
A shortcut is taken.
Nothing bad happens.
The shortcut is repeated.
Still nothing happens.
Over time, the deviation becomes routine.
The absence of an immediate adverse consequence is mistaken for evidence that the practice is safe.
Cybersecurity organizations are vulnerable to the same pattern.
A critical vulnerability remains unresolved for thirty days.
No incident occurs.
The exception is extended.
Another thirty days pass.
Still no incident.
The organization becomes increasingly comfortable with the exposure.
Eventually, the original urgency disappears.
The vulnerability has not necessarily become less dangerous.
The organization has simply become more familiar with it.
The absence of exploitation is not evidence that the exposure is acceptable.
That distinction matters because attackers do not operate according to the organization's remediation calendar.
When Exceptions Become Permanent
Security exceptions are sometimes necessary.
Organizations cannot remediate every vulnerability immediately.
Some changes require maintenance windows.
Some systems have operational dependencies.
Some risks cannot be eliminated without disproportionate business consequences.
A mature governance program must accommodate these realities.
But an exception should represent a deliberate, bounded decision—not an indefinite suspension of accountability.
Consider a critical vulnerability granted a ninety-day remediation exception.
The business owner approves the delay.
Compensating controls are documented.
A review date is established.
Ninety days later, remediation remains incomplete.
The exception is renewed.
Then renewed again.
After several extensions, the original decision may no longer reflect the current threat environment, business dependencies, or available treatment options.
Yet the administrative record remains intact.
The organization can demonstrate that the exception was approved.
What it may struggle to demonstrate is whether continued acceptance remains justified.
An exception that is repeatedly renewed without meaningful reassessment can become a mechanism for preserving risk rather than managing it.
The paperwork remains current.
The underlying decision becomes stale.
The Risk of Institutional Memory
Long-standing cybersecurity weaknesses often survive organizational transitions.
A CISO inherits a vulnerability from a predecessor.
A new CIO discovers that modernization has been postponed for years.
A business executive assumes the existing risk acceptance was thoroughly evaluated.
An audit committee receives the same unresolved finding across multiple reporting periods.
Everyone assumes someone previously made the necessary decision.
But institutional memory is not a substitute for governance evidence.
Why was the risk originally accepted?
What alternatives were evaluated?
What assumptions supported the decision?
Were those assumptions ever tested?
Have the business consequences changed?
Does the current accountable executive understand the exposure?
Without a traceable decision history, the organization may be perpetuating a risk that nobody currently understands well enough to defend.
This is particularly concerning when an exception outlives the executives who originally approved it.
Risk acceptance should not become an inherited obligation whose rationale has been lost.
The Budget Is Also a Governance Decision
One of the most uncomfortable aspects of persistent cybersecurity risk is the relationship between remediation and resource allocation.
Security teams may repeatedly recommend corrective action.
IT may develop technically sound remediation plans.
Business leaders may acknowledge the exposure.
But funding never materializes.
The risk remains unresolved because the organization has prioritized other investments.
That is a business decision.
And business decisions have consequences.
An executive who declines funding for a material security improvement may be exercising legitimate financial judgment.
Organizations have finite resources.
Not every cybersecurity investment can be approved.
But the decision should be informed by the potential consequences of leaving the exposure unresolved.
It should also be traceable.
When leadership repeatedly defers cybersecurity remediation through budget decisions, the resulting exposure is not merely a technical backlog item. It is a consequence of enterprise resource allocation.
That does not mean every deferred security project represents negligence.
It means the organization should be able to demonstrate that the decision was made by an appropriate authority, with a reasonable understanding of the alternatives and consequences.
What Changes When the Threat Changes?
A risk acceptance decision is made at a particular moment using the information available at that time.
But cybersecurity conditions are dynamic.
A vulnerability that initially required specialized access may later become remotely exploitable.
Proof-of-concept exploit code may become publicly available.
Threat actors may begin actively targeting affected systems.
A previously isolated application may become connected to additional enterprise services.
The business may expand its reliance on the vulnerable platform.
Regulatory obligations may change.
Each development can alter the original risk assessment.
Yet organizations sometimes treat accepted risks as administratively closed until their next scheduled review.
That creates a dangerous disconnect.
The decision remains unchanged while the conditions supporting it evolve.
A mature governance process should identify events that trigger reconsideration.
Those triggers might include new exploitation intelligence, increased business criticality, failed compensating controls, changes in exposure, or significant shifts in potential impact.
Risk acceptance must remain conditional on the circumstances that made the decision reasonable.
Otherwise, yesterday's judgment becomes tomorrow's unexamined vulnerability.
Evidentiary Architecture™ and the History of a Risk
This is one of the problems Evidentiary Architecture™ is intended to address.
Traditional risk registers typically provide a current view of identified exposure.
They may show severity, ownership, treatment status, and review dates.
But a defensible governance record should preserve the evolution of the decisions surrounding that exposure.
For a long-standing material risk, the organization should be able to reconstruct:
Risk identified → Business impact assessed → Treatment options evaluated → Decision authorized → Conditions established → Exposure monitored → Changes reassessed → Decision renewed, revised, or closed.
The important element is continuity.
Every extension should be connected to the evidence supporting it.
Every material change should trigger appropriate review.
Every accountable executive should understand the obligations inherited from prior decisions.
And every closure should be supported by evidence that the intended outcome was achieved.
The objective is not to produce more paperwork.
It is to prevent material risks from becoming permanent features of the organization simply because their histories have become difficult to reconstruct.
The Boardroom Blind Spot
Boards often receive reports identifying the organization's most significant cybersecurity risks.
Those reports may include severity ratings, remediation status, mitigation plans, and projected completion dates.
But consider a different set of questions.
Which material risks have remained unresolved the longest?
How many times have their remediation deadlines been extended?
What changed between the original acceptance decision and the latest renewal?
Which risks remain unresolved primarily because of funding or business-priority decisions?
How does management verify that compensating controls remain effective?
And which accepted risks would no longer be approved if they were presented as new decisions today?
That last question is particularly revealing.
Would leadership knowingly accept the same exposure today, under current conditions, if the organization were encountering it for the first time?
If the answer is no, the organization may be relying on familiarity rather than sound governance judgment.
Boards do not need to approve every remediation decision.
But they should seek assurance that material unresolved risks remain subject to meaningful oversight rather than becoming permanent entries in management reports.
The Most Dangerous Words in Cybersecurity
"We've known about that for years."
Those words can mean two very different things.
They may indicate that the organization has carefully evaluated a persistent risk, established appropriate safeguards, and maintained accountable oversight.
Or they may reveal that the organization has gradually normalized a weakness nobody has been willing or able to resolve.
The difference is not how long the risk has existed.
It is whether the organization can demonstrate that continued exposure remains an informed, authorized, and actively governed decision.
Familiarity is not mitigation.
Documentation is not remediation.
And repeated acknowledgment is not accountability.
A risk does not become acceptable simply because the organization has survived its presence.
The Question I Would Ask Every CISO
Find the oldest unresolved material cybersecurity risk in your organization.
Not the newest critical vulnerability.
Not the highest-profile threat.
The oldest significant exposure that everyone has learned to live with.
Then ask:
Who originally accepted it?
How many times has remediation been postponed?
What assumptions justified those decisions?
Are those assumptions still valid?
What would cause leadership to stop accepting the exposure?
And if an incident occurred tomorrow, could the organization demonstrate why the risk remained unresolved?
The answers may reveal more about the effectiveness of cybersecurity governance than another quarterly compliance dashboard.
Because some of the most consequential cybersecurity failures do not begin with an unknown vulnerability.
They begin with a known weakness that gradually becomes ordinary.
The greatest danger may not be the risk your organization failed to discover. It may be the one everyone discovered, everyone discussed, and everyone eventually stopped questioning.
Discussion
Think about the oldest significant cybersecurity risk your organization continues to carry.
Is it still unresolved because management has made a deliberate, informed decision to accept the exposure?
Or has it simply survived enough budget cycles, leadership changes, and remediation extensions that nobody questions it anymore?
At what point does a repeatedly postponed cybersecurity risk stop being a technical problem and become an executive accountability failure?
#CybersecurityGovernance #CyberRisk #RiskAcceptance #ExecutiveAccountability #VulnerabilityManagement #SecurityLeadership #GRC #EvidentiaryArchitecture
3 reactions · 5 comments
Topics: #cyberrisk, #vulnerabilitymanagement, #securityleadership, #cybersecuritygovernance, #executiveaccountability, #evidentiaryarchitecture, #riskacceptance, #grc
Comments
Schomer: This lands exactly right. The danger isn't that the risk is hidden, it's that it stops being treated as a decision at all. Once the exception is renewed enough times, nobody is really accepting it anymore, they're just inheriting it. I see the same pattern at the protocol level in my own work. I build a Modbus guard that checks every write against its invariants before forwarding it, and logs the
Victor Font: Schomer Schomer, you've identified the critical distinction: a risk acceptance should remain a decision, not become an inherited assumption. Your Modbus example illustrates what governance should look like in practice—evaluate the current conditions, enforce the established boundaries, and preserve the rationale. At the enterprise level, we should be applying that same discipline to material risk
Schomer: Victor, thank you — that framing helps a lot. "A decision, not an inherited assumption" is the cleanest way I've heard it put, and the renewal point is the one I'll carry forward: every extension should have to show the original assumptions still hold, not just get another signature. Appreciate you taking the Modbus example seriously and connecting it to the enterprise side.
Victor Font: Schomer Schomer, I appreciate the exchange as well. Your Modbus examples bring something valuable to these discussions: a concrete demonstration of how principles we discuss in the boardroom translate into technical enforcement. Too often, governance and engineering are treated as separate disciplines when they should reinforce each other. Your work illustrates that connection particularly well. I
Schomer: Victor, appreciate you saying that — and the exchange. That's exactly what I'm trying to do with the Modbus work: take a governance principle and make it something you can actually enforce and show the decision for, not just write down. Glad it's landing that way here, and I look forward to more of these too.