Offensive Security needs business KPIs not just technical findings. A VAPT or Red Team program should answer…
Chukwunonso A. — Offensive Cyber Security Consultant for High-Value & Regulated Environments (FinTech, Banking, Healthcare, Cloud) | I simulate real-world attacks to uncover critical attack paths before they become incidents.
Offensive Security needs business KPIs not just technical findings.
A VAPT or Red Team program should answer one question:
“Is the business becoming harder to compromise?”
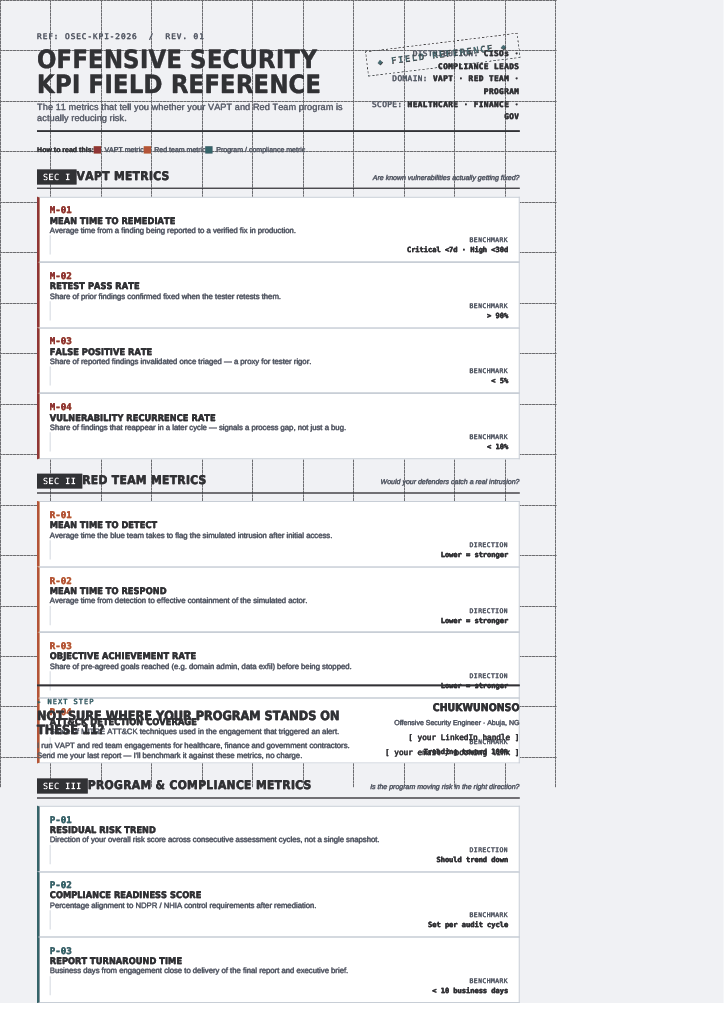
That means measuring:
• Mean Time to Remediate
• Retest Pass Rate
• Vulnerability Recurrence
• Mean Time to Detect & Respond
• Objective Achievement
• Residual Risk Trend
• Compliance Readiness
• Reporting Turnaround
The shift is simple: stop measuring how busy security is. Start measuring how much risk the business has removed.
That’s how Offensive Security earns executive attention and budget.
#CyberSecurity #OffensiveSecurity #VAPT #RedTeam #CyberRisk #CISO #SecurityMetrics
0 reactions · 0 comments
Topics: #offensivesecurity, #vapt, #cyberrisk, #ciso, #securitymetrics, #redteam, #cybersecurity