Case Study: Engineering a Hardened Cloud Perimeter in AWS During my cloud security research, I focused on…
Haydn K. — Lead Community Operator
Case Study: Engineering a Hardened Cloud Perimeter in AWS
During my cloud security research, I focused on the essential defense-in-depth hygiene required when initializing a greenfield AWS organization. The first hours of a cloud environment's lifecycle are the most vulnerable, and this project establishes a hardened, production-grade foundation for future infrastructure labs.
The implementation focuses on eliminating root exposure, implementing scalable access controls, and ensuring continuous visibility. Here are the core phases of the deployment:
Root Hardening & IAM Identity Center: I activated a centralized identity provider instance to manage cross-account access from a single control plane. The unrestricted root identity was reinforced with physical multi-factor authentication and securely locked away, moving all daily operations to a secure workforce directory.
Role-Based Access Control: To prevent privilege creep, I built out isolated operational groups for network engineering, systems administration, and security auditing. These groups were bound directly to AWS-managed predefined permission sets (such as NetworkAdministrator and SecurityAudit), ensuring human operators are strictly confined to their authorized lanes.
CloudWatch Telemetry Ingestion: I deployed global telemetry enablement rules to ingest CloudTrail management events directly into Amazon CloudWatch Logs across all regions. Choosing Managed Log Groups ensures built-in deletion protection and strict cryptographic source validation, keeping the audit trail safe from adversary tampering.
Fiscal Security Controls: I engineered a proactive billing guardrail using AWS Budgets. Setting a tight monthly cost budget acts as an operational canary in the coal mine, notifying security via automated alerts the moment a resource spike or credential compromise is forecasted to breach the threshold.
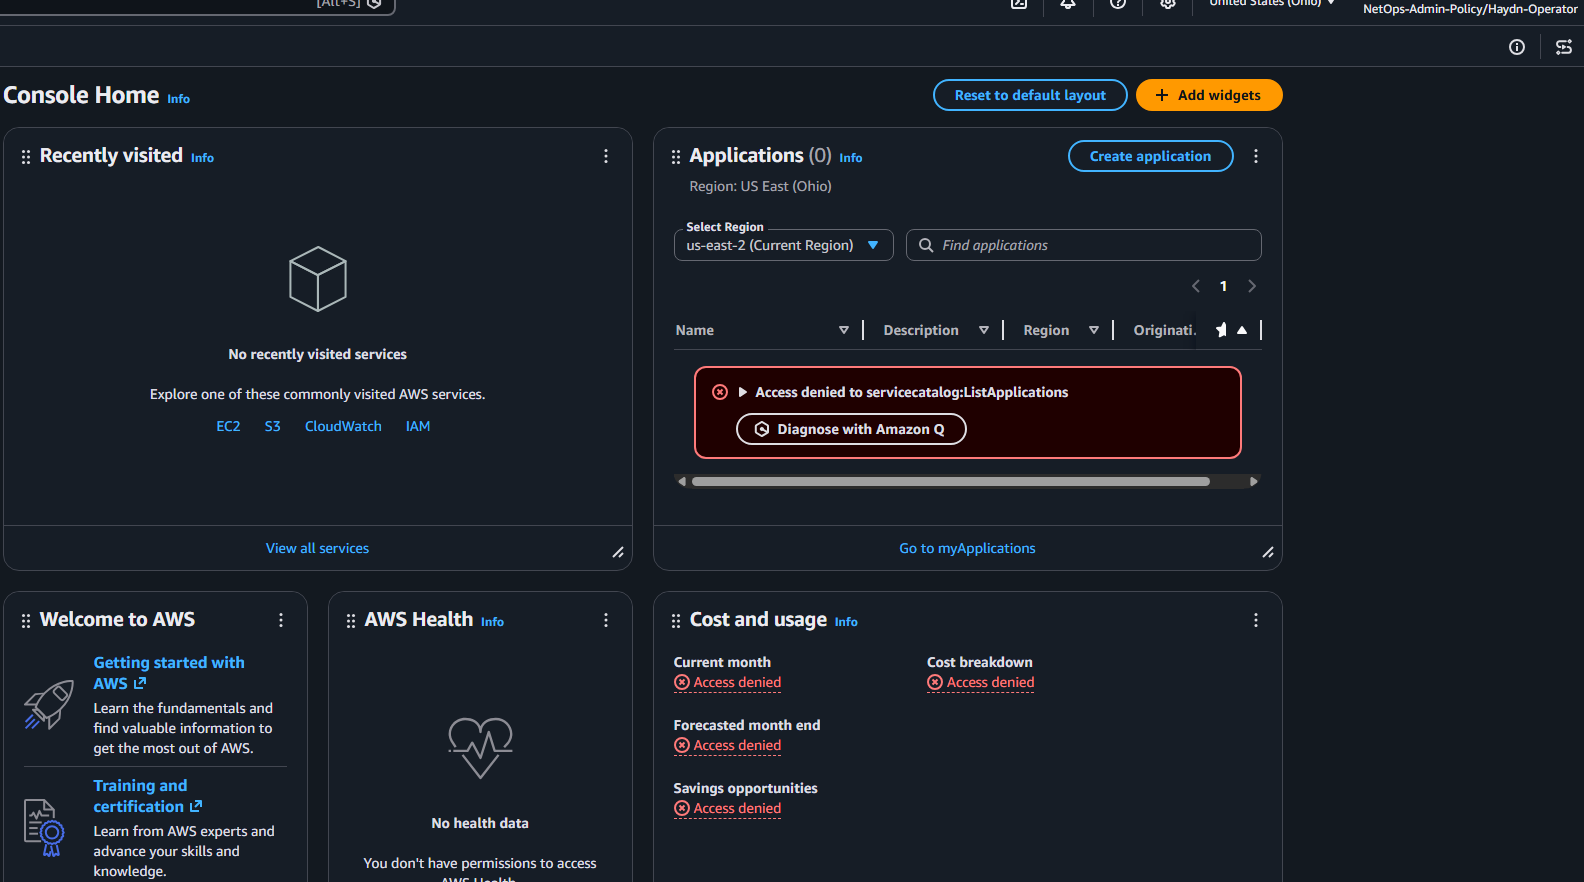
By validating the deployment through restricted placeholder accounts, the architecture successfully enforces access denied boundaries across unauthorized lanes, ensuring a true zero-trust baseline.
The full architectural write-up, including the step-by-step group mappings and logging configurations, is documented in my repository here: https://github.com/HaydnZK/AWS/tree/main/Step%20One%3A%20Securing%20the%20Cloud%20Perimeter
1 reactions · 0 comments