Pleased to share EZ Sentinel Workbench v6.0. EZ Sentinel Workbench is a Windows-based GUI designed to help…
KENNEDY A. — Cybersecurity Analyst
Pleased to share EZ Sentinel Workbench v6.0.
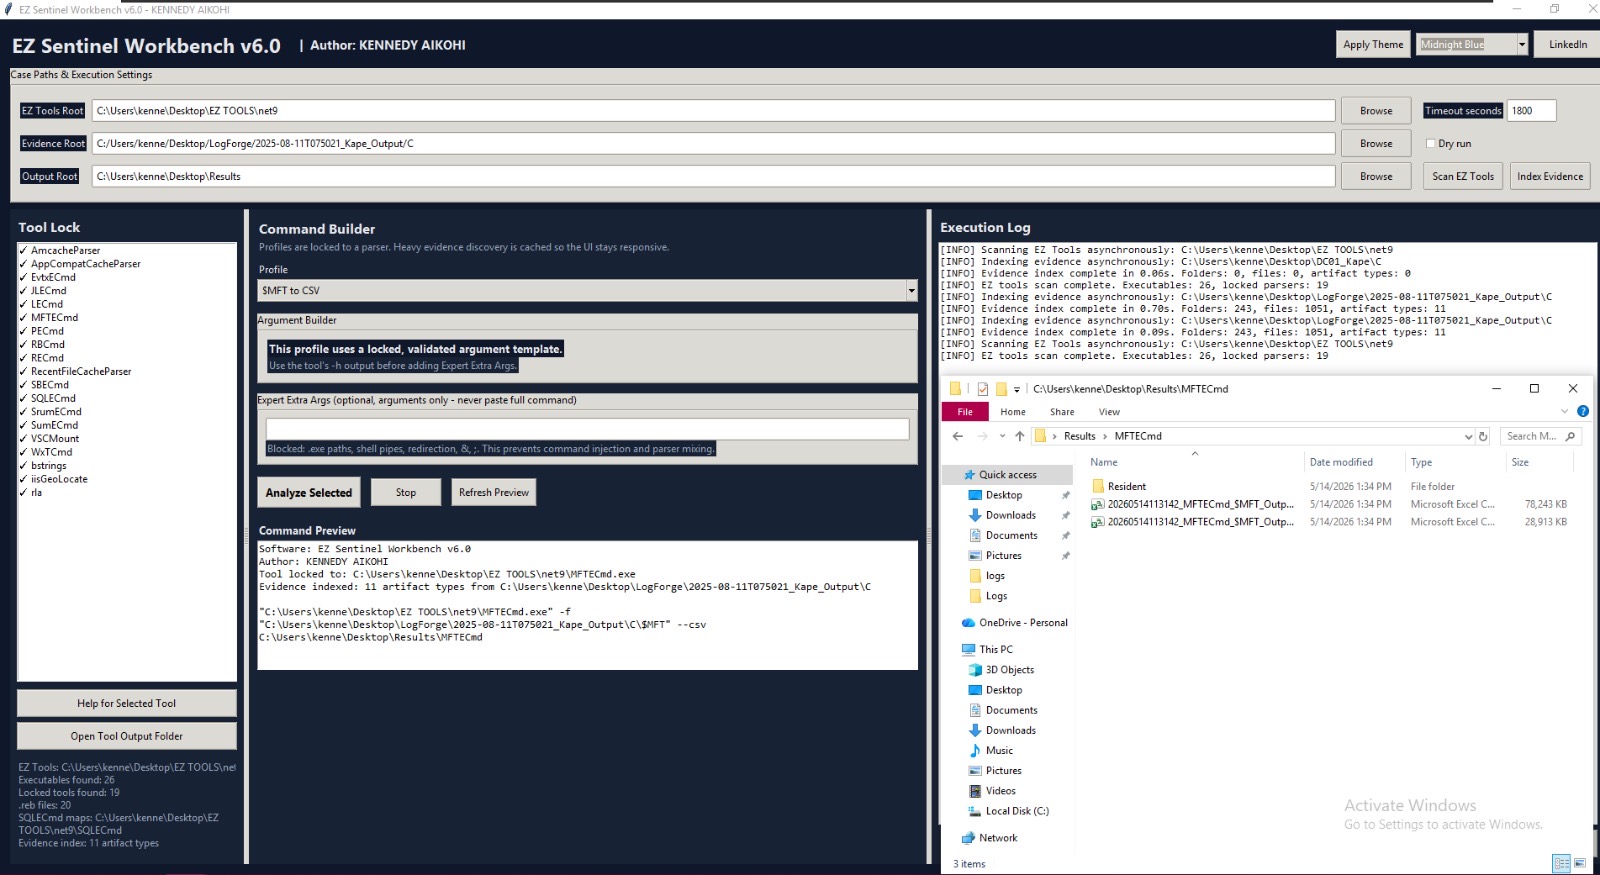
EZ Sentinel Workbench is a Windows-based GUI designed to help digital forensic analysts work faster with the Eric Zimmerman EZ Tools suite by reducing the need to constantly move between Command Prompt and PowerShell windows.
In many DFIR workflows, analysts must remember different parser syntax, validate command arguments, manage evidence paths, create output folders, and review results across multiple tools. Some EZ Tools commands and switches are also easy to miss, even for experienced analysts. For example, options such as parsing $MFT resident files with --dr, using RECmd search modes, or selecting the correct parser-specific arguments can be overlooked during time-sensitive investigations.
EZ Sentinel Workbench helps simplify that process by bringing multiple EZ parsers into one structured execution interface. It helps analysts discover and use the right commands for supported artifacts, including MFT, registry hives, event logs, LNK files, Jump Lists, ShellBags, SRUM, Amcache, Shimcache, Windows Timeline, SQLite artifacts, and more.
Key capabilities include:
Tool discovery
Parser locking
Evidence indexing
Guided command building
RECmd argument selection
Live execution logs
Timeout and stop controls
Direct access to parser output folders
Performance-focused background scanning
The goal is to reduce repetitive command-line work, expose useful parser options more clearly, and help analysts spend more time on investigation, evidence review, and decision-making.
GitHub: https://github.com/kennedy-KENNEDY A./EZ-Sentinel-Workbench
Compliance and clarification:
EZ Sentinel Workbench is an independent wrapper. It is not affiliated with, endorsed by, or officially connected to Eric Zimmerman.
The workbench does not redistribute EZ Tools binaries. Users must provide their own official locally installed copies of EZ Tools.
All underlying EZ Tools engines, names, and binaries remain the intellectual property of their original author, Eric Zimmerman.
#DFIR #DigitalForensics #IncidentResponse #CyberSecurity #WindowsForensics #ForensicTools #BlueTeam #ThreatHunting
1 reactions · 0 comments
Topics: #digitalforensics, #blueteam, #threathunting, #dfir, #incidentresponse, #windowsforensics, #cybersecurity, #forensictools