Testing The BCP And IR Deficit
Mark C. — Executive Technology & Cyber Leader | CIO | Cyber, Governance & Operational Resilience
When did you last test your BCP and Incident Response capability?
Not simply "review" it. Not just update a document, but actually test it to make sure it's fit for purpose?
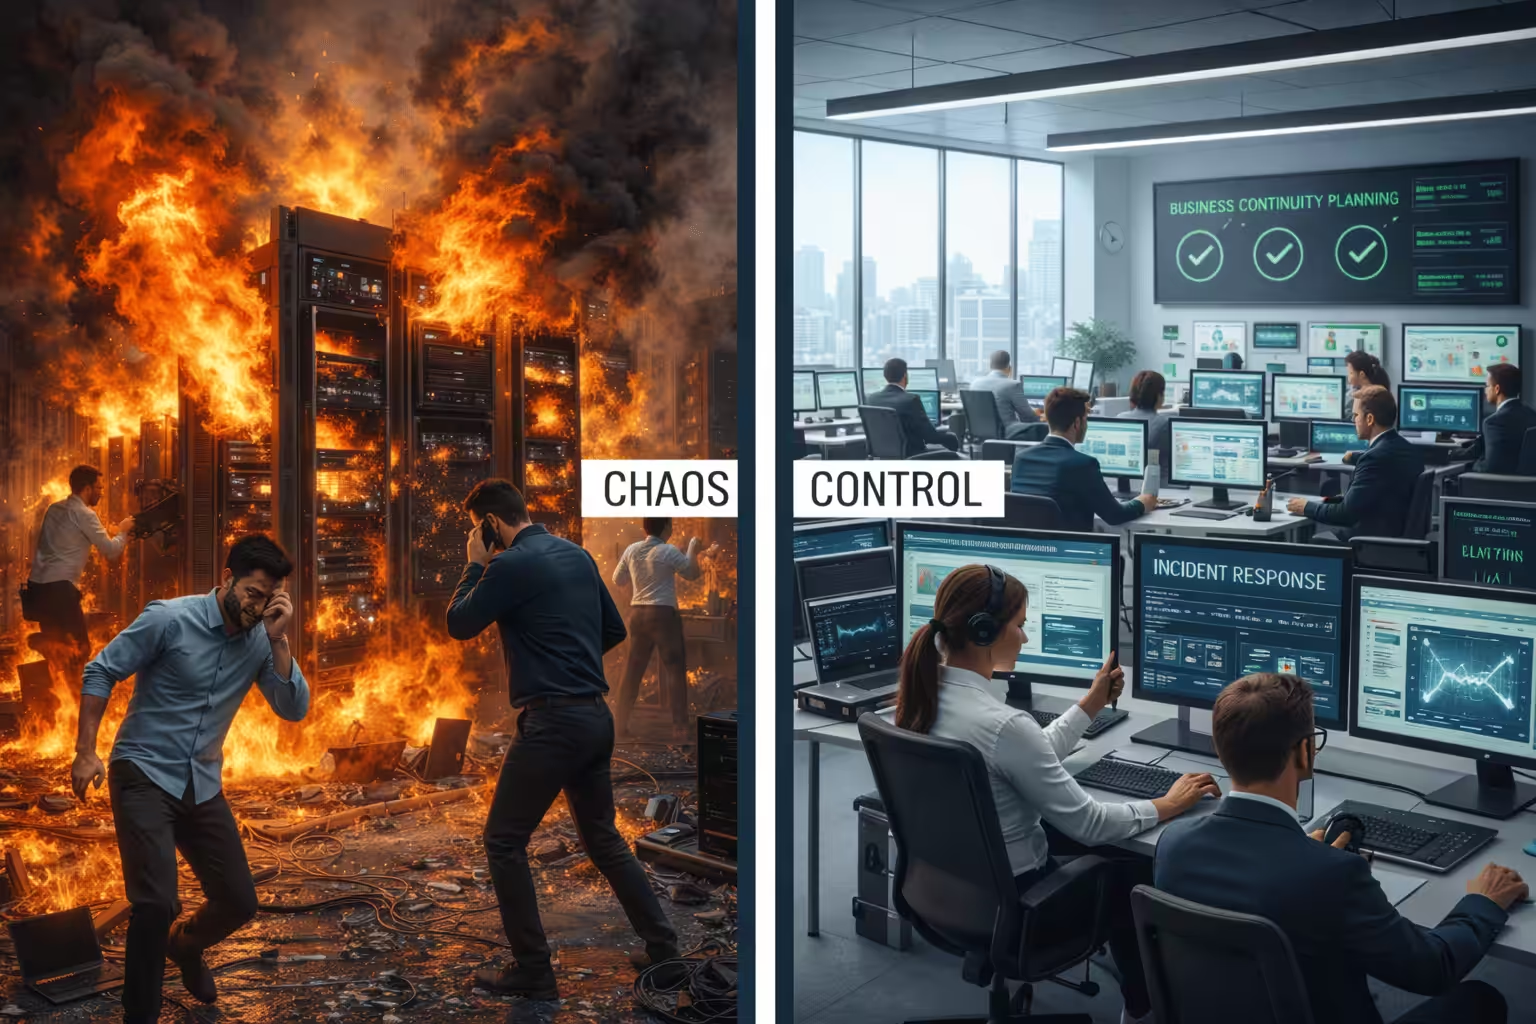
Most organisations don’t have any capability. They have a plan that hasn’t been proven when it needs to be relied upon, and that only becomes visible when something fails.
BCP and IR are not the same animal.
- BCP: can the business continue?
- IR: can you control the event?
If they’re not aligned, recovery falls like a house of cards. Untested plans suffer the same fate:
- Ownership is ambiguous
- Recovery times are assumed
- Backups don’t restore cleanly
- Communication breaks down
Consistent. Predictable. Avoidable.
Here's a simple board-level test:
If a material incident hits tomorrow:
- Who makes the decisions?
- How fast do you stabilise?
- What fails first?
If that isn’t clear, the plan isn’t even remotely ready. Testing isn’t compliance, but it is the only proof that holds under analysis.
Resilience isn’t declared. It’s demonstrated.
And if you can’t evidence that you’ve tested it recently and changed something as a result, you don’t have assurance.
You have nothing more than assumption - and frankly, a disaster waiting to happen.
https://phenomlab.com/theory/when-did-you-last-test-your-bcp-and-ir-plans/
1 reactions · 0 comments