Most people open a PCAP file and just scroll through packets. Today, I extracted actionable insight from…
OLUWATOYIN O. — Security Operations & Threat Analysis
Most people open a PCAP file and just scroll through packets.
Today, I extracted actionable insight from one.
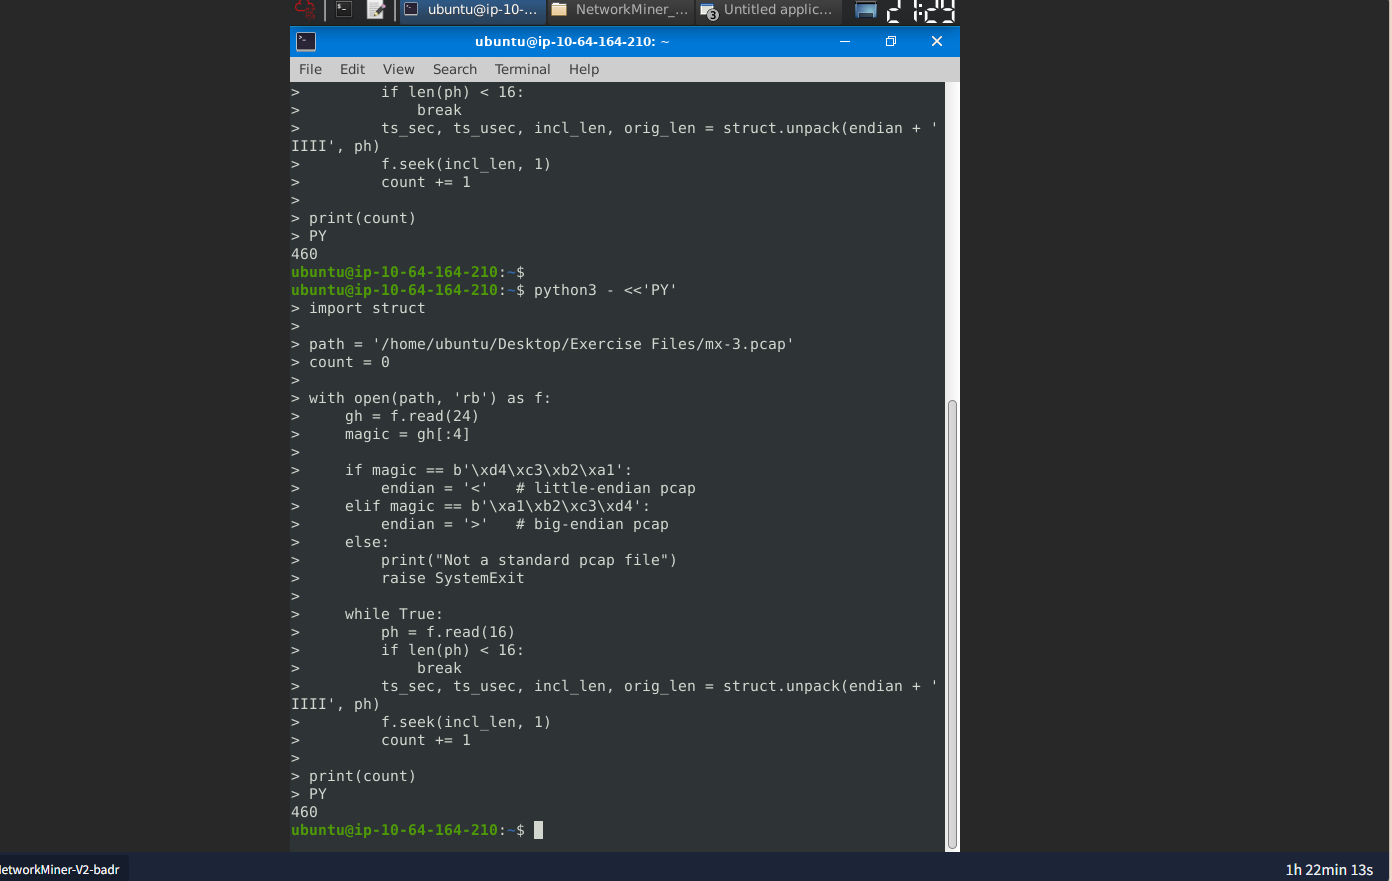
Using Python (no GUI tools), I analyzed raw packet data and:
✔ Parsed PCAP structure manually
✔ Automated packet counting logic
✔ Extracted 460 packets from network traffic
✔ Strengthened understanding of how data is structured at protocol level
This is the kind of hands-on work that builds real SOC capability — not just theory.
Because in real-world security operations, you don’t always rely on tools…
you understand what’s happening underneath them.
Currently building practical experience in:
🔹 Network Traffic Analysis (PCAP)
🔹 Threat Detection & Incident Response
🔹 Authentication & Protocol Analysis
🔹 Python for Security Automation
I’m actively seeking opportunities in a Security Operations environment where I can contribute and grow.
If you're hiring or working in cybersecurity, let’s connect.
#CyberSecurity
#SOCAnalyst
#NetworkAnalysis
#ThreatDetection
#BlueTeam
#InfoSec
#Python
5 reactions · 1 comments
Topics: #blueteam, #python, #infosec, #socanalyst, #networkanalysis, #cybersecurity, #threatdetection
Comments
Everett D.: Love seeing people still doing this! A fun analysis is run your code against a scapy script and see what diffs.