🧑💻Reason You Should Never Skip Reading JavaScript! Most automated tools missed this one. While manually…
John O. — Security Researcher | Penetration Tester | Reverse Engineer
🧑💻Reason You Should Never Skip Reading JavaScript!
Most automated tools missed this one.
While manually reviewing a target's JavaScript last week, I discovered an
🔥"Open Redirect vulnerability"
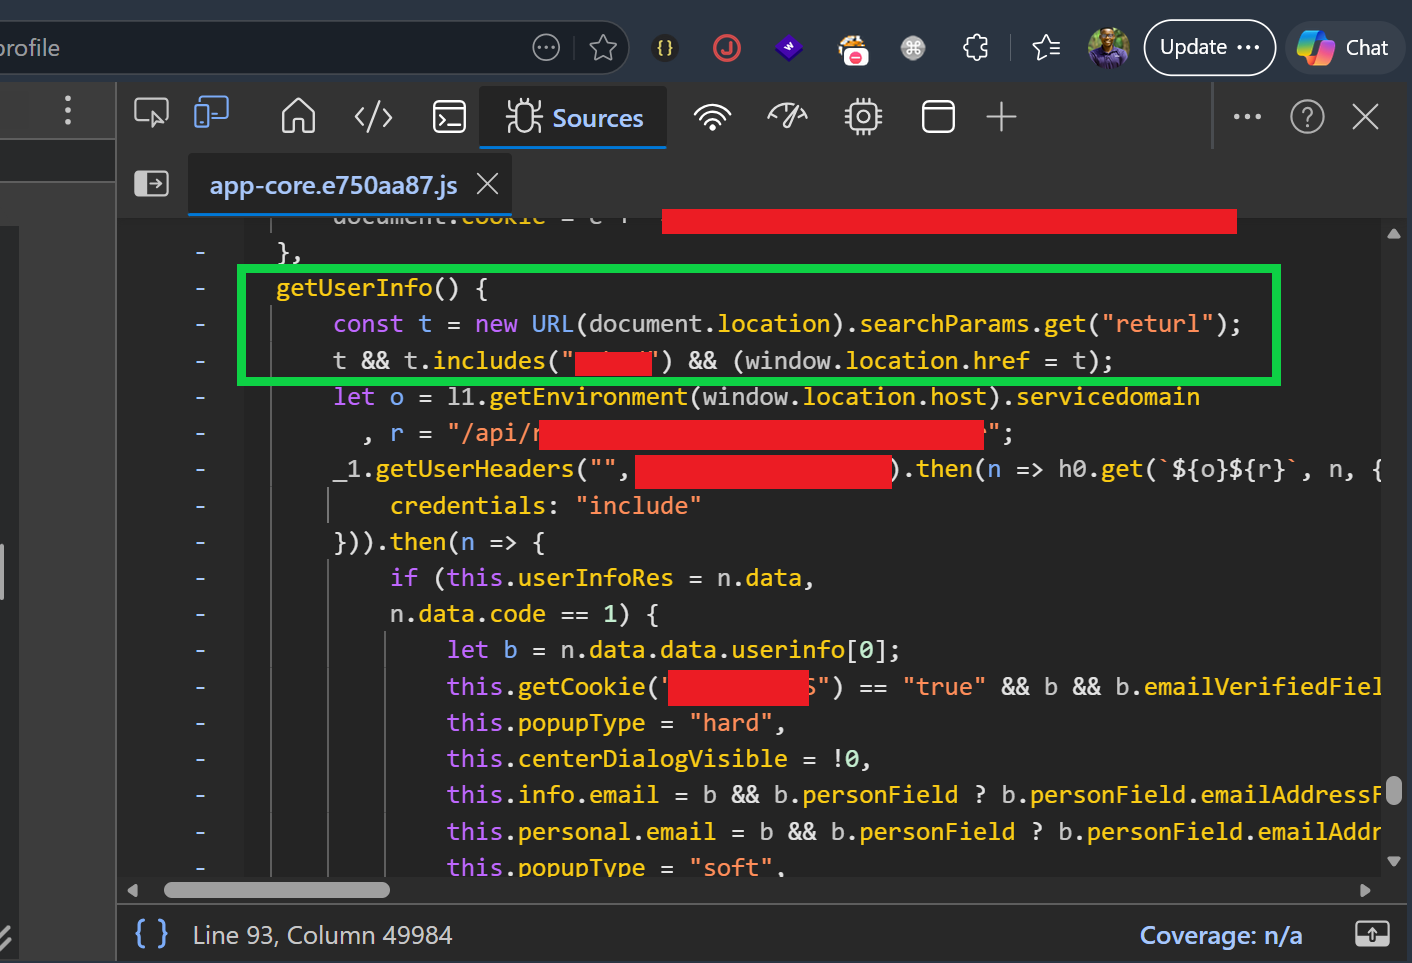
in the "returl" parameter used during authentication. This parameter was invisible, but when I looked at the JavaScript code, I found it.
A JavaScript function in the target trusted the user-controlled "returl" value and redirected users using "window.location.href", allowing redirection from a trusted domain to an attacker-controlled site. You can see this in the attached screenshot 👇
Before it performs the redirect, it checks if the name of the website is present in the URL e.g if the site is buyme.com, it checks for the word "buyme"
This could be leveraged by an attacker for phishing attacks by abusing user trust in the legitimate domain.
The parameter could be abused on both sign-in and profile endpoint by crafting the following URL (lets say the site is buyme.com):
✅https://[redacted].[redacted].com/signin?returl=https://buyme.evil.com
✅https://[redacted].[redacted].com/profile?returl=https://buyme.evil.com
This means, so long as this word "buyme" is present in the URL, it redirects to the attacker controlled website. This is a poor coding practice!
🙂Takeaway: Automated scanners are useful, but manually reading JavaScript can reveal vulnerabilities that tools overlook.
#BugBounty #AppSec #CyberSecurity #WebSecurity #JavaScript #OpenRedirect #SecurityResearch #OWASP #EthicalHacking #OffSec
1 reactions · 0 comments
Topics: #bugbounty, #javascript, #owasp, #websecurity, #ethicalhacking, #appsec, #securityresearch, #openredirect, #offsec, #cybersecurity