Spent the day breaking and rebuilding an organisational web policy in Cloudflare Zero Trust, and it reminded…
Biswadeb M. — Security Engineer & Independent Researcher
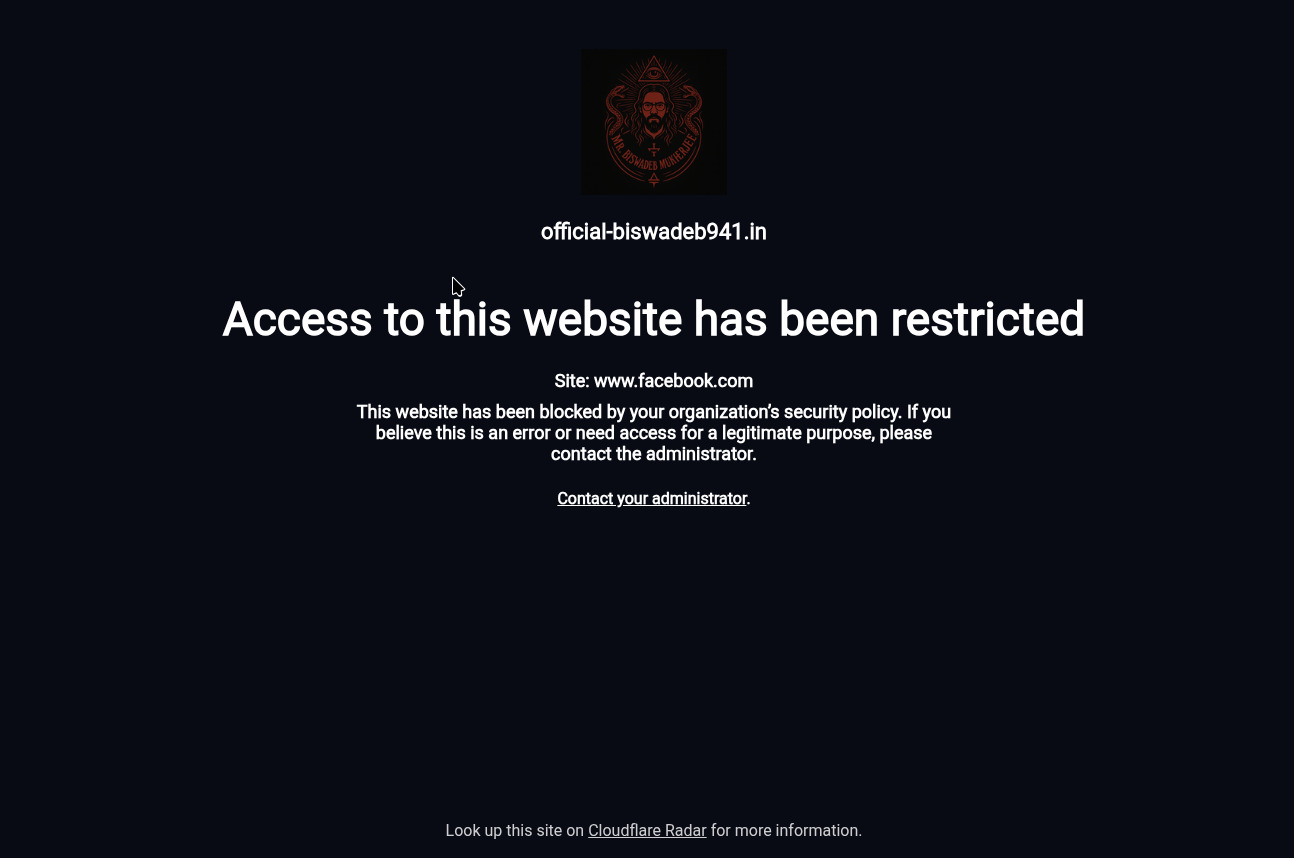
Spent the day breaking and rebuilding an organisational web policy in Cloudflare Zero Trust, and it reminded me of a mistake many organisations still make:
They mistake configured control for enforced control.
From a business perspective, a blocked category in DNS looks like a policy has been implemented.
From an attacker’s perspective, it’s just one layer in a chain.
The hard lesson is this: security controls should be designed around how users, apps, and browsers actually behave, not how we hope they behave.
That gap between policy on paper and policy under pressure is where many organisations lose visibility and control.
#CyberSecurity #ZeroTrust #SecurityLeadership #Cloudflare #SecurityResearch
2 reactions · 2 comments
Topics: #cloudflare, #securityleadership, #securityresearch, #zerotrust, #cybersecurity
Comments
Dave M.: There’s also the gap between a policy and a control that only implements partially and the organisation leadership thinking they have something covered - like blocking access to AI websites from corporate computers and thinking AI is “under control”
Biswadeb M.: DAVID MCKENZIE Exactly. A lot of organisations don’t have a control problem; they have a verification problem. The rulebook gets written, policies get signed off, and the existence of a control is mistaken for proof of enforcement. But if nobody is auditing, validating, or DDoS those rules against actual behaviour, the control can quietly decay while leadership still believes the risk is covered.