Most security platforms still operate like static scanners. RedNode is moving in a completely different…
Damian K. — Penetration Tester / Offensive Security Engineer
Most security platforms still operate like static scanners.
RedNode is moving in a completely different direction.
Over the last months the project evolved from:
tooling + dashboards + automation
into:
runtime offensive intelligence architecture.
Current focus is no longer:
“how many vulnerabilities were found?”
The focus became:
→ runtime truth
→ evidence lineage
→ topology cognition
→ attack-chain continuity
→ governance-aware execution
→ temporal offensive memory
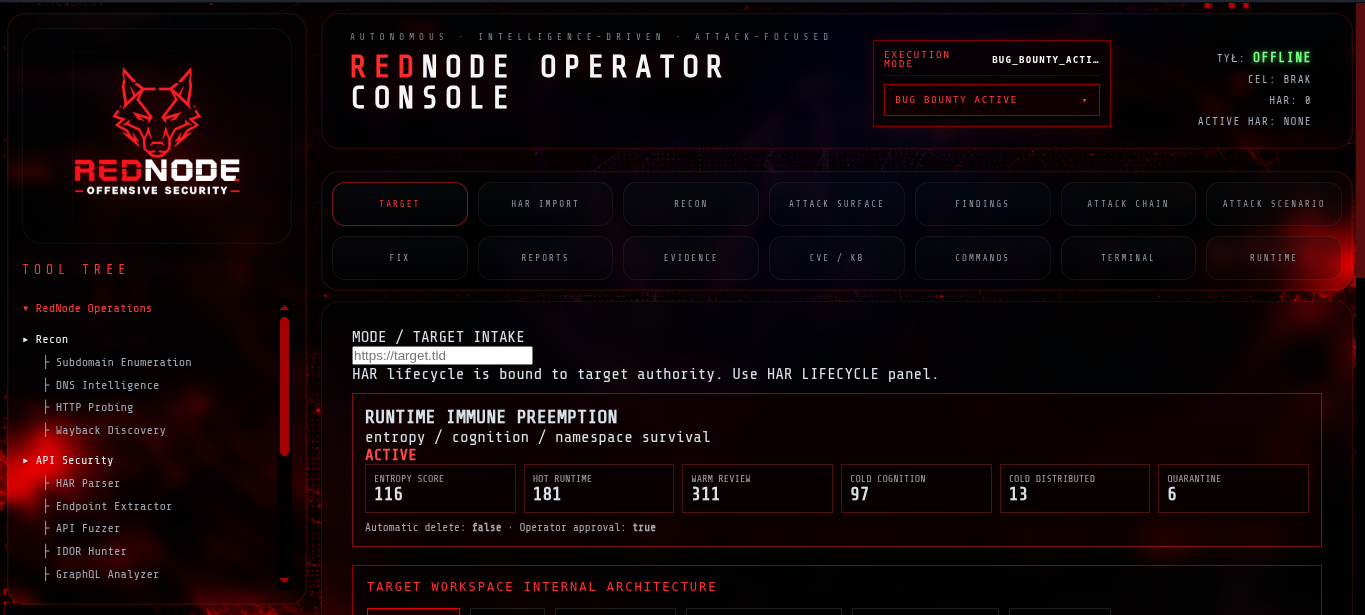
The Operator Console is slowly becoming a real offensive runtime workspace:
• HAR-driven runtime analysis
• attack-chain projection
• telemetry correlation
• governance modes
• runtime cognition
• evidence propagation
• execution lineage
• target-bound execution context
One of the biggest architectural changes:
AI is no longer the source of truth.
Runtime telemetry is.
That sounds subtle, but it changes everything.
Most “AI security” systems today:
→ summarize
→ classify
→ hallucinate confidence
RedNode is being built around:
REAL_TELEMETRY → EVIDENCE → LINEAGE → TOPOLOGY → EXECUTION → COGNITION
Not the reverse.
What still does NOT exist yet:
• real autonomous reasoning
• exploit evolution cognition
• adaptive replay continuation
• self-improving heuristics
• distributed offensive runtime mesh
• exploit prediction engine
• architecture-level cognition
And that part matters.
Because the goal is not to build “AI theater”.
The goal is to build:
a reality-safe offensive runtime intelligence organism.
Next major milestones:
→ real replay engine
→ session intelligence
→ auth propagation analysis
→ adaptive mutation
→ runtime graph propagation
→ exploit pattern memory
→ temporal attack reasoning
→ architecture cognition
The future of offensive security will not belong to systems that merely scan applications.
It will belong to systems that understand how trust behaves under runtime pressure.
4 reactions · 4 comments
Comments
Ikechukwu O.: Spot on, Damian. Shifting from AI-first guessing to runtime-telemetry-first truth is a massive paradigm shift. 'AI theater' falls apart on complex networks, but tracking evidence lineage and trust under actual runtime pressure changes the game entirely. Looking forward to seeing that replay engine and session intelligence milestone drop!
Damian K.: Ikechukwu Justin Onyekwere That’s the core architectural pivot. Most current “AI security” stacks still operate on: prompts, summaries, confidence scoring, CVE enrichment. But real enterprise compromise rarely happens because of a single alert. It happens because: trust propagates incorrectly across runtime boundaries. That’s why upcoming RedNode milestones are heavily focused on: → replay-driven
Ikechukwu O.: Damian Kuś a great approach you have there. I am enjoying your security approach 😀
Damian K.: Ikechukwu Justin Onyekwere najbardziej wyróżnia mnie to, że RedNode mimo automatyzacji i autonomii jest w pełni kontrolowany przez operatora, RedNode potrzebuje zgody na agresywne działania, potwierdzenia łańcucha ataku zgodego z in-scope, zgodnego z NDA itp. RedNode sam się rozwija, uczy, mutuje dla tego wbudowałem mu tryby safe mode i agressive oraz scenariusze działań typowo pod konkretne opera