Posted in Security Operations
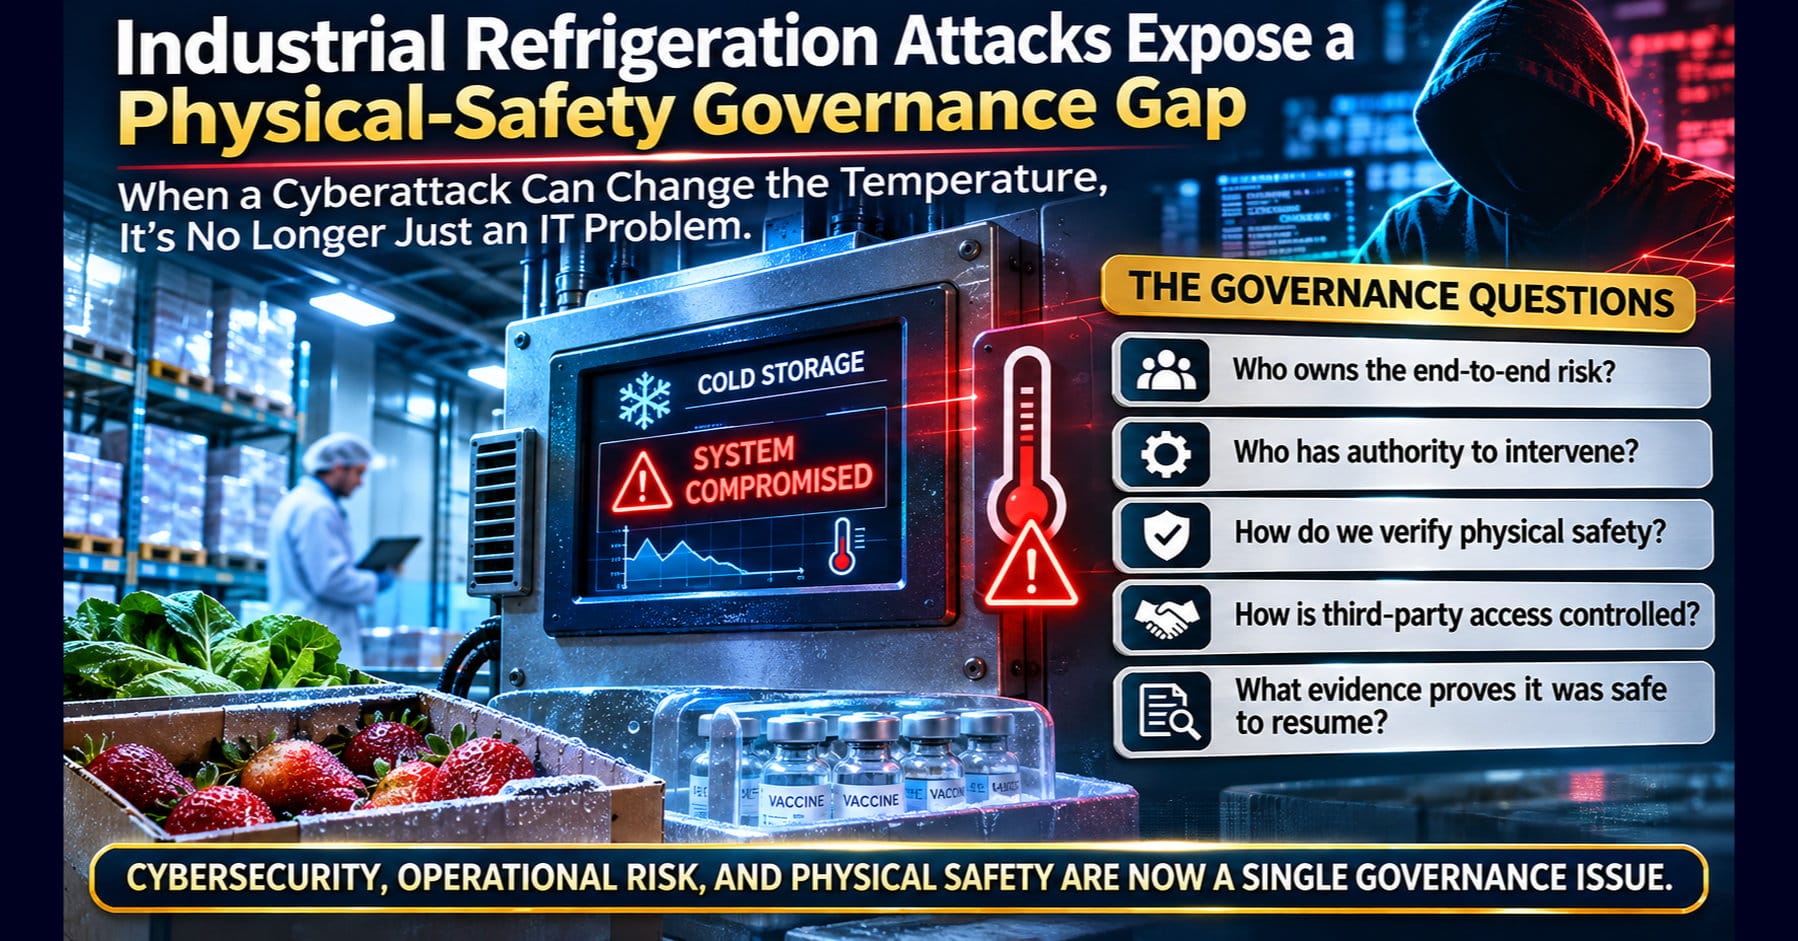
Industrial Refrigeration Cyberattacks Expose a Critical Physical-Safety Governance Gap
Victor Font — Keynote Speaker | Strategic Technology Leader | Fractional CIO | IT & Cyber Governance Expert | Published Author | FedRAMP Readiness | Board-Level Advisor | Digital Transformation | Enterprise WordPress/Formidable Forms
A cyberattack against an industrial refrigeration system may never involve stolen data, encrypted servers, or a ransom demand.
An attacker may simply change a temperature setting.
The consequences can include spoiled food, compromised medical supplies, damaged equipment, and interrupted critical operations.
And restoring the technology doesn't necessarily reverse the damage.
Recent warnings about attacks targeting industrial refrigeration and cold-chain systems expose a significant cybersecurity governance problem.
Who owns the risk when digital systems control physical processes?
Is it cybersecurity, operations, facilities management, quality assurance, or the equipment supplier?
In this Cyber Brief, I examine why boards must establish end-to-end accountability, intervention authority, independent safety verification, and evidence that operations can safely resume.
When a cyberattack creates physical consequences, technical recovery is not proof of operational safety.
https://cybergovernancecenter.com/industrial-refrigeration-cyberattacks-governance-gap/
5 reactions · 0 comments