💡A quick lesson from a recent Web Cache Deception (WCD) finding: Don't trust cache headers alone. Before I…
John O. — Security Researcher | Penetration Tester | Reverse Engineer
💡A quick lesson from a recent Web Cache Deception (WCD) finding: Don't trust cache headers alone.
Before I go on, within the space of 2 weeks, I found 2 WCD vulnerabilities on two different targets!
In addition to these two, on a recent target I found another WCD vulnerability. From the server's response on the /profile endpoint, I saw:
👉 "Cache-Control: no-cache, no-store, must-revalidate"
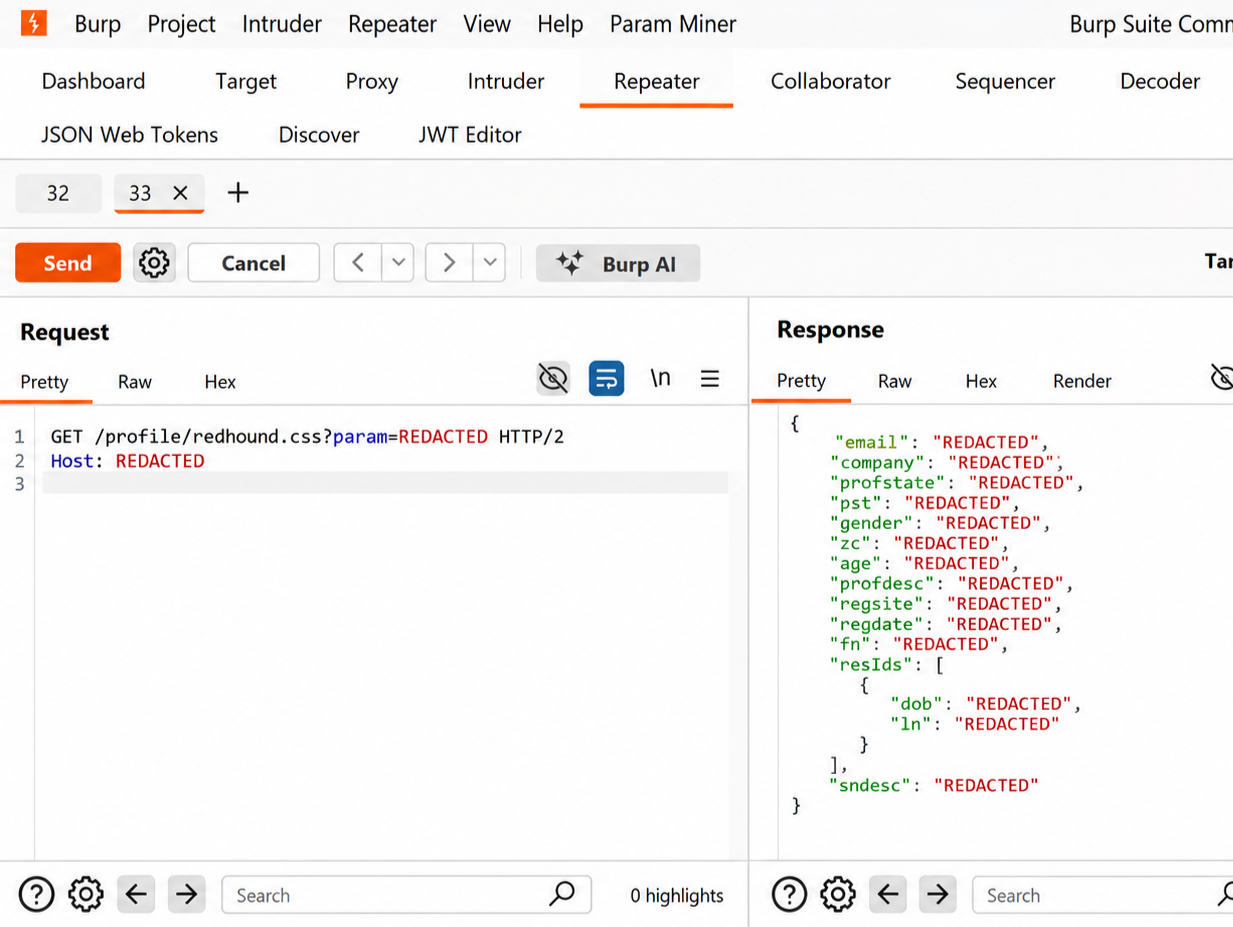
At first glance, it looked like authenticated content could not be cached. However, after testing different URL patterns and URL-encoded WCD payloads, I discovered a cache misconfiguration that resulted in an authenticated response being cached.
As shown in the attached screenshot, I was able to retrieve the cached response without cookies or an Authorization header. I also made use of incognito mode on my web browser and the response still contained the sensitive user PII.
✅Takeaway: always verify actual cache behavior, not just the headers.
#BugBounty #WebCacheDeception #CyberSecurity #AppSec #Pentesting #OffSec #BurpSuite
1 reactions · 0 comments
Topics: #bugbounty, #burpsuite, #appsec, #offsec, #cybersecurity, #webcachedeception, #pentesting