The "Glass House" of cyber security is surprisingly common. Their pitch: A self-proclaimed cybersecurity…
Mark C. — Executive Technology & Cyber Leader | CIO | Cyber, Governance & Operational Resilience
The "Glass House" of cyber security is surprisingly common.
Their pitch:
A self-proclaimed cybersecurity "expert" posts a long thread on "essential hardening."
The reality:
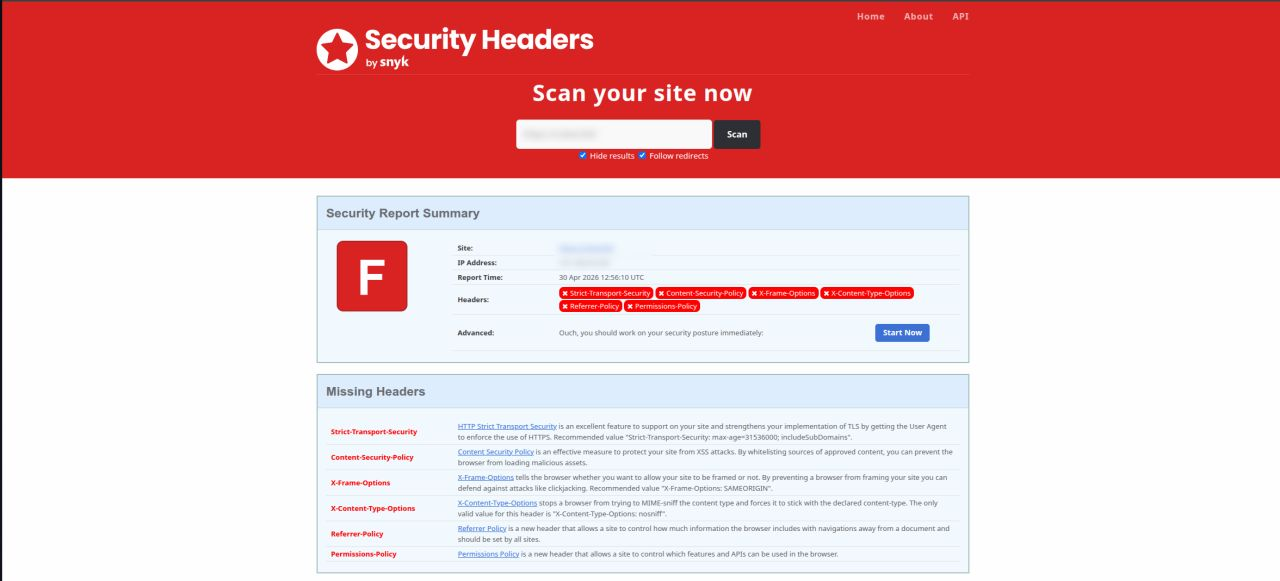
You visit their website. It is missing basic HTTP security headers. No Content Security Policy (CSP). No HSTS. No X-Frame-Options. NOTHING
The fallout:
The Irony of "Expertise"
Selling security services while leaving your own front door unlocked isn't just an oversight. It is a brand risk.
If you are preaching to others about risk mitigation, your own digital footprint should be the blueprint. You cannot secure an enterprise if you cannot secure a WordPress site or a personal portfolio.
The Minimum Baseline:
Before advising others, check your own site for:
Strict-Transport-Security: To enforce HTTPS.
Content-Security-Policy: To prevent XSS and data injection.
X-Content-Type-Options: To stop MIME-sniffing.
Referrer-Policy: To control how much info you leak to other sites.
Practice what you preach
Authenticity in this industry starts with your own config files!
1 reactions · 0 comments