AWS Pentesting - Flaws Level 5 - Exploiting AWS IMDS via SSRF
Julian X. — Cyber Security Analyst
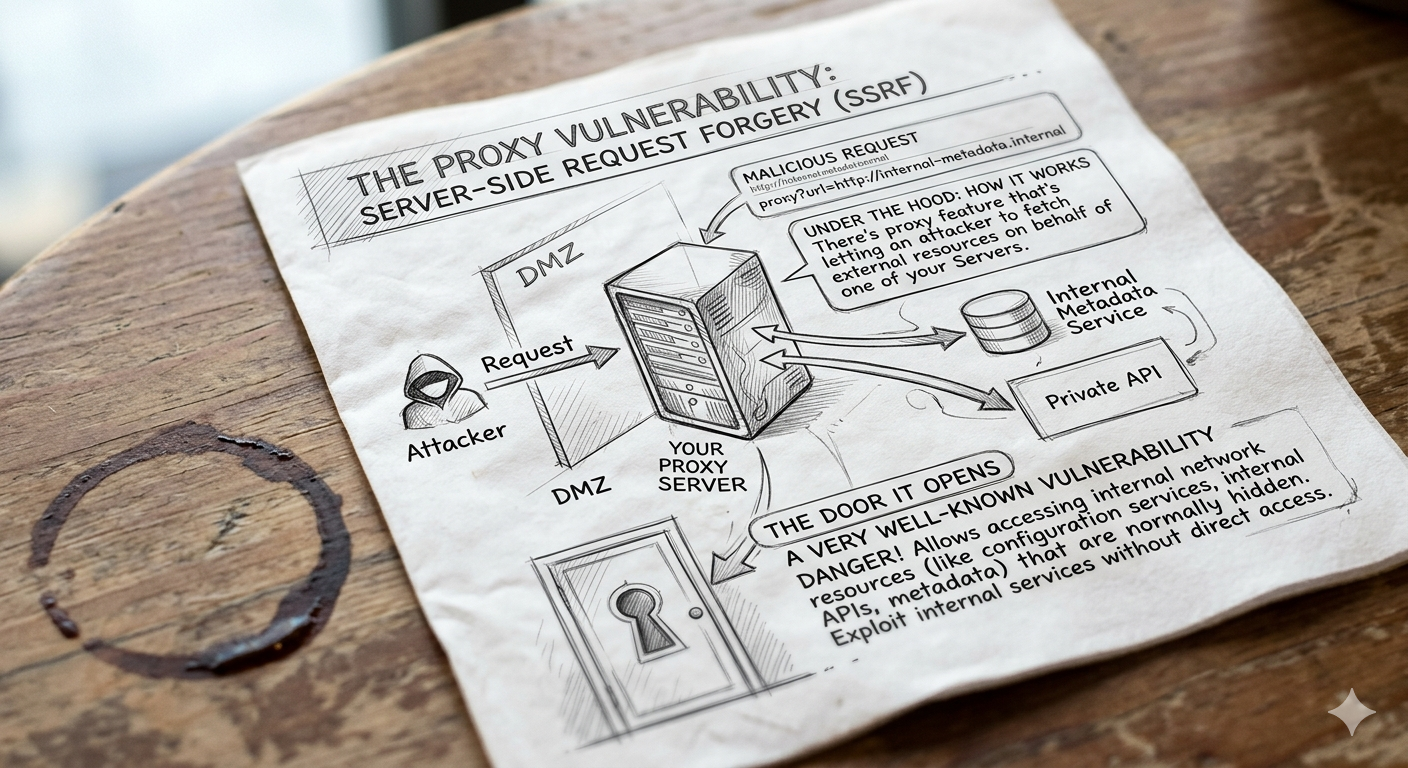
In this level, you’ll deal with a proxy feature that’s letting an attacker to fetch external resources on behalf of one of your EC2 instances. This may not look dangerous at first, but under the hood it opens the door to a very well-known vulnerability. https://jjeuribe.github.io/posts/aws-pentesting-flaws-level-5-exploiting-aws-imds-via-ssrf/
0 reactions · 0 comments