Posted in GRC
📢 Shared from Cybersecurity Governance & Executive Accountability EXECUTIVE DECISION SCENARIO | #1 The…
Victor Font — Keynote Speaker | Strategic Technology Leader | Fractional CIO | IT & Cyber Governance Expert | Published Author | FedRAMP Readiness | Board-Level Advisor | Digital Transformation | Enterprise WordPress/Formidable Forms
📢 Shared from Cybersecurity Governance & Executive Accountability
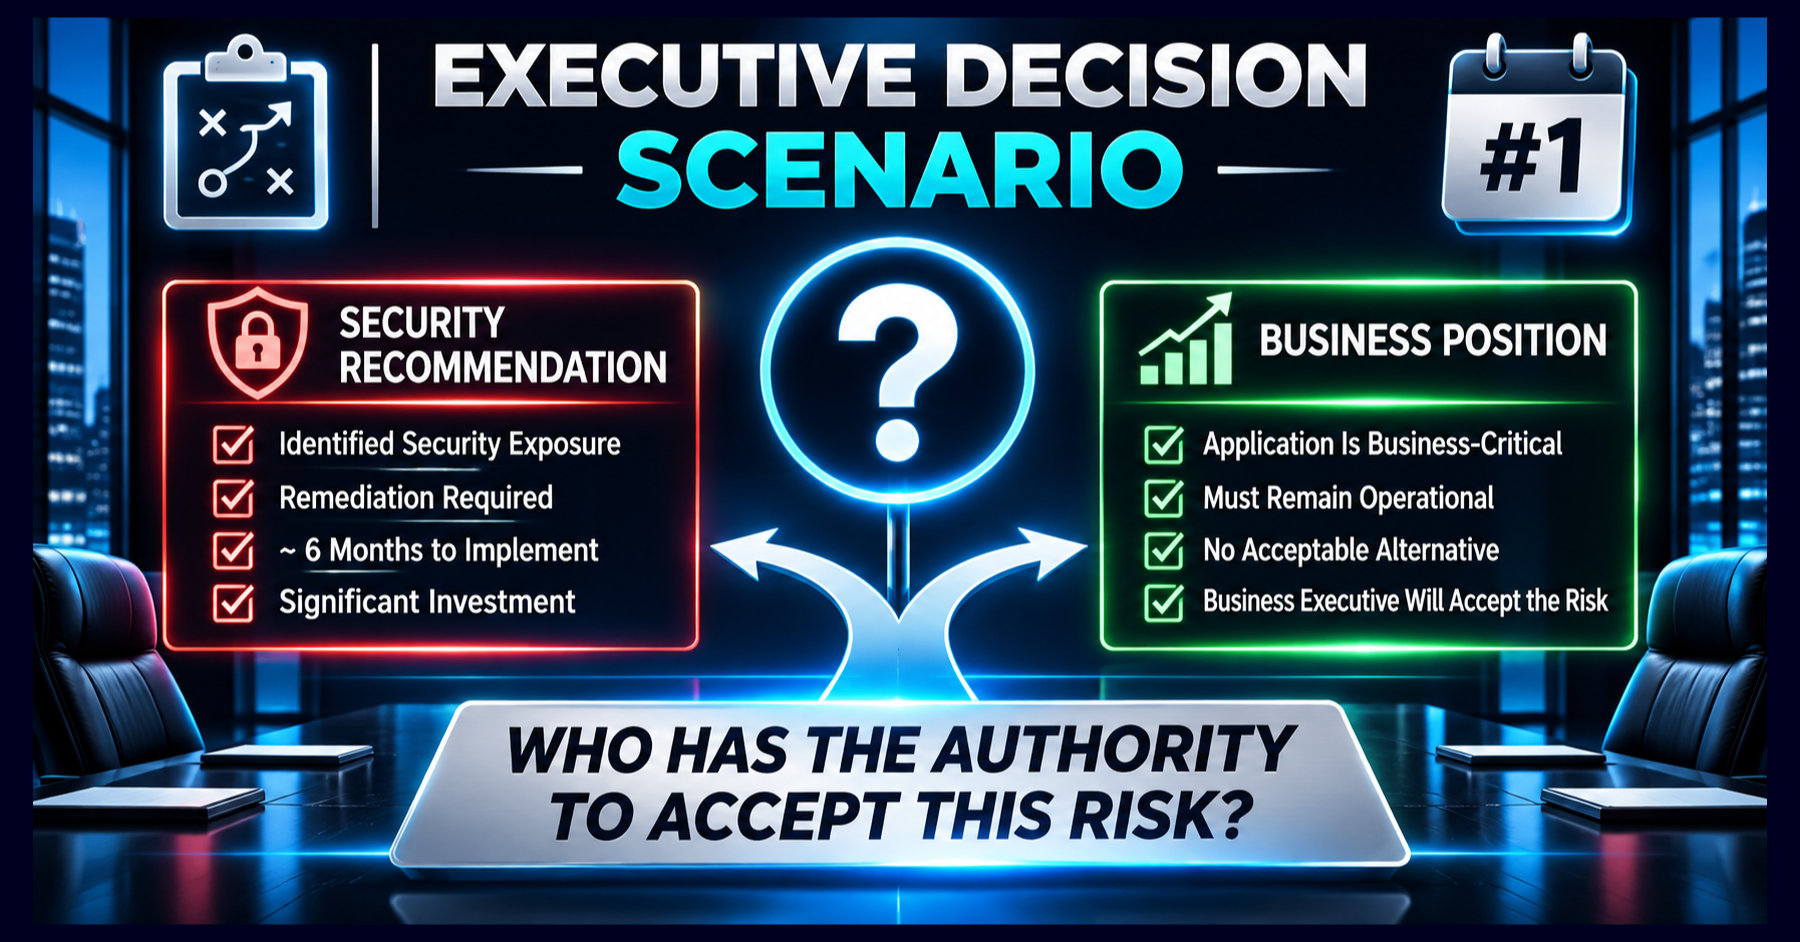
EXECUTIVE DECISION SCENARIO | #1
The Security Team Says No. The Business Says We Have No Choice.
A business-critical application fails to meet the organization's security requirements.
The security team identifies the exposure and recommends remediation.
The CIO confirms that remediation will require six months and substantial investment.
The business executive insists the application must remain operational.
The CISO refuses to recommend accepting the risk.
The business executive responds, "Then I'll accept it myself."
Here's the complication.
The business executive owns the application and its operating budget. But the potential consequences extend beyond that business unit, affecting shared infrastructure, customer information, and enterprise operations.
Who actually has the authority to accept this risk?
A. The business executive, because the application supports their operations.
B. The CISO, because cybersecurity risk falls within the security function.
C. The CIO, because IT owns the underlying technology.
D. The designated enterprise risk authority, based on established delegation limits and the potential consequences.
Or is there a better answer?
I'm particularly interested in how your organization handles disagreements between business ownership and enterprise risk authority.
Does owning a business process give an executive the authority to accept every risk that process creates?
#CybersecurityGovernance #ExecutiveAccountability #CyberRisk #GRC #RiskAcceptance #DecisionAuthority
2 reactions · 3 comments
Topics: #cyberrisk, #decisionauthority, #cybersecuritygovernance, #executiveaccountability, #riskacceptance, #grc
Comments
Ilias M.: I’d say D. The fundamental principle of cybersecurity governance is that risk acceptance authority must align with the scope and potential impact of the risk, not simply ownership of the application or its budget. In this scenario, the potential consequences extend beyond the business unit, affecting shared infrastructure, customer information, and enterprise operations. Therefore, the business ex
Victor Font: Ilias Mavropoulos Ilias, exactly. You've identified the distinction that often gets overlooked: business ownership does not automatically confer enterprise-wide risk acceptance authority. The business executive certainly has a role in evaluating the operational consequences, but when exposure crosses organizational boundaries, the decision must follow established enterprise risk authority and tole
Ilias M.: Victor Font My pleasure! I get easily triggered by common business misconceptions so couldn’t really resist in commenting 😃