Found a GraphQL endpoint during recon and not sure where to start? Here's a quick cheat sheet of the 4…
John O. — Security Researcher | Penetration Tester | Reverse Engineer
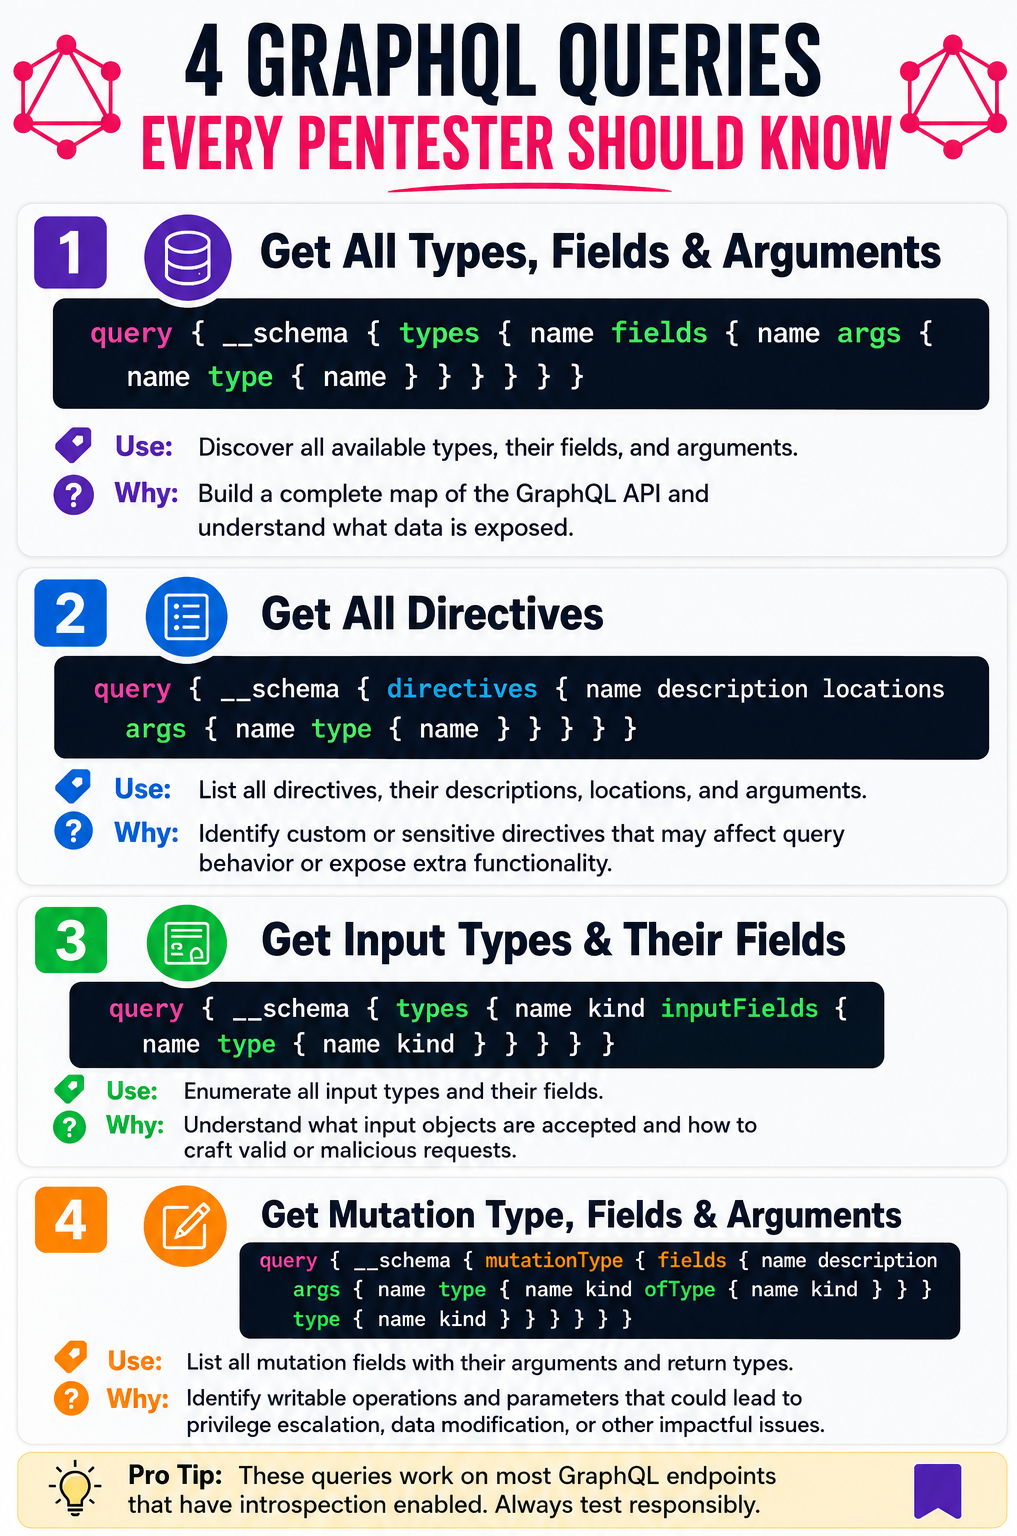
Found a GraphQL endpoint during recon and not sure where to start?
Here's a quick cheat sheet of the 4 queries I use most often to map the schema, discover inputs, and identify mutations.
Nothing fancy though, just a simple reference that can save time when testing GraphQL endpoints.
Hope it helps someone in their next hunt. 🚀
#BugBounty #CyberSecurity #AppSec #GraphQL #APIsecurity #EthicalHacking #BugBountyHunter #SecurityTesting #Recon #WebSecurity
3 reactions · 0 comments
Topics: #bugbounty, #bugbountyhunter, #websecurity, #ethicalhacking, #appsec, #graphql, #apisecurity, #cybersecurity, #securitytesting, #recon