Posted in GRC
Everyone Owns Cybersecurity. So Why Is Nobody Accountable?
Victor Font — Keynote Speaker | Strategic Technology Leader | Fractional CIO | IT & Cyber Governance Expert | Published Author | FedRAMP Readiness | Board-Level Advisor | Digital Transformation | Enterprise WordPress/Formidable Forms
The Dangerous Difference Between Shared Responsibility and Executive Accountability
Ask almost any executive whether cybersecurity is everyone's responsibility, and the answer will be yes.
Employees must recognize phishing attempts.
IT teams must maintain secure infrastructure.
Developers must build secure applications.
Security professionals must identify threats and manage vulnerabilities.
Business leaders must understand operational risk.
Executives must support the cybersecurity program.
The board must exercise oversight.
Everyone has a role.
That sounds like a mature approach to cybersecurity governance.
But there is a problem.
When everyone is responsible for cybersecurity, it becomes remarkably easy for nobody to be accountable for a particular decision or outcome.
The distinction between responsibility and accountability is not semantic.
It determines whether an organization can identify who had the authority, obligation, and ability to address a material cybersecurity risk before that risk became an incident.
The Shared Responsibility Illusion
Consider an organization that experiences a significant data breach involving a third-party service provider.
The security team evaluated the vendor's technical controls.
Procurement completed the onboarding process.
Legal reviewed the contract.
IT approved the integration.
The business unit sponsored the relationship.
Compliance verified that required assessments were completed.
Every department fulfilled its assigned responsibilities.
Yet the vendor retained excessive access to sensitive enterprise information, and that access contributed to the breach.
Who was accountable for the cumulative exposure?
Security evaluated technical controls but did not own the business relationship.
Procurement managed the acquisition but did not control the integration.
Legal reviewed contractual protections but did not validate operational safeguards.
IT implemented the connection according to approved requirements.
The business sponsor assumed the technical specialists had addressed the risk.
Every function completed its assigned task. The enterprise still failed to govern the risk created by the relationship between those tasks.
This is the accountability gap hidden inside many otherwise sophisticated cybersecurity programs.
Responsibility Is Distributed. Accountability Must Be Traceable.
Cybersecurity requires collaboration across organizational boundaries.
No single executive can personally perform every activity necessary to protect the enterprise.
Distributed responsibility is therefore unavoidable.
Distributed accountability without clearly defined decision ownership is not.
A mature governance model distinguishes between the people who perform activities, the individuals who provide specialized advice, and the authorities who make consequential decisions.
For example, a security architect may recommend restricting a third-party integration.
An application owner may explain why the integration requires elevated access.
Legal may identify contractual consequences.
The business executive may determine whether the operational benefits justify the residual exposure.
Those responsibilities are related, but they are not interchangeable.
The organization must identify who possesses the authority to make the final decision and who remains accountable for ensuring that the resulting obligations are fulfilled.
Collaboration should inform decisions. It should not obscure ownership of those decisions.
The RACI Matrix Is Not Enough
Many organizations rely on RACI matrices to define who is Responsible, Accountable, Consulted, and Informed.
RACI can be useful for clarifying operational roles.
But a completed matrix does not necessarily establish effective cybersecurity governance.
Consider a system designated as business-critical.
The RACI matrix identifies an accountable executive.
A serious vulnerability is discovered.
Security recommends immediate remediation.
Operations requests a delay.
The accountable executive approves an exception.
Three months later, the vulnerability remains unresolved.
The matrix may accurately identify the executive who approved the exception.
But it does not necessarily establish whether the executive understood the consequences, whether compensating controls were implemented, or whether anyone reassessed the decision as conditions changed.
The organization has documented accountability as a role assignment.
It has not necessarily demonstrated accountability as an operating discipline.
A name in the Accountable column is the beginning of governance, not evidence that governance occurred.
Accountability Requires More Than Ownership
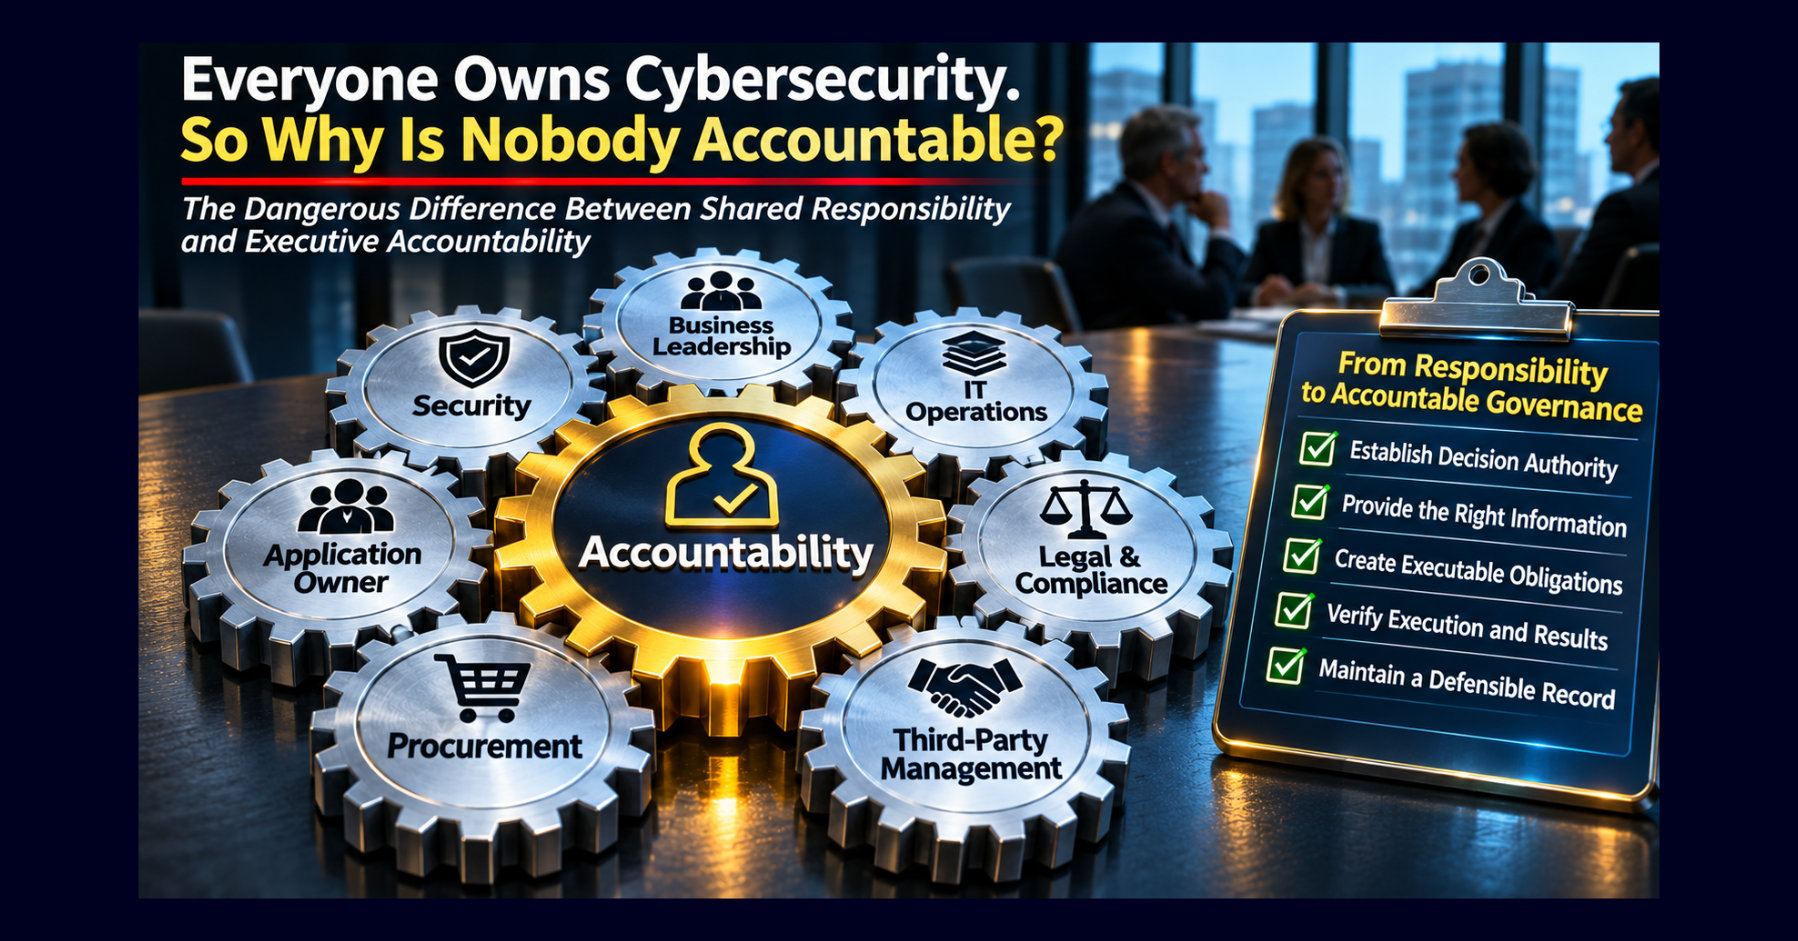
For executive accountability to become operationally meaningful, five conditions should exist.
1. Decision authority must be explicit.
An accountable executive needs clearly defined authority over the decisions assigned to that role.
Holding someone accountable for outcomes they cannot meaningfully influence creates a governance contradiction.
2. Information must reach the decision-maker.
Accountability requires access to timely, relevant, and understandable information.
An executive cannot make an informed risk decision when material facts remain isolated within technical teams or buried in reporting systems.
3. Decisions must produce obligations.
Approving a remediation plan, accepting an exception, or authorizing a third-party relationship should create specific actions, owners, deadlines, and review requirements.
A decision without executable obligations is little more than an expression of intent.
4. Execution must be verified.
Management must establish whether approved actions occurred and whether they produced the intended results.
Completion reports are useful, but consequential controls may require independent validation.
5. Accountability must survive organizational boundaries.
Cybersecurity risks frequently span departments, vendors, platforms, and business processes.
Governance must preserve traceability across those boundaries rather than allowing responsibility to disappear at each handoff.
These conditions transform accountability from an organizational label into a functioning management system.
The Handoff Problem
One of the most persistent cybersecurity governance weaknesses appears during transitions between teams.
Security identifies a vulnerability.
IT accepts the remediation assignment.
The application owner requests a maintenance window.
Operations postpones the window because of business demand.
The issue returns to security as an unresolved exception.
Each handoff is documented.
Each team can explain its actions.
But the vulnerability remains.
Who is accountable for resolving the conflict between security requirements and business priorities?
Without an established decision owner and escalation mechanism, the organization can continue transferring responsibility without resolving the underlying risk.
This is why cybersecurity governance cannot be evaluated solely by examining the performance of individual departments.
The quality of governance is often revealed at the boundaries between organizational responsibilities.
Those boundaries are where assumptions become dependencies, decisions become delays, and unresolved risks become normalized.
Evidentiary Architecture™ Connects Responsibility to Results
This accountability problem is one of the reasons I developed Evidentiary Architecture™.
Traditional governance documentation often records policies, organizational structures, meeting minutes, and compliance activities.
Those records have value.
But they do not always demonstrate how a specific governance decision moved through the organization and produced a verified outcome.
Evidentiary Architecture™ addresses that weakness by connecting the evidence generated throughout the decision lifecycle.
For a material cybersecurity issue, the organization should be able to trace:
Risk identified → Accountable authority established → Decision recorded → Obligations assigned → Actions executed → Results verified → Evidence preserved.
The important feature is continuity.
The evidence should not terminate when one department completes its portion of the work.
It should remain connected across organizational handoffs until the governance obligation has been fulfilled, formally revised, or escalated.
This makes accountability demonstrable.
It also provides executives and boards with a more meaningful understanding of whether governance processes are operating effectively.
The Boardroom Accountability Test
Boards frequently receive cybersecurity presentations describing program maturity, control performance, incident trends, and regulatory compliance.
Those reports may provide valuable visibility.
But they rarely reveal whether accountability remains intact across complex organizational relationships.
A board seeking meaningful assurance should ask management questions such as:
Who is accountable for resolving material cybersecurity risks that cross departmental boundaries?
How are disagreements between security requirements and business priorities resolved?
What prevents an unresolved risk from circulating indefinitely between departments?
How does management verify that decisions have been implemented?
Can the organization reconstruct the chain of accountability for a significant risk or incident?
These questions do not require directors to become cybersecurity engineers.
They require directors to understand whether management has established a coherent system for governing enterprise risk.
That is a fundamental oversight responsibility.
Accountability Is Tested When Something Goes Wrong
Following a significant cybersecurity incident, organizations frequently reconstruct the sequence of events.
Who discovered the vulnerability?
Who received the notification?
Who approved the exception?
Who owned the affected system?
Who was responsible for implementing the corrective action?
These questions matter.
But the most important question may be different.
At what point did the organization lose accountable control over the risk?
Perhaps the risk was assigned without sufficient authority.
Perhaps an executive approved an exception without understanding its implications.
Perhaps remediation stalled between departments.
Perhaps compensating controls were assumed to exist but never verified.
Perhaps everyone believed someone else was monitoring the exposure.
The failure may not have originated with a single negligent individual.
It may have emerged from an organizational system that distributed responsibilities without preserving accountability.
That is a governance failure.
And it cannot be corrected simply by assigning more tasks or adding another approval layer.
The Question Every Executive Should Answer
There is nothing wrong with saying cybersecurity is everyone's responsibility.
As a statement about organizational participation, it is entirely appropriate.
But it is not a substitute for accountable governance.
Every material cybersecurity risk should have an identifiable decision authority.
Every consequential decision should produce defined obligations.
Every obligation should have an accountable owner.
And every significant outcome should be supported by evidence sufficient to establish what occurred.
The goal is not to concentrate every cybersecurity decision in one executive's office.
It is to ensure that accountability remains clear even when responsibility is distributed across the enterprise.
Everyone can contribute to cybersecurity. But for every material risk, the organization must be able to identify who is accountable for the decision—and demonstrate what happened afterward.
That is the difference between a culture of shared responsibility and an architecture of executive accountability.
Discussion
Have you encountered a cybersecurity risk that remained unresolved even though every department involved had completed its assigned responsibilities?
Where did accountability break down—at the decision, the handoff, or the verification of the outcome?
#CybersecurityGovernance #ExecutiveAccountability #CyberRisk #GRC #RiskManagement #BoardOversight #CyberLeadership #EvidentiaryArchitecture
0 reactions · 0 comments
Topics: #cyberrisk, #cyberleadership, #cybersecuritygovernance, #executiveaccountability, #evidentiaryarchitecture, #riskmanagement, #boardoversight, #grc