Posted in GRC
📢 Shared from Cybersecurity Governance & Executive Accountability When Every Cybersecurity Exception Is…
Victor Font — Keynote Speaker | Strategic Technology Leader | Fractional CIO | IT & Cyber Governance Expert | Published Author | FedRAMP Readiness | Board-Level Advisor | Digital Transformation | Enterprise WordPress/Formidable Forms
📢 Shared from Cybersecurity Governance & Executive Accountability
When Every Cybersecurity Exception Is Approved, Who Owns the Cumulative Risk?
Cybersecurity Governance & Executive Accountability | Governance in Practice
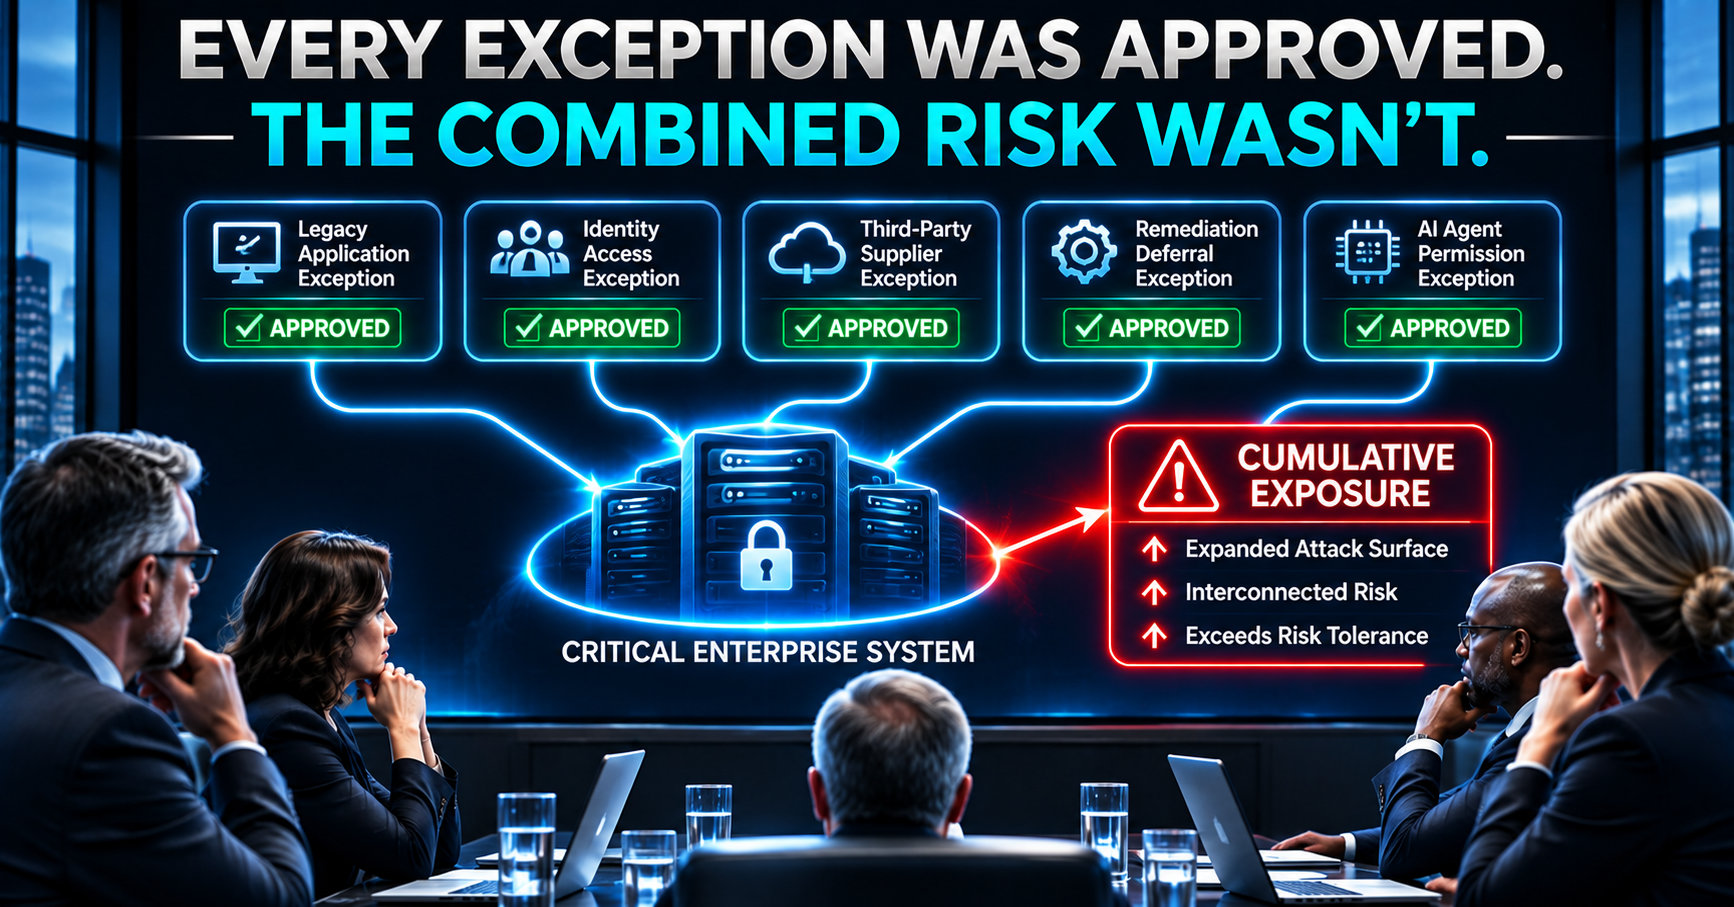
Every cybersecurity exception was properly approved.
The business owners documented their justifications. The security team evaluated the exposures. The appropriate executives authorized the deviations. The risk register reflected the decisions.
From a procedural standpoint, everything appeared to be working.
Yet over time, the organization accumulated dozens of exceptions affecting critical applications, identity controls, legacy infrastructure, third-party services, and sensitive information.
Each exception was considered acceptable in isolation.
Together, they created an enterprise exposure that nobody had explicitly evaluated or authorized.
The organization governed individual risk decisions but failed to govern their cumulative consequences.
This is one of the more subtle weaknesses in enterprise cybersecurity governance.
And it raises an important question.
Can every individual risk acceptance decision be legitimate while the organization's overall risk position becomes unacceptable?
Absolutely.
The Problem With Evaluating Risk in Isolation
Consider a large enterprise operating across multiple business units.
One division receives approval to defer multifactor authentication for a legacy application.
Another receives an exception allowing extended privileged access because an operational system cannot support modern identity controls.
A third accepts a supplier's inability to meet contractual security requirements.
A fourth postpones remediation of a critical vulnerability because the affected application is scheduled for replacement.
Each decision is reviewed independently.
Each business owner provides a reasonable justification.
Each approving authority operates within established delegation limits.
But what happens when those systems share infrastructure, identities, suppliers, or data?
What happens when the same privileged accounts can access multiple applications?
What happens when the supplier with inadequate controls supports several critical business processes?
And what happens when the deferred vulnerability creates an attack path into systems already operating under other security exceptions?
The individual decisions may appear defensible.
The combined exposure may not be.
Risk does not respect organizational boundaries simply because governance authority has been divided among departments.
This is why enterprise cybersecurity governance must evaluate more than individual risk acceptance records.
It must understand how accepted exposures interact.
Delegated Authority Does Not Eliminate Enterprise Accountability
Organizations appropriately delegate cybersecurity decision authority.
A business unit executive may accept defined categories of risk within established tolerance.
A technology executive may authorize limited operational exceptions.
An enterprise risk committee may approve exposures exceeding departmental thresholds.
This delegation enables timely decisions without requiring senior leadership to approve every operational deviation.
But delegated authority creates a governance obligation.
The organization must ensure that decisions made independently do not collectively exceed enterprise risk appetite or tolerance.
Consider five executives, each authorized to accept a particular level of cybersecurity exposure.
Each approves an exception affecting a different business application.
No individual exceeds delegated authority.
Yet the applications share a common identity provider and depend on the same network environment.
An attacker exploiting one weakness may be able to leverage the others.
The enterprise exposure is not necessarily equal to the sum of five independently assessed risks.
It may be substantially greater because of shared dependencies and potential attack paths.
Delegated authority must operate within an enterprise governance structure capable of identifying cumulative and interconnected exposure.
Otherwise, organizations can remain procedurally compliant with their approval processes while drifting beyond acceptable risk boundaries.
The Risk Register May Not Reveal the Problem
Enterprise risk registers are valuable instruments for documenting and monitoring exposures.
But their usefulness depends on the information architecture supporting them.
Many registers organize risks by business unit, application, control category, or accountable owner.
This makes individual exposures easier to manage.
It can also make relationships between exposures harder to recognize.
A vulnerability exception appears in one record.
An identity management exception appears in another.
A third-party security deficiency appears in a separate supplier assessment.
A business continuity weakness appears in yet another system.
Each record has an owner, a status, and a review date.
But where does the organization evaluate the combined exposure?
Who determines whether these weaknesses affect the same critical business service?
Who identifies common dependencies?
Who evaluates whether one exception undermines the compensating controls supporting another?
And who possesses authority to address the resulting enterprise risk?
A risk register that documents individual exposures without revealing their relationships can create an incomplete picture of organizational risk.
The issue is not necessarily poor data quality.
It may be inadequate risk architecture.
Compensating Controls Can Create Hidden Dependencies
Compensating controls frequently support cybersecurity exceptions.
An organization may accept delayed remediation because network segmentation limits exposure.
It may approve a legacy authentication exception because privileged access monitoring provides additional oversight.
It may continue using a deficient supplier because contractual restrictions and enhanced monitoring reduce the expected consequences.
These arrangements can be appropriate.
But compensating controls introduce dependencies that must themselves be governed.
Suppose several accepted risks rely on the same network segmentation architecture.
If that architecture changes or becomes ineffective, multiple acceptance decisions may lose their supporting justification simultaneously.
Similarly, several exceptions may depend on a shared monitoring capability.
A failure in that capability could invalidate the assumptions supporting multiple approvals.
When multiple risk acceptance decisions depend on the same compensating control, that control becomes a point of concentrated governance exposure.
Organizations should be able to identify these relationships.
They should also understand what happens when a shared control fails, deteriorates, or changes.
Otherwise, an organization may continue treating numerous accepted risks as valid even after the common safeguard supporting them is no longer effective.
Cumulative Risk Is Not Simply a Mathematical Exercise
It is tempting to approach this problem by adding risk scores together.
Five moderate risks produce a combined score.
Ten exceptions create a higher aggregate number.
A dashboard displays the result.
But cybersecurity risk aggregation is more complicated.
Risk ratings are often ordinal rather than mathematically additive.
Different assessment methods may use incompatible scales.
Some exposures overlap.
Others share dependencies.
Certain combinations create new attack paths or amplify business consequences.
A collection of vulnerabilities affecting unrelated systems may present a different enterprise exposure than the same number affecting interconnected critical infrastructure.
The objective is not merely to calculate a larger number.
It is to understand whether individually accepted exposures interact in ways that change the organization's overall risk position.
This requires technical analysis, business context, dependency mapping, and governance judgment.
It also requires decision-makers who possess authority over the enterprise consequences—not merely the individual systems involved.
Who Owns the Combined Exposure?
This is where the governance problem becomes especially important.
Each exception may have an assigned owner.
Each approval may be valid.
Each business unit may be operating within its delegated authority.
But who owns the cumulative exposure?
The CISO may identify the relationships.
Enterprise risk management may evaluate the broader consequences.
Technology leadership may understand the shared infrastructure.
Business executives may understand the operational dependencies.
An executive risk committee may possess the authority to resolve competing priorities.
These roles must work together.
But collaboration alone is insufficient.
The governance operating model must establish who is accountable for evaluating cumulative risk and who possesses authority to require action when combined exposures exceed acceptable boundaries.
That may involve restricting additional exceptions, revisiting existing approvals, requiring compensating controls, or escalating the issue to senior executive leadership.
The authority to approve individual exceptions must be accompanied by an enterprise mechanism for governing their collective consequences.
Without that mechanism, local decisions can create enterprise exposures that no single approving authority intended to authorize.
NIST CSF 2.0 GOVERN and Enterprise Risk Strategy
The NIST Cybersecurity Framework 2.0 provides a useful foundation for addressing this challenge.
Its GOVERN function emphasizes organizational context, risk management strategy, roles and authorities, policy, and oversight.
These elements are particularly relevant to cumulative risk.
Organizational context helps establish the critical business services, dependencies, and stakeholders affected by cybersecurity exposures.
Risk management strategy provides the enterprise boundaries within which risk decisions should occur.
Roles and authorities establish who may accept exposures and who must address matters exceeding delegated limits.
Policies define expectations for exceptions, monitoring, and escalation.
Oversight evaluates whether the organization's risk management approach remains effective.
The framework does not prescribe a universal method for aggregating cybersecurity exceptions.
Organizations must design approaches appropriate to their operating environments.
But the governance principle is clear.
Enterprise risk appetite cannot be meaningfully enforced if the organization evaluates only individual decisions and ignores their combined consequences.
This is where governance must connect local authority with enterprise oversight.
Evidentiary Architecture™ and the Relationships Between Decisions
This problem also reveals why governance evidence cannot be limited to isolated approval records.
An organization may possess complete documentation for every exception.
It may demonstrate that each decision was authorized.
It may show that required reviews occurred.
Yet those records may not explain how the decisions affected one another.
Evidentiary Architecture™ addresses this broader challenge by emphasizing the relationships among governance decisions, organizational authority, supporting evidence, and subsequent outcomes.
For cumulative risk governance, the evidentiary structure should support several questions.
Which exceptions affect the same business service?
Which accepted risks depend on common infrastructure, identities, suppliers, or compensating controls?
Which decisions were made under separate delegated authorities but contribute to the same enterprise exposure?
What changes would invalidate multiple acceptance decisions?
Who evaluated the combined consequences?
What authority supported the resulting enterprise decision?
What evidence demonstrates that required actions were implemented and reviewed?
These relationships transform a collection of approval records into a more useful governance evidence system.
The organization can examine not only whether individual decisions were authorized, but whether their combined consequences received appropriate evaluation and oversight.
Defensible governance requires evidence of how consequential decisions interact—not merely proof that each decision occurred.
Autonomous AI Creates Another Dimension of Cumulative Exposure
Consider an organization deploying autonomous AI agents across several business functions.
One agent receives permission to retrieve customer information.
Another can modify business records.
A third can initiate financial transactions.
A fourth can communicate with external suppliers.
Each deployment is independently evaluated and approved.
Each agent operates within its assigned permissions.
But what happens when the agents share data, tools, workflows, or service identities?
What happens when the output of one agent becomes the instruction or input for another?
What happens when individually authorized actions combine into a consequential business outcome that no single approval anticipated?
The organization may have governed each agent independently while failing to evaluate the authority and exposure created by their interaction.
Individually authorized autonomous actions can produce collectively significant consequences.
This is not merely a technical orchestration issue.
It is a governance problem involving delegated authority, dependency analysis, cumulative exposure, and executive accountability.
As AI systems become more interconnected, organizations will need governance mechanisms capable of evaluating their combined operational authority.
The Boardroom Test
Boards should not be expected to examine every cybersecurity exception.
But they should receive sufficient information to understand whether material concentrations of accepted risk are emerging.
A dashboard showing 47 approved exceptions provides limited insight.
A more meaningful report might identify that 18 exceptions affect the same critical business service, 11 depend on a shared compensating control, and several collectively create exposure exceeding established tolerance.
Those figures are illustrative, but the distinction matters.
The first report describes administrative activity.
The second supports enterprise risk oversight.
Boards and executive leadership should understand whether management has established mechanisms for identifying concentrations, dependencies, and interactions among accepted risks.
They should also understand how those mechanisms influence decisions.
The governance question is not simply whether exceptions were properly approved. It is whether the enterprise remains within acceptable risk boundaries after those approvals are considered together.
A Practical Test for the Enterprise
Select the organization's most significant currently approved cybersecurity exceptions.
Instead of reviewing them individually, examine their relationships.
Identify the business services they affect.
Map shared systems, identities, suppliers, and compensating controls.
Determine whether combinations create additional attack paths or amplify business consequences.
Evaluate whether the combined exposure remains within enterprise risk tolerance.
Then identify who possesses authority to require corrective action when the cumulative exposure becomes unacceptable.
Finally, examine the evidence.
Can the organization demonstrate that the combined risk was evaluated, that appropriate authorities considered the consequences, and that required decisions were made?
If not, the organization may have a functioning exception approval process without a functioning enterprise risk aggregation capability.
And those are not the same thing.
A Question for the Community
Most organizations have processes for approving individual cybersecurity exceptions.
Far fewer can demonstrate how they evaluate the cumulative exposure created by multiple accepted risks.
Does your organization assess cybersecurity exceptions primarily as individual decisions, or does it systematically evaluate their combined impact on critical business services and enterprise risk tolerance?
Who possesses authority when several individually approved exceptions collectively create an unacceptable exposure?
I am particularly interested in how organizations identify shared dependencies and concentrated risks across business units.
Because the fact that every cybersecurity exception was properly approved does not necessarily mean the enterprise risk created by those exceptions was ever authorized.
That is the difference between governing individual decisions and governing the organization.
#CybersecurityGovernance #ExecutiveAccountability #CyberRisk #RiskAcceptance #GRC #EnterpriseRiskManagement #NISTCSF #EvidentiaryArchitecture
2 reactions · 0 comments
Topics: #cyberrisk, #cybersecuritygovernance, #nistcsf, #executiveaccountability, #evidentiaryarchitecture, #riskacceptance, #grc, #enterpriseriskmanagement