Building PhilSIEM v2: My Own Home Security Monitoring Environment I’ve been building something I’m calling…
Building PhilSIEM v2: My Own Home Security Monitoring Environment
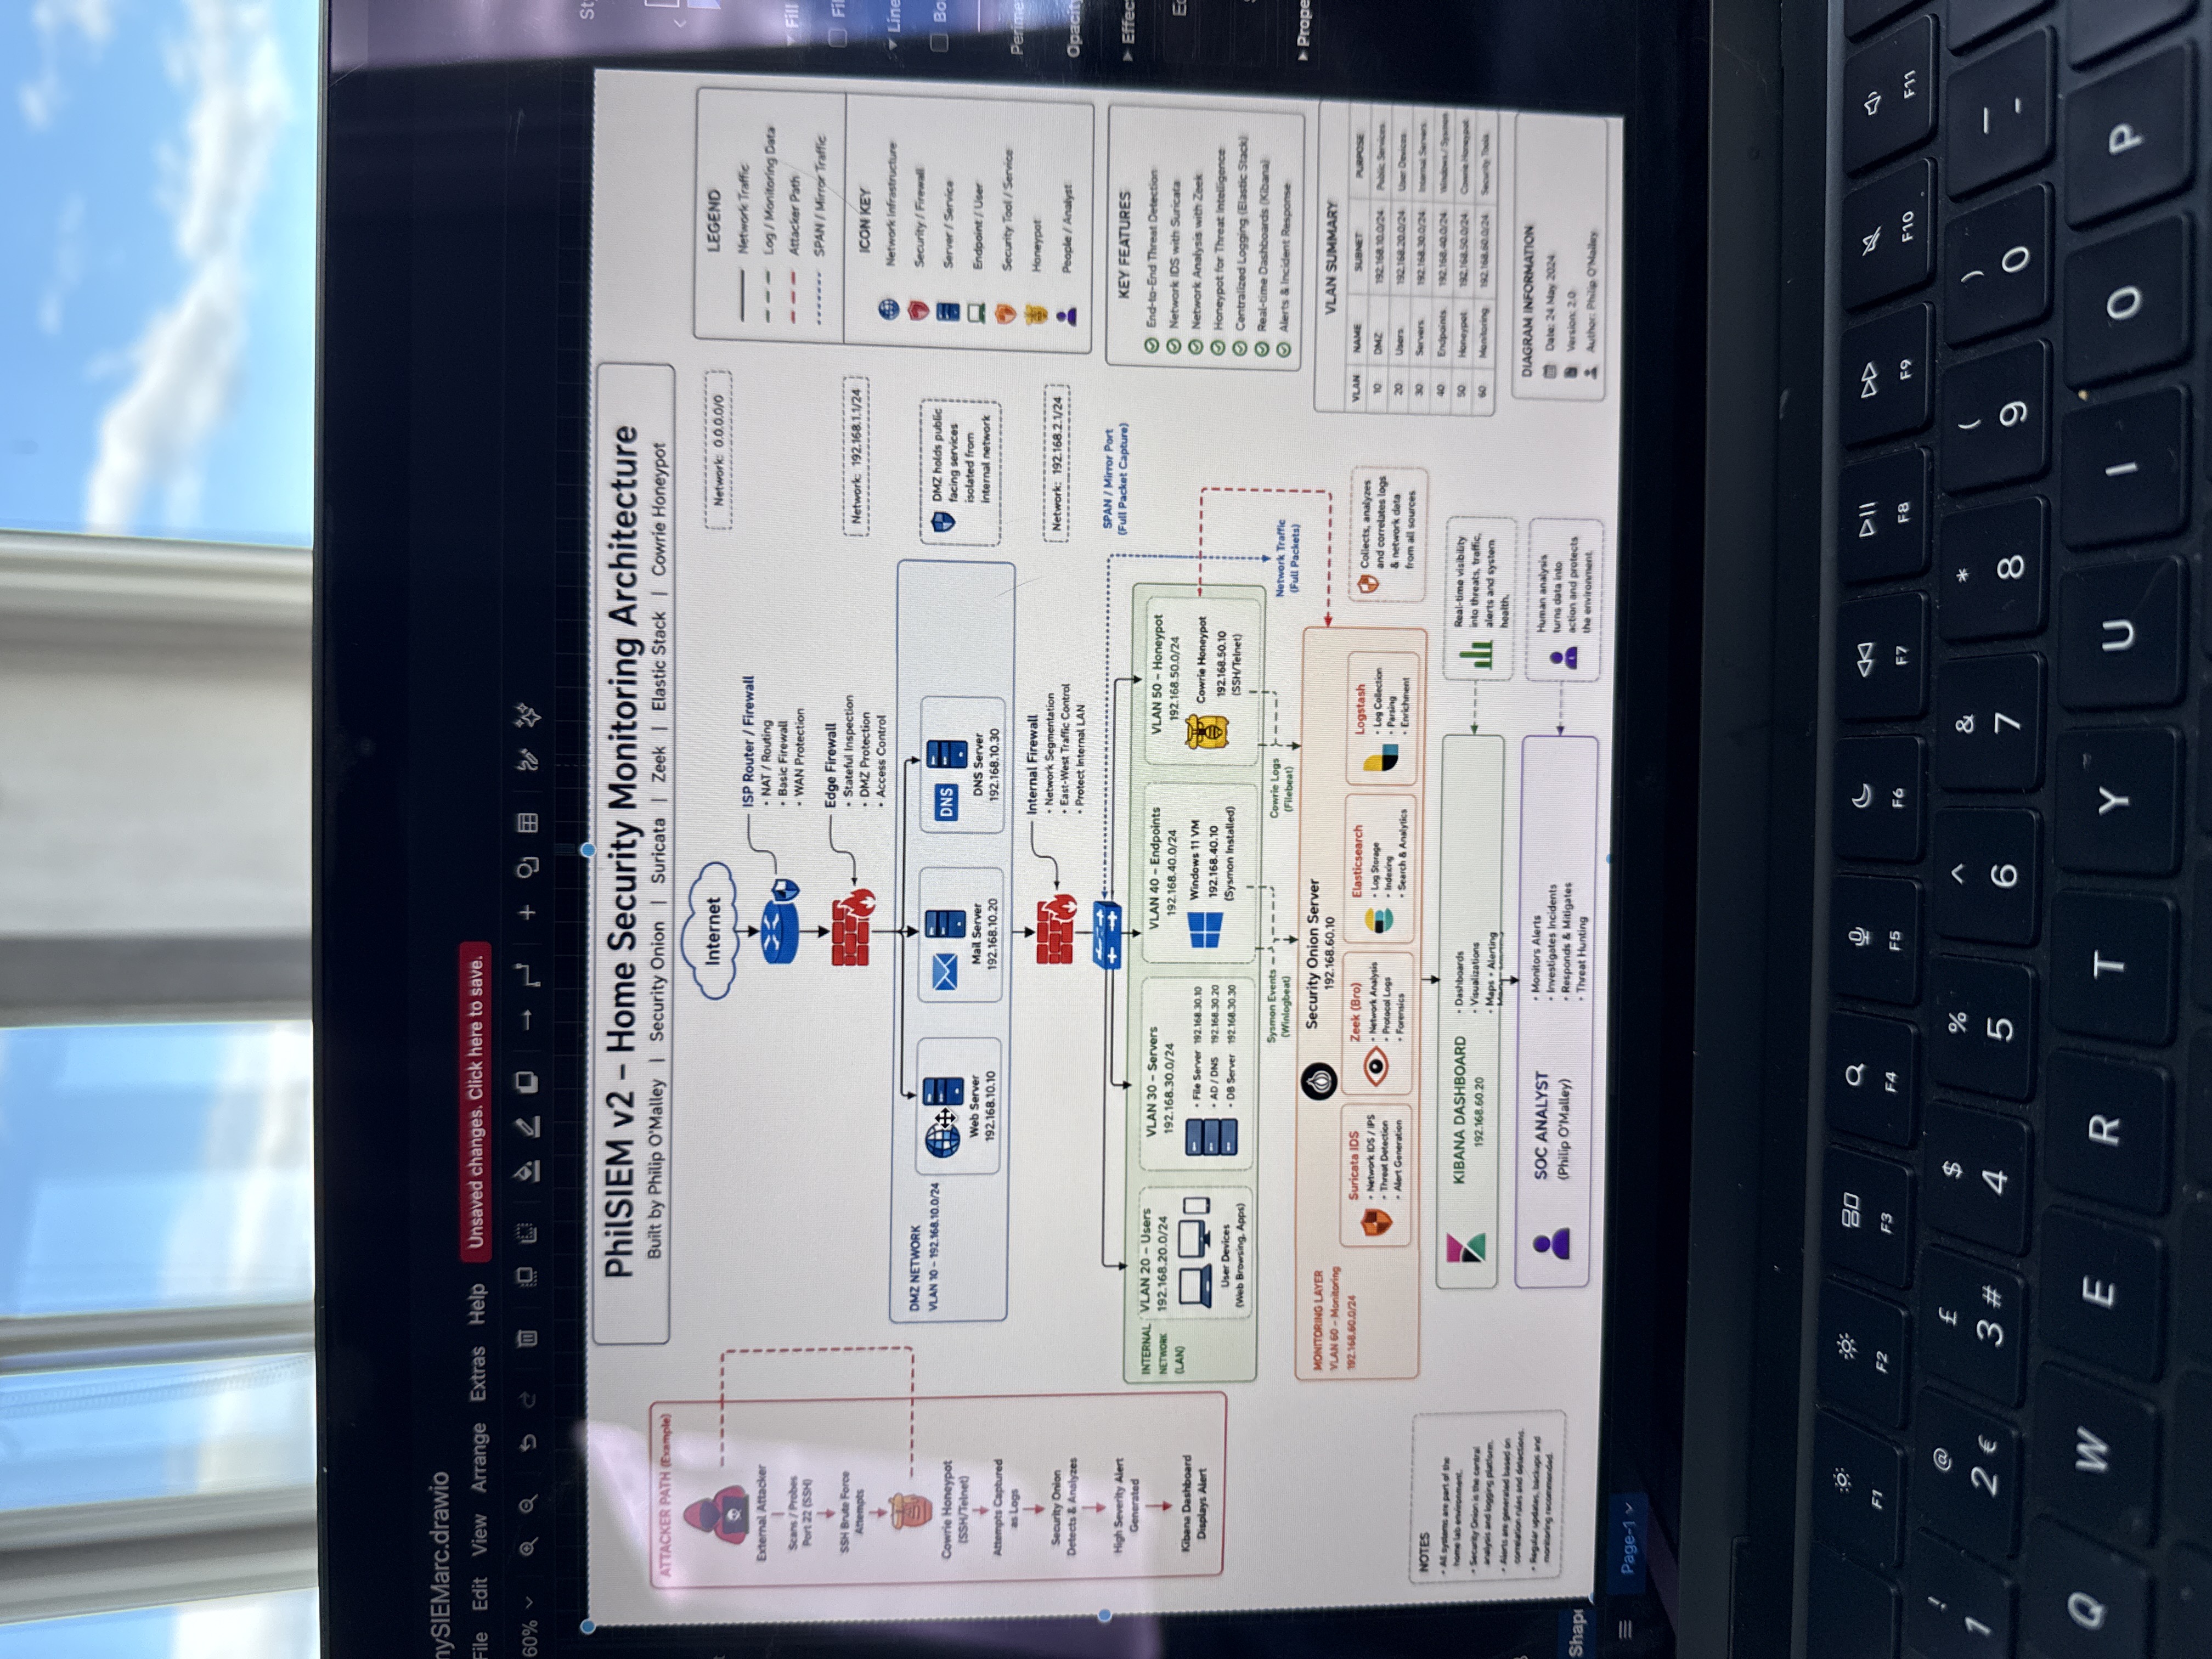
I’ve been building something I’m calling PhilSIEM v2, a home-based cybersecurity monitoring environment designed to simulate the sort of detection and response workflow you’d find in a SOC.
The idea is simple:
Don’t just build a network. Build a network you can monitor, attack, investigate and defend.
🌐 Internet → Firewalls → Network Segmentation
Different parts of the environment are separated into VLANs for users, servers, endpoints, monitoring and a dedicated honeypot.
🍯 Cowrie Honeypot
I’ve deliberately created an SSH honeypot to attract and capture malicious activity. This allows me to observe things such as scanning, brute-force attempts and attacker behaviour without exposing my real systems.
🛡️ Suricata
Acts as the detection layer, identifying suspicious and potentially malicious network activity.
👁️ Zeek
Provides deeper network visibility and helps answer questions such as:
Who communicated with whom?
When did it happen?
What protocols were involved?
What actually happened during the connection?
📊 Elastic Stack
Logstash collects and processes the data, Elasticsearch stores and indexes it, and Kibana provides dashboards, visualisation and alerting.
👨💻 SOC Analyst
And ultimately, that’s where I come in.
The goal isn’t to have technology simply throw alerts at me.
It’s to investigate those alerts, understand what happened, determine the severity, identify potential threats and decide on an appropriate response.
So, in simple terms:
Raw network activity → Detection → Logging → Analysis → Alert → Investigation → Response
That’s what PhilSIEM is about.
I’m building this as a practical way to develop the skills needed for a career in SOC analysis, threat detection and incident response, while creating something I can continuously expand and improve.
Better visibility → Faster detection → Stronger defence.
#CyberSecurity #SOC #SIEM #BlueTeam #ThreatDetection #IncidentResponse #NetworkSecurity #CyberSecurityCareer #HomeLab #Elastic #Suricata #Zeek #Kibana #PhilSIEM
3 reactions · 0 comments
Topics: #zeek, #blueteam, #kibana, #siem, #cybersecuritycareer, #suricata, #incidentresponse, #philsiem, #cybersecurity, #soc