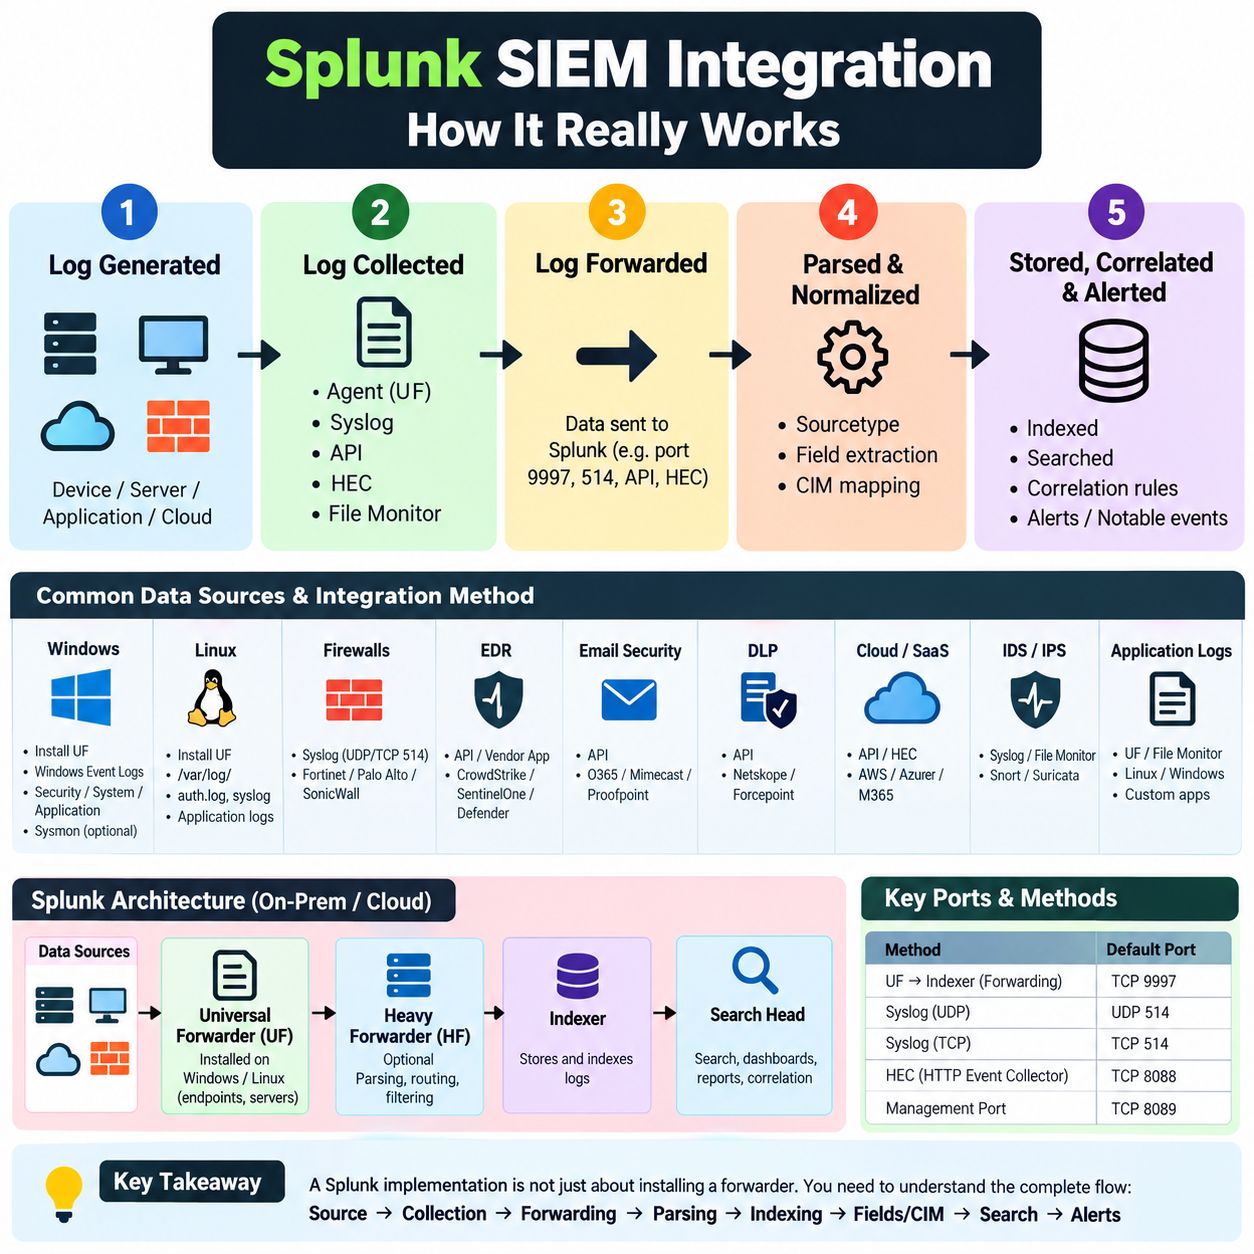
🔐 Splunk SIEM INTEGRATION Generate → Collect → Forward → Parse → Index → Normalize → Search → Alert ⚠️…
SHERIF E. — Cyber Security Analyst
🔐 Splunk SIEM INTEGRATION
Generate → Collect → Forward → Parse → Index → Normalize → Search → Alert
⚠️ Collection fails = Splunk is blind.
⚠️ Forwarding/parsing fails = Detection can fail.
🏗️ SPLUNK CORE
🔹 UF → Endpoint log collection
🔹 HF → Optional parsing/routing
🔹 Indexer → Receives amp; stores events
🔹 Search Head → SPL, dashboards amp; investigation
━━━━━━━━━━━━━━
🪟 1️⃣ WINDOWS / AD
📌 Install Splunk Universal Forwarder (UF) on the Windows server/DC.
⚙️ inputs.conf
[WinEventLog://Security]
disabled = 0
index = windows
📊 Collect: Security, System, Application, PowerShell, Sysmon
.➡️ Forward: UF → Indexer
🔌 Port: TCP 9997
🔎 Validate: Service → Connectivity → Index → Sourcetype → Events
━━━━━━━━━━━━━━
🐧 2️⃣ LINUX
📌 Install UF and monitor:
/var/log/auth.log
/var/log/secure
/var/log/syslog
⚙️ Example:[monitor:///var/log/auth.log]
index = linux
➡️ Forward: UF → Indexer
🚨 Detect: SSH brute force, failed authentication, privilege escalation
━━━━━━━━━━━━━━
🔥 3️⃣ FIREWALL
1️⃣ Set Splunk/Syslog receiver IP
2️⃣ Configure UDP/TCP 514
3️⃣ Configure Splunk input
4️⃣ Set index + sourcetype
5️⃣ Search amp; validate events
🔄 Flow: Firewall → Syslog → Splunk → Index → CIM → Detection
━━━━━━━━━━━━━━
🛡️ 4️⃣ EDR
❌ No UF on the cloud console.
1️⃣ Create API credentials
2️⃣ Install vendor App/Add-on
3️⃣ Enter API URL + ID/Secret/Token
4️⃣ Configure polling/ingestion
5️⃣ Set index + sourcetype
6️⃣ Validate events
🔄 Flow: EDR Cloud → API → Add-on → Index → CIM → Detection
━━━━━━━━━━━━━━
☁️ 5️⃣ CLOUD / SaaS
🔗 Methods: API / HEC / Add-on / Cloud integration
☁️ AWS: CloudTrail → S3 → Splunk → Index
1️⃣ Enable required logs
2️⃣ Configure IAM/API access
3️⃣ Configure Splunk input/Add-on
4️⃣ Set index + sourcetype
5️⃣ Validate events
━━━━━━━━━━━━━━
📧 6️⃣ EMAIL SECURITY
M365 / Mimecast / Proofpoint / Barracuda
1️⃣ Enable audit/security logs
2️⃣ Create API/App credentials
3️⃣ Configure Add-on/API input
4️⃣ Set index + sourcetype
5️⃣ Validate phishing, malware, spam amp; mail-flow events
━━━━━━━━━━━━━━
🛡️ 7️⃣ DLP
Netskope / Forcepoint / Purview
🔄 DLP → API/Connector → Splunk
🔐 API Auth → Add-on/Input → Polling → Index/Sourcetype → Fields → CIM
━━━━━━━━━━━━━━
🚨 8️⃣ IDS / IPS / WAF / PROXY
Snort / Suricata / F5 / Cloudflare / Web Proxies
🔗 Methods: Syslog / File Monitor / API / HEC
📁 Example: /var/log/snort/alert⚙️ Input → Index → Sourcetype → Fields → Detection
━━━━━━━━━━━━━━
📱 9️⃣ APPLICATION LOGS
🐧 Linux: /var/log/app/app.log
🪟 Windows: C:Applogsapp.log
1️⃣ Install UF
2️⃣ Configure file monitoring
3️⃣ Set index + sourcetype
4️⃣ Configure timestamp/line breaking
5️⃣ Validate fields amp; events
━━━━━━━━━━━━━━
🧩 🔟 PARSING → CIM → DETECTION
Raw Event → Sourcetype → Field Extraction → CIM → SPL → Correlation → Alert
━━━━━━━━━━━━━━
#Splunk #SplunkSIEM #SIEM #SPL #CIM #LogManagement #SIEMIntegration #SOC #SOCAnalyst #SOCOperations #DetectionEngineering #ThreatHunting #IncidentResponse #CyberSecurity #InfoSec #BlueTeam
COPIED
4 reactions · 0 comments
Topics: #blueteam, #threathunting, #logmanagement, #siem, #splunksiem, #infosec, #incidentresponse, #socanalyst, #cim, #siemintegration