Windows CLI Fundamentals: Host-Based Enumeration "I Just wrapped up a deep-dive into Windows Server Core…
OLUWATOYIN O. — Security Operations & Threat Analysis
Windows CLI Fundamentals: Host-Based Enumeration
"I Just wrapped up a deep-dive into Windows Server Core enumeration! 🛡️
As an aspiring SOC Analyst, mastering the CLI is non-negotiable. Today I focused on:
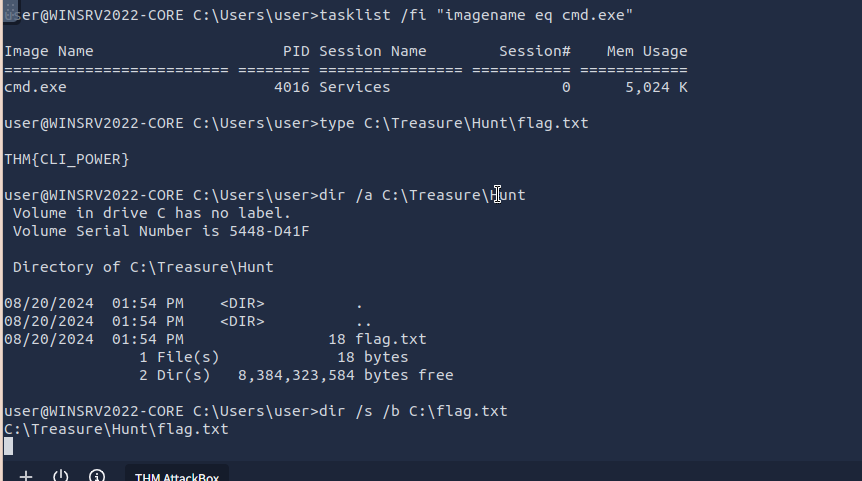
✅ Mapping active ports (RDP/RPC) to system services using netstat and tasklist.
✅ Isolating specific process IDs (PIDs) to audit system health.
✅ Navigating the file system to locate hidden sensitive data.
You can check out my full technical walkthrough and command breakdown on my GitHub: [Insert Your GitHub Link Here]
#Cybersecurity #SOCAnalyst #WindowsServer #ThreatHunting #BlueTeam #TorontoIT"
3 reactions · 0 comments
Topics: #blueteam, #threathunting, #torontoit, #socanalyst, #windowsserver, #cybersecurity