If there are no logs in Sentinel, you have zero visibility and zero detection. While building out my…
Ikechukwu O. — Security Operations Center (SOC) Analyst
If there are no logs in Sentinel, you have zero visibility and zero detection.
While building out my Microsoft Sentinel lab, I hit a critical wall: Windows Security Events simply stopped flowing. For any SOC analyst, this is a nightmare scenario where authentication activity, privilege escalations, and IOCs vanish into a black hole.
Here is how I diagnosed the failure and restored the pipeline:
🔎 The Resolution Path
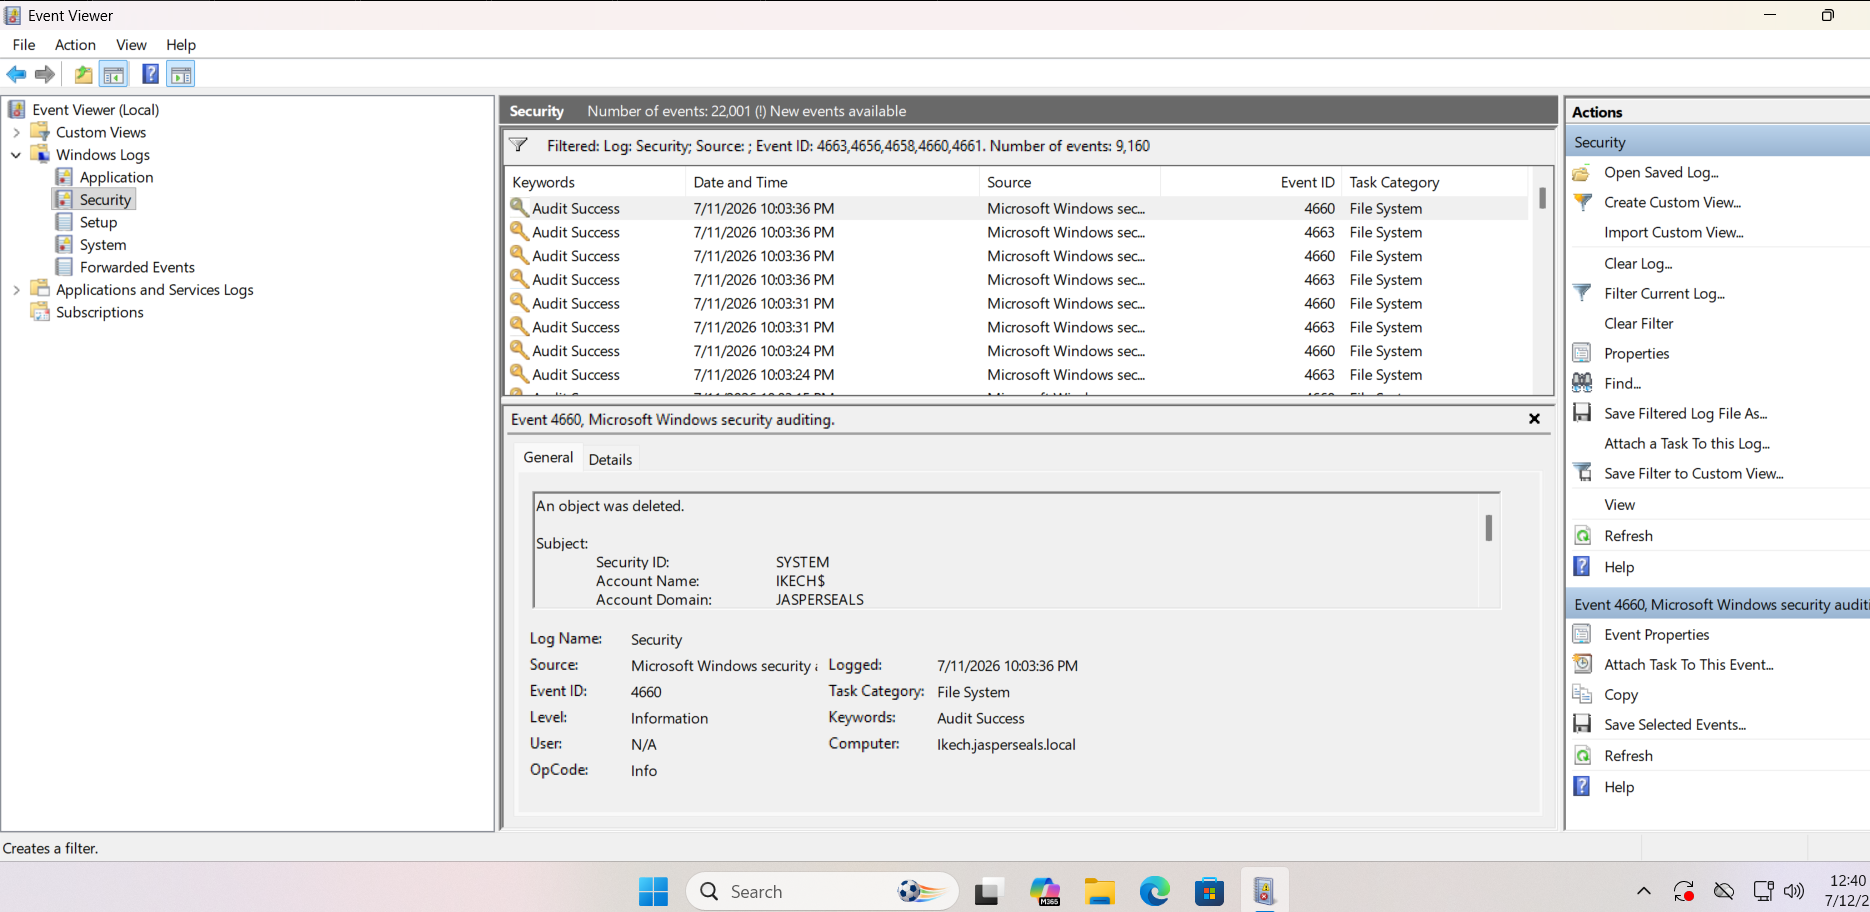
1️⃣ Validate the Source: I started by opening Windows Event Viewer on the VM. Local generation of events like 4624 (Logon) and 4625 (Failed Logon) was functioning perfectly, confirming the issue wasn't the OS.
2️⃣ Identify the Gap: I traced the telemetry upstream and found the Windows Security Events via Azure Monitor Agent (AMA) connector had lost its link to the Log Analytics workspace. The data existed but had no path to the cloud.
3️⃣ Re-engineer the Flow: I reconfigured the AMA connector, applied the correct Data Collection Rule (DCR), and successfully bridged the ingestion gap.
4️⃣ Verification: Within minutes, KQL queries for SecurityEvent IDs 4624, 4625, 4672, and 4798 confirmed that privileged logons and group enumerations were officially back on the radar.
✅ Key Takeaways for Defenders:
▶️ Systematic Diagnosis: Troubleshoot in layers (OS → Agent/Connector → Workspace) to isolate the failure point quickly.
▶️ Trust but Verify: Event Viewer is your source of truth. Always confirm logs exist locally before chasing phantom configurations in the portal.
▶️ Stealth Failures: A misconfigured AMA connector is a silent killer for SOC visibility. Regular health checks on ingestion heartbeats are non-negotiable.
This lab was a perfect exercise in troubleshooting high-stakes ingestion issues and ensuring SOC readiness-skills that are mandatory for securing enterprise environments.
#SOCAnalyst #MicrosoftSentinel #CyberSecurity #AzureSecurity #IncidentResponse #SC200
5 reactions · 0 comments
Topics: #incidentresponse, #socanalyst, #sc200, #microsoftsentinel, #cybersecurity, #azuresecurity