Posted in Threat Intelligence
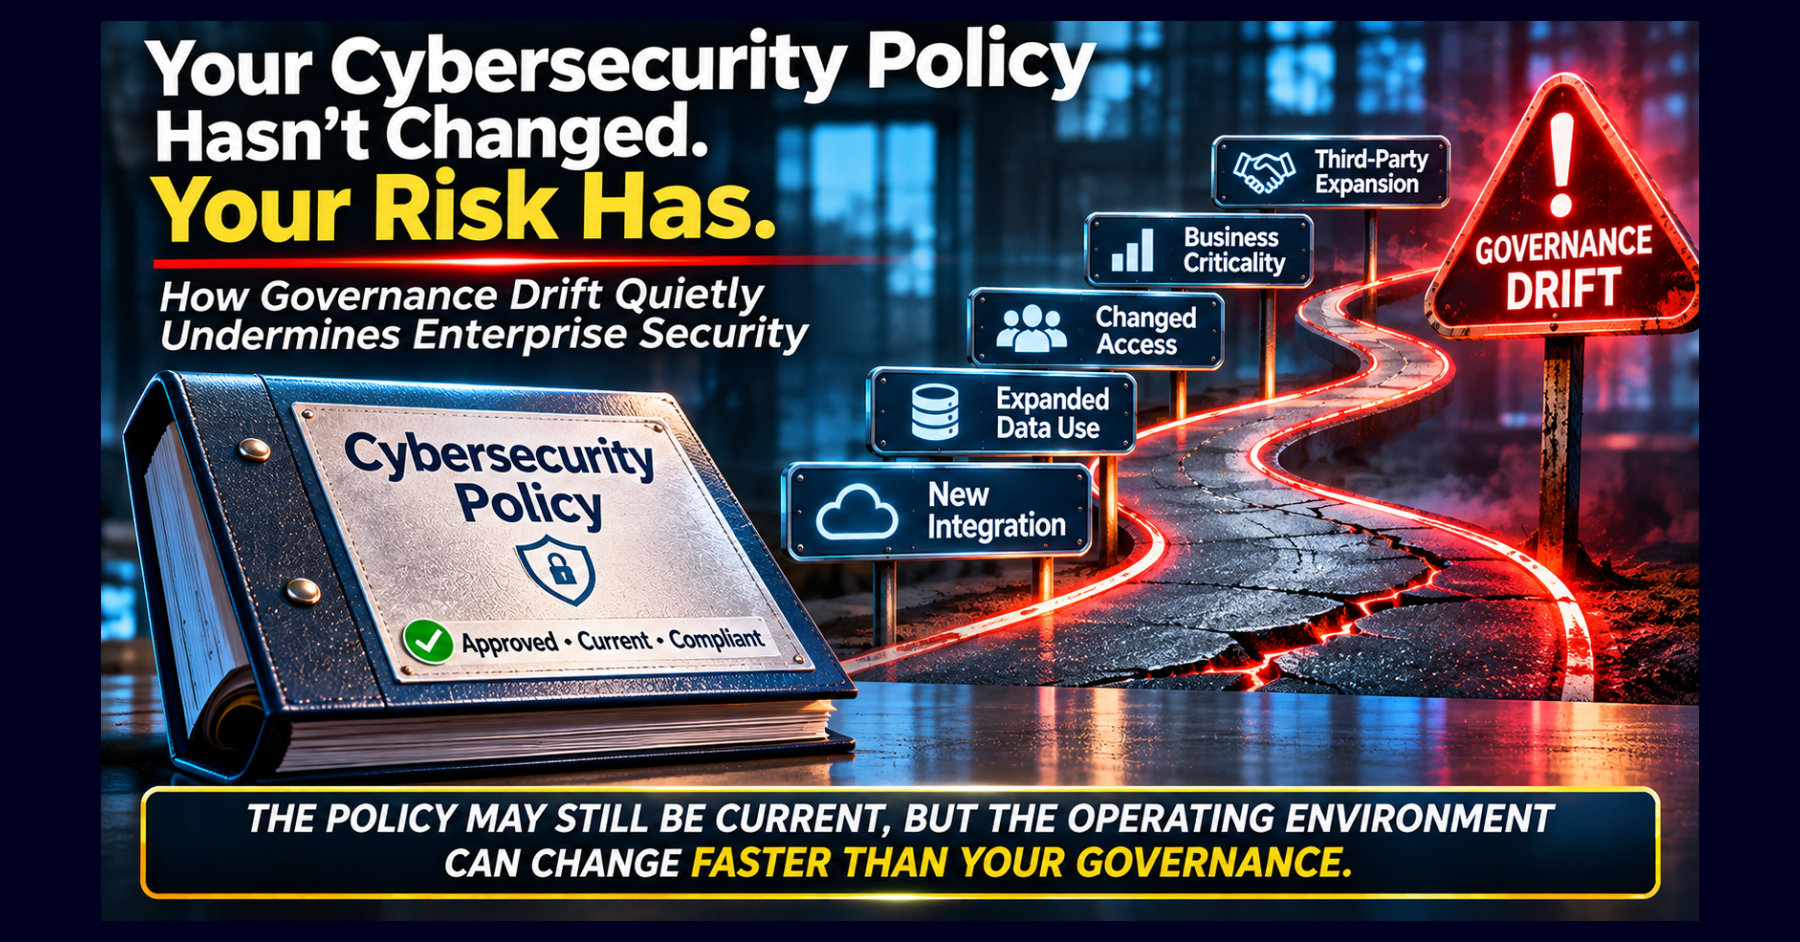
Your Cybersecurity Policy Hasn't Changed. Your Risk Has.
Victor Font — Keynote Speaker | Strategic Technology Leader | Fractional CIO | IT & Cyber Governance Expert | Published Author | FedRAMP Readiness | Board-Level Advisor | Digital Transformation | Enterprise WordPress/Formidable Forms
How Governance Drift Quietly Undermines Enterprise Security
Your organization has a cybersecurity policy.
It was reviewed by legal.
Approved by executive leadership.
Published to employees.
Mapped to applicable security standards.
Perhaps it was even updated within the past year.
The policy defines acceptable practices, assigns responsibilities, establishes control requirements, and describes how exceptions should be managed.
On paper, the organization appears well governed.
But something has changed.
A business unit has adopted a new cloud application.
An integration now exchanges sensitive information with an external service.
A privileged account has accumulated additional permissions.
A temporary exception has been extended several times.
A system originally classified as noncritical now supports an essential business process.
None of these changes necessarily required rewriting the cybersecurity policy.
Yet collectively, they may have transformed the organization's exposure.
The policy remains current. The operating environment has moved beyond the assumptions on which the policy was built.
That is governance drift.
And it can occur even when everyone believes they are following the rules.
Governance Drift Is Not the Same as Policy Noncompliance
When cybersecurity leaders hear that an organization has drifted from its established requirements, they often think about noncompliance.
Someone violated a policy.
A control was disabled.
An approval was bypassed.
A required review was missed.
Those are important issues.
But governance drift can be more subtle.
It occurs when the organization's actual operating conditions, decision practices, responsibilities, or risk exposure evolve without corresponding changes to the governance mechanisms intended to control them.
Consider a business application originally approved to process internal operational information.
At the time of approval, its security requirements were appropriate.
Two years later, the application has become integrated with customer systems, financial reporting platforms, and third-party analytics services.
Its business criticality has increased.
Its data sensitivity has changed.
Its external dependencies have expanded.
Yet its original risk classification remains unchanged.
The application may still comply with every control assigned to its original classification.
The organization has not necessarily violated its policy. It may have outgrown the governance decision that determined which policy requirements applied.
That distinction matters.
Because conventional compliance monitoring may not identify the problem.
The Danger of Decisions That Never Get Revisited
Every cybersecurity governance decision depends on assumptions.
A system is classified according to its expected use.
Access privileges are granted based on an employee's responsibilities.
A vendor is approved based on the services it will provide.
A security exception is accepted under defined conditions.
A control is selected because it is considered appropriate for a particular level of risk.
These decisions may be entirely reasonable when made.
But the enterprise does not remain static.
Employees change roles.
Applications gain capabilities.
Vendors introduce new services.
Business processes become more dependent on technology.
Threat conditions evolve.
And systems that were once peripheral become operationally essential.
The original governance decision may remain documented long after its underlying assumptions have changed.
This creates a dangerous condition.
The organization continues enforcing a decision that was appropriate for yesterday's environment without determining whether it remains appropriate today.
The problem is not necessarily that the original decision was wrong.
The problem is that nobody recognized when it needed to be reconsidered.
A Familiar Example: Privileged Access
Imagine an employee who joins an organization as a systems administrator.
The employee receives privileged access to several infrastructure platforms.
The access is appropriate for the assigned responsibilities.
Over time, the employee moves into an architecture role.
Then into project management.
Eventually, the employee becomes a business technology advisor.
The original administrative responsibilities disappear.
But some privileged permissions remain.
Periodic access reviews occur.
Managers certify that access is appropriate.
The identity management system records successful completion of the review.
The compliance dashboard remains green.
Yet the employee retains permissions that are no longer necessary.
How does this happen?
Perhaps the reviewing manager does not understand the technical significance of the permissions.
Perhaps the access certification process emphasizes completion rather than meaningful evaluation.
Perhaps nobody connects changes in job responsibilities to the original justification for granting access.
The organization has a functioning access review process.
What it may lack is an effective mechanism for detecting when the rationale for access has become obsolete.
The review was completed. The underlying entitlement decision was never meaningfully reconsidered.
That is governance drift in practice.
Cloud Services Make Drift Easier to Miss
Modern enterprise environments change continuously.
Cloud platforms introduce new capabilities.
Software-as-a-service applications expand their integrations.
Infrastructure is provisioned and modified through automation.
AI-enabled services acquire access to enterprise data.
Third-party providers change their operating models.
These changes can occur much faster than traditional governance review cycles.
Consider a cloud application initially approved for a narrow business function.
Over time, employees enable additional integrations.
The application begins receiving more sensitive information.
New automation workflows are introduced.
An AI feature is activated.
The service's operational importance increases.
Each individual change may appear minor.
But the cumulative effect may be substantial.
The original security assessment may no longer describe the system's actual risk profile.
The vendor approval may no longer reflect the services being consumed.
The data governance classification may no longer match the information being processed.
And the business owner may not realize that the application's risk characteristics have materially changed.
Governance drift frequently emerges through the accumulation of individually reasonable changes.
No single event appears significant enough to trigger a comprehensive reassessment.
The combined result, however, can invalidate the original governance assumptions.
Why Annual Reviews Are Not Enough
Many organizations rely on scheduled reviews to maintain cybersecurity governance.
Policies are reviewed annually.
Vendor assessments are refreshed periodically.
Access certifications occur quarterly or semiannually.
Risk registers are updated according to established schedules.
These activities are necessary.
But a calendar is not a reliable indicator of when risk conditions change.
A critical business application can acquire a new external dependency the day after its annual assessment.
A privileged account can become inappropriate immediately after an employee changes responsibilities.
A vendor can introduce a material service change between scheduled reviews.
A previously accepted vulnerability can become actively exploited long before its next renewal date.
If governance depends exclusively on periodic review, the organization may operate for extended periods under outdated assumptions.
The solution is not to eliminate scheduled reviews.
It is to supplement them with event-driven reassessment.
Governance should respond to material changes in operating conditions, not merely the passage of time.
That requires identifying which events should trigger renewed evaluation.
Five Signals That Governance May Be Drifting
Organizations can begin detecting governance drift by examining five categories of change.
1. Changes in business criticality
Has a system become more important to revenue, customer service, safety, regulatory obligations, or operational continuity than it was when originally assessed?
2. Changes in access and authority
Do current permissions, delegated authorities, and approval rights still reflect the responsibilities of the people and systems exercising them?
3. Changes in data exposure
Are applications processing more sensitive information, exchanging data with additional parties, or supporting new uses that were not considered during initial approval?
4. Changes in technical dependencies
Have new integrations, cloud services, automation platforms, or third-party relationships altered the organization's exposure?
5. Changes in risk assumptions
Have threat intelligence, business conditions, compensating controls, or regulatory requirements changed enough to invalidate earlier decisions?
These signals do not automatically establish that governance has failed.
They establish that a previous decision may require reconsideration.
The objective is to detect that need before an incident reveals it.
The Missing Connection Between Change Management and Governance
Enterprise change management traditionally focuses on controlling modifications to systems and services.
A change is requested.
Its technical and operational impact is evaluated.
Approvals are obtained.
Implementation occurs.
Results are reviewed.
But not every technical change receives an equally rigorous assessment of its governance implications.
A new integration may be technically successful while expanding the organization's third-party exposure.
A cloud configuration change may improve performance while altering data residency or access boundaries.
An automation initiative may reduce manual work while transferring consequential decisions from employees to software.
A system upgrade may introduce capabilities that exceed the scope of the original security assessment.
These changes are not necessarily inappropriate.
But they may require new decisions about risk ownership, control requirements, decision authority, or assurance.
A technically successful change can still produce an unrecognized governance consequence.
This is why cybersecurity governance must be connected to enterprise architecture, identity management, data governance, procurement, and change management.
Otherwise, the organization may approve changes individually without understanding their cumulative effect on enterprise risk.
Evidentiary Architecture™ and Decision Validity
This problem illustrates another important application of Evidentiary Architecture™.
Traditional governance records often preserve evidence that a decision was made.
An application was approved.
A vendor was assessed.
Access was authorized.
A risk was accepted.
Those records establish historical facts.
But defensible governance requires more than preserving the original decision.
It requires understanding whether the decision remains valid under current conditions.
That means connecting governance decisions to the assumptions and dependencies supporting them.
A useful evidence chain follows this sequence:
Decision authorized → Assumptions documented → Dependencies identified → Conditions monitored → Material change detected → Decision reassessed → Evidence preserved.
The essential capability is traceability.
When an application changes, the organization should be able to identify which governance decisions may be affected.
When a business dependency expands, the relevant risk classification should be reconsidered.
When an employee's responsibilities change, access decisions should be evaluated against current requirements.
When a vendor introduces a material capability, the organization should determine whether the original assessment remains sufficient.
This does not require a full governance review every time someone changes a configuration setting.
It requires proportionate, risk-based mechanisms for recognizing when a change affects the basis of an earlier decision.
The goal is to preserve the validity of governance decisions—not merely the records proving they once existed.
The Executive Accountability Problem
Governance drift raises a difficult accountability question.
Who is responsible for recognizing that a previously approved decision is no longer appropriate?
The original decision-maker?
The current business owner?
The cybersecurity team?
Enterprise architecture?
Risk management?
The individual who approved the latest technical change?
In many organizations, responsibility is fragmented.
Each function monitors the conditions within its own area.
But no single function may be responsible for evaluating whether changes across those areas have invalidated the original governance decision.
This creates an accountability gap.
The security team may believe the business owner is responsible for reporting changes in criticality.
The business owner may assume IT will identify new technical dependencies.
IT may assume security will evaluate any resulting risk.
Risk management may rely on periodic assessments to capture material changes.
Everyone performs their assigned responsibilities.
Yet the enterprise continues operating under outdated assumptions.
Governance drift thrives where accountability for detecting change is distributed but accountability for reassessing decisions is undefined.
That is not merely a technical monitoring problem.
It is a governance architecture problem.
What Boards Should Be Asking
Boards do not need to review individual configuration changes or application integrations.
But they should seek assurance that management can detect material changes affecting the organization's cybersecurity risk profile.
Consider several questions.
How does management identify when previously approved risk decisions are no longer valid?
What events trigger reassessment outside scheduled review cycles?
How are changes in business criticality reflected in cybersecurity control requirements?
Who is accountable for evaluating the cumulative effects of technical and operational changes?
How does the organization verify that its risk register reflects current conditions rather than historical assumptions?
And perhaps most importantly:
How does management know when the enterprise has changed faster than its governance processes?
A cybersecurity dashboard may show that policies are current and required reviews are complete.
Those indicators are useful.
But they do not necessarily establish that governance decisions remain appropriate for the organization as it operates today.
The Policy Is Not the Enterprise
Organizations sometimes treat cybersecurity governance as a collection of approved documents.
Policies.
Standards.
Procedures.
Risk registers.
Control matrices.
Approval records.
These artifacts are necessary.
But they are representations of governance, not governance itself.
The enterprise is constantly changing.
Its systems evolve.
Its people move.
Its dependencies expand.
Its business priorities shift.
Its exposure changes.
Governance must remain connected to those realities.
Otherwise, the organization can become increasingly compliant with a model of the enterprise that no longer exists.
That is the central danger of governance drift.
The organization may continue following its established rules while the conditions that made those rules appropriate have fundamentally changed.
The Question Every CISO Should Ask
Select one business-critical application that has been operating for several years.
Retrieve its original security assessment.
Examine the assumptions that supported its approval.
Then compare those assumptions with the application's current operating environment.
Does it process the same information?
Does it support the same business functions?
Does it have the same external dependencies?
Are its users and privileged access requirements unchanged?
Does its original risk classification still reflect its importance to the enterprise?
Have its governance decisions been reconsidered as those conditions evolved?
If the answers reveal significant differences, the organization may have discovered governance drift.
Not necessarily because anyone violated a policy.
But because the enterprise changed while the governance model remained anchored to an earlier reality.
The most dangerous cybersecurity policy may not be the one your organization ignores. It may be the one everyone follows faithfully—even though the assumptions behind it are no longer true.
Discussion
Think about a system, application, or business process in your organization that has evolved significantly since its original security assessment.
Who is responsible for recognizing when those changes invalidate the original governance decision?
Is reassessment automatically triggered by material changes, or does your organization depend on someone noticing the problem during the next scheduled review?
And if every required review is completed on time, how confident are you that your governance decisions still reflect the enterprise as it actually operates today?
#CybersecurityGovernance #GovernanceDrift #CyberRisk #EnterpriseArchitecture #RiskManagement #SecurityAssurance #GRC #EvidentiaryArchitecture
2 reactions · 0 comments
Topics: #governancedrift, #cyberrisk, #cybersecuritygovernance, #evidentiaryarchitecture, #riskmanagement, #enterprisearchitecture, #grc, #securityassurance