Posted in Threat Intelligence
LiveResponse-NG v0.20.0 is out, and it was built for one target: my own C2. Project Lattice is the…
jp101216 — Security Engineer | Offensive Security Research & Custom C2 Tooling
LiveResponse-NG v0.20.0 is out, and it was built for one target: my own C2.
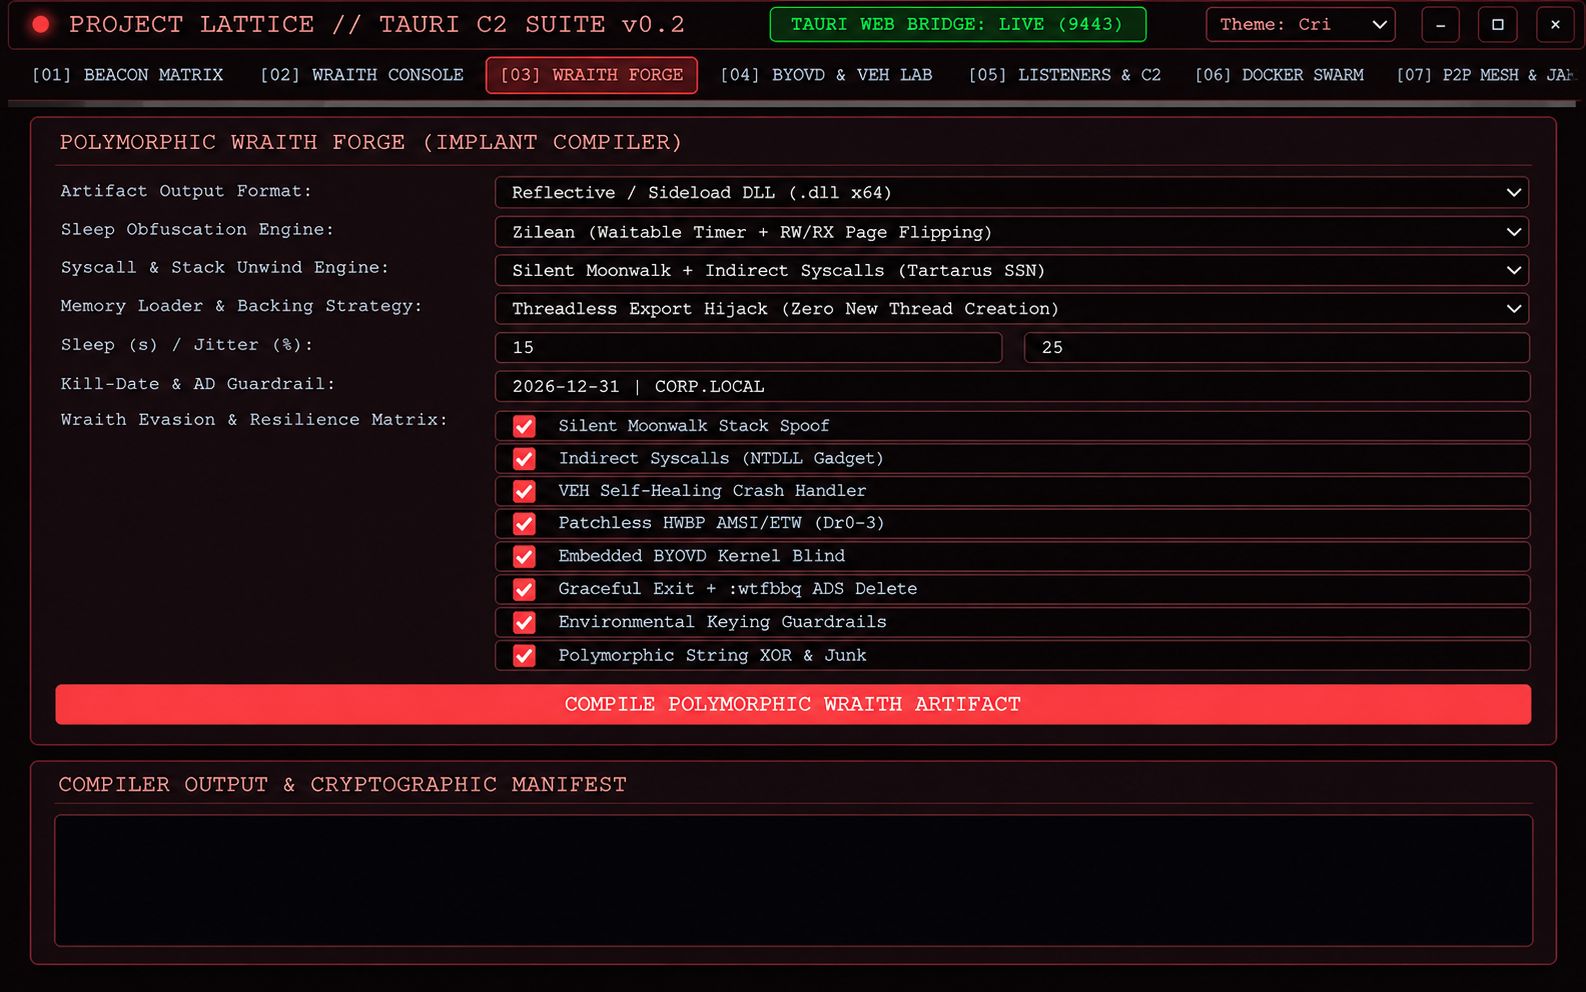
Project Lattice is the adversary-emulation C2 I'm building (Wraith implant in Rust, Go team server, Tauri console). The screenshot is the Wraith Forge, where each build picks its evasion. This release puts a detection behind every one of those boxes:
• Stack spoofing, including call-preceded gadgets
• Indirect syscalls, and LSASS opened through them
• Zilean sleep masking, threadless hooks, VEH self-healing
• Patchless hardware-breakpoint AMSI/ETW bypasses
• BYOVD driver loads, and PPL stripped from LSASS
• Self-deletion through an NTFS stream rename
• Stolen tokens, execute-assembly, LDAP enumeration, DoH, SOCKS listeners
• The Wraith agent itself, by its own strings, on Windows and Linux
The few things a user-mode tool can't see (kernel callback tampering, environmental keying) are documented as out of reach, not skipped.
The C2 stays private. The detections are open source.
github.com/jp101216/LiveResponse-NG/releases/tag/v0.20.0
#DetectionEngineering #PurpleTeam #AdversaryEmulation #DFIR
4 reactions · 0 comments
Topics: #adversaryemulation, #dfir, #purpleteam, #detectionengineering