You do not need a full-time CISO until you do. By then, the regulator is already knocking. This week, I saw…
Mark C. — Executive Technology & Cyber Leader | CIO | Cyber, Governance & Operational Resilience
You do not need a full-time CISO until you do. By then, the regulator is already knocking.
This week, I saw a classic (but wholly avoidable) example of why small, high-risk organisations desperately need fractional technical governance.
An organisation in a highly regulated sector was interviewing for a senior technology role.
𝗧𝗵𝗲 𝘁𝗮𝘀𝗸 𝘁𝗵𝗲𝘆 𝘀𝗲𝗻𝘁 𝗺𝗲: A questionnaire on how I'd rapidly fix a low-maturity IT setup ahead of an unannounced regulatory inspection - obviously a simulation.
𝗧𝗵𝗲 𝗶𝗿𝗼𝗻𝘆: The email was sent as a mass blast with every candidate's email address exposed in the open "To" field.
This is a clear UK GDPR breach. It leaked the contact details and the job-seeking intentions of an entire group of industry peers.
This isn't just an administrative slip-up. It is a symptom of a deeper structural 𝗳𝗮𝗶𝗹𝘂𝗿𝗲:
𝗣𝗿𝗼𝗰𝗲𝘀𝘀 𝗼𝘃𝗲𝗿 𝗽𝗼𝗹𝗶𝗰𝘆: You can write all the data protection policies you want. Without a tech leader enforcing guardrails, like blocking mass external emails via standard mail clients. Staff will default to the easiest path.
𝗧𝗵𝗲 𝗵𝗶𝗱𝗱𝗲𝗻 𝗰𝗼𝘀𝘁 𝗼𝗳 𝗱𝗲𝗹𝗮𝘆𝗶𝗻𝗴: Companies wait to hire a CIO or CISO because they think they are too small to justify the salary. Meanwhile, an untrained staff member can trigger a data breach or an adverse inspection rating in five seconds.
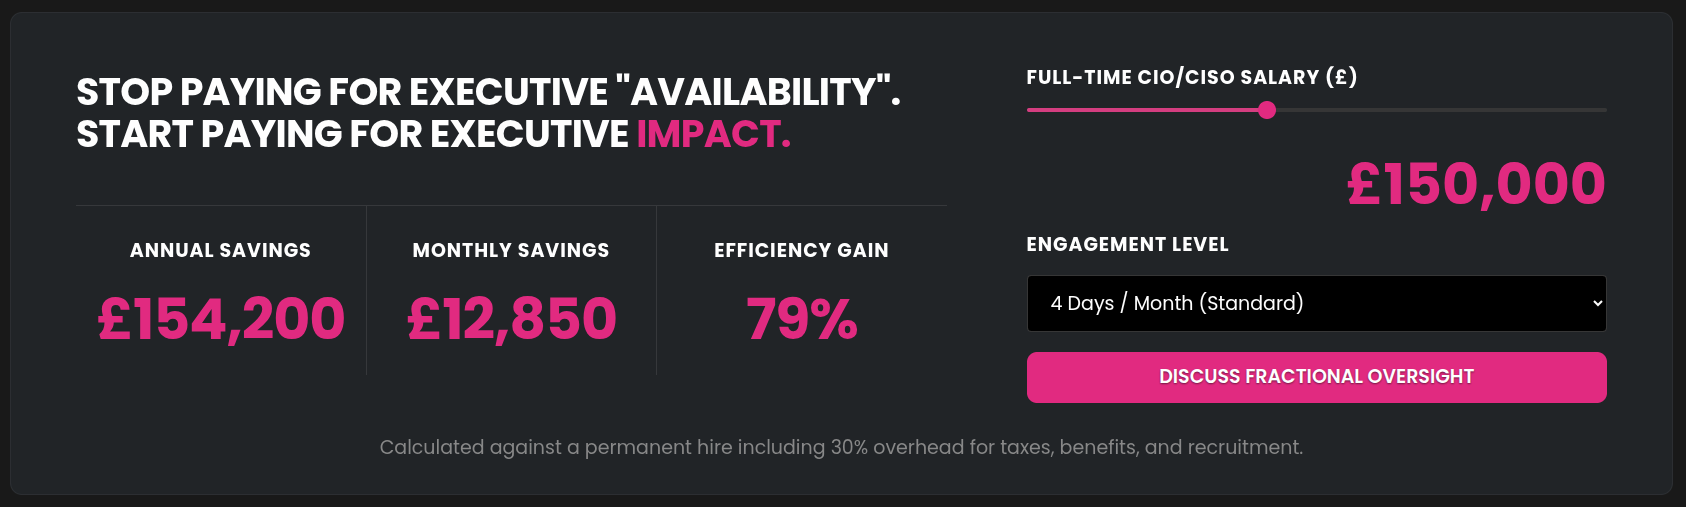
𝗧𝗵𝗲 𝗰𝗮𝘀𝗲 𝗳𝗼𝗿 𝗳𝗿𝗮𝗰𝘁𝗶𝗼𝗻𝗮𝗹 𝗹𝗲𝗮𝗱𝗲𝗿𝘀𝗵𝗶𝗽: You do not always need a six-figure permanent hire on day one. A fractional expert working a few days a month can audit workflows, lock down endpoints, and train your team.
If your hiring process for a tech leader actively breaches data regulations, your daily operations are likely doing it too.
Do not wait for a regulatory failure or an embarrassing data leak to fix your governance.
If you cannot afford a full-time security leader, look at an interim or fractional one before the choice is taken out of your hands.
7 reactions · 0 comments