I’m an offensive security researcher focused on automation, API security, and autonomous attack workflows…
Damian K. — Penetration Tester / Offensive Security Engineer
I’m an offensive security researcher focused on automation, API security, and autonomous attack workflows. My work combines penetration testing with engineering-oriented thinking — building scalable offensive systems rather than relying solely on manual testing.
I’m especially interested in agentic pentesting, exploit chaining, behavioral analysis, and graph-based attack reasoning. I enjoy solving complex security problems that require both offensive intuition and practical engineering.
I thrive in fast-moving research environments where experimentation, prototyping, and pushing technical boundaries are part of the culture.
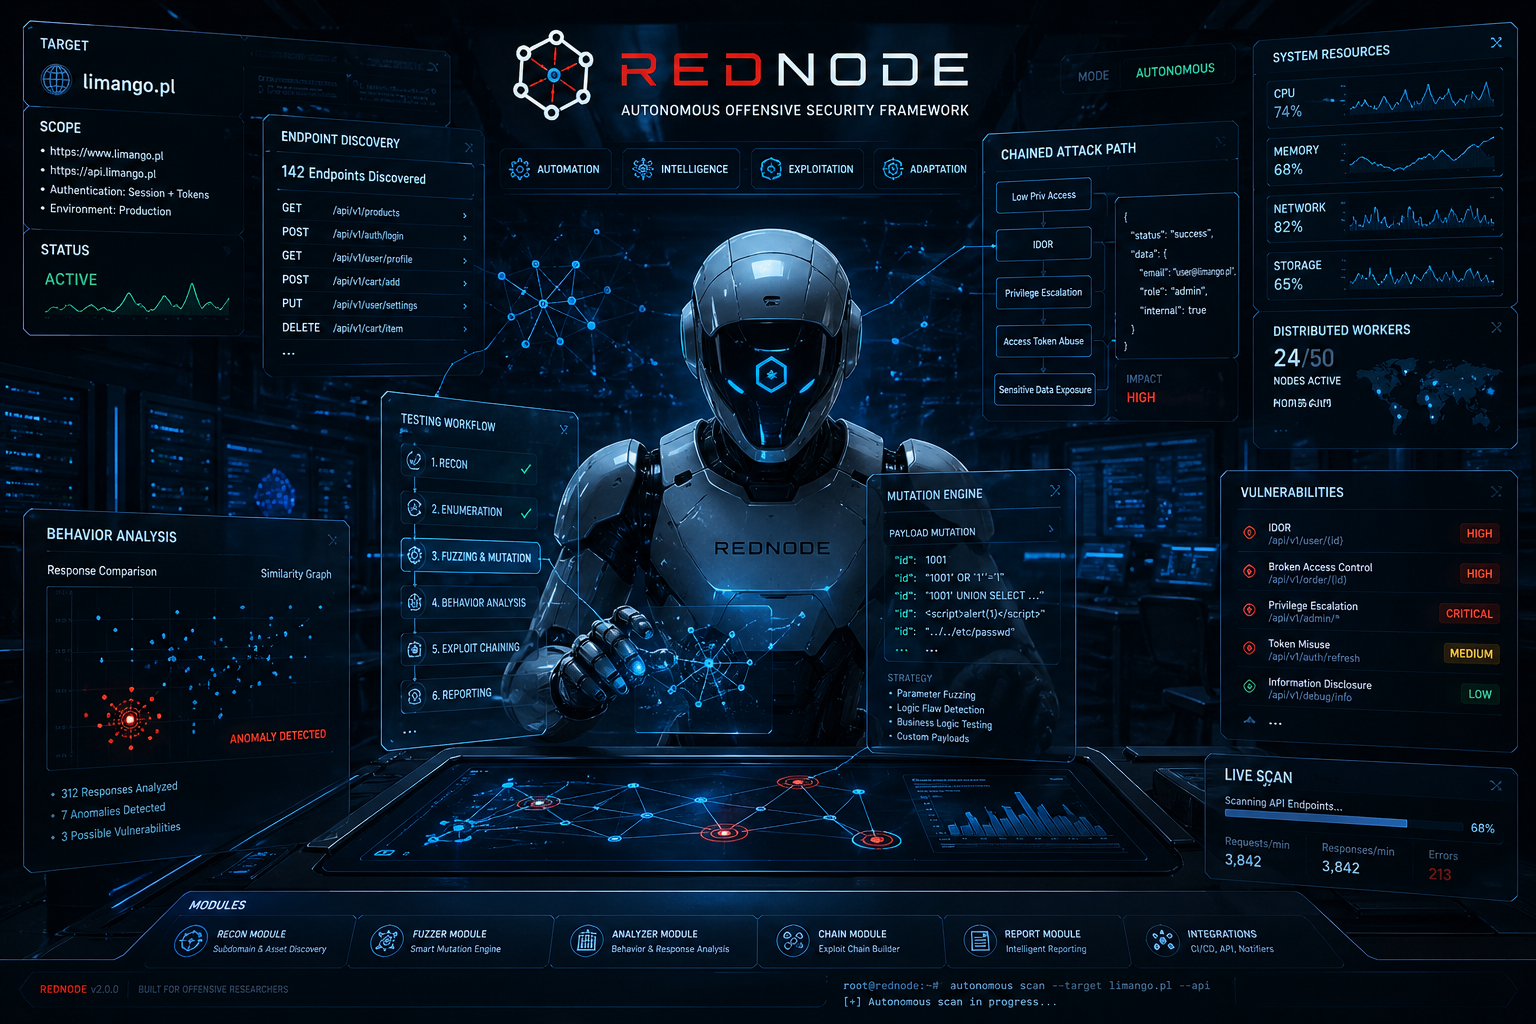
My biggest ongoing project is RedNode — a custom offensive security framework focused on autonomous application and API security testing.
I designed RedNode as a modular offensive automation platform capable of replaying, mutating, and analyzing authenticated application workflows at scale. The framework combines API fuzzing, behavioral analysis, attack surface extraction, and exploit-oriented workflow automation into a unified offensive research environment.
Through RedNode, I explore how autonomous systems can move beyond traditional vulnerability scanning toward context-aware offensive workflows capable of adaptive testing, exploit chaining, and autonomous security reasoning.
The project reflects my long-term focus on offensive automation, agentic pentesting, and scalable security research engineering.
4 reactions · 0 comments